


Showing 361–379 of 379 reports
Vibe Coding Gone Wrong: Moltbook AI Social Network Exposes 4.75 Million Records in Massive Database Breach
Google-owned Wiz discovers 4.75 million exposed records in AI social network Moltbook, including 1.5M API tokens and plaintext OpenAI keys—all because Row Level Security was never enabled on the “vibe-coded” platform.
BreachForums Breach Exposes 324,000 Cybercriminal Identities in Unprecedented Dark Web Leak
The tables have turned: BreachForums, one of the largest dark web marketplaces for stolen data, has been breached. A disgruntled insider leaked the real identities of nearly 324,000 cybercriminals, including email addresses, IP addresses, and connections to notorious groups like
SonicWall Cloud Breach Enables Ransomware Attack on 74 US Banks and Credit Unions
State-sponsored hackers exploited SonicWall’s MySonicWall cloud breach to launch a ransomware attack affecting 74 US banks and credit unions, compromising data of over 400,000 individuals. The attack demonstrates how third-party security breaches can cascade into devastating down
Nike Investigates 1.4 TB Data Leak After World Leaks Ransomware Gang Posts Stolen Files
Nike confirms it is investigating a potential breach after the World Leaks ransomware gang claimed to have stolen 1.4 TB of corporate data. The group, a rebrand of Hunters International, has targeted major organizations including the U.S. Marshals Service and Tata Technologies.
WinRAR CVE-2025-8088: Russia, China, and Cybercriminals Unite to Exploit Path Traversal Flaw
Google Threat Intelligence reveals widespread exploitation of CVE-2025-8088 by Russian APT groups, Chinese actors, and cybercriminals. The WinRAR path traversal flaw enables payload delivery via the Windows Startup folder, with active campaigns targeting Ukraine, LATAM, and finan
Microsoft to Disable 30-Year-Old NTLM Authentication Protocol by Default
Microsoft announces NTLM will be disabled by default in upcoming Windows releases, marking the end of the 30-year-old authentication protocol that has been a persistent security vulnerability.
Ivanti Patches Two Critical EPMM Zero-Day Vulnerabilities Under Active Exploitation
Two critical CVSS 9.8 vulnerabilities in Ivanti Endpoint Manager Mobile (CVE-2026-1281, CVE-2026-1340) are under active exploitation, allowing unauthenticated remote code execution. CISA has added them to the KEV catalog with a February 1 federal deadline.
Ivanti EPMM Zero-Days Actively Exploited: Pre-Auth RCE via Bash Arithmetic Expansion
Two actively exploited pre-auth RCE vulnerabilities (CVE-2026-1281 and CVE-2026-1340) in Ivanti Endpoint Manager Mobile allow attackers to execute arbitrary commands via Bash arithmetic expansion. CISA has added these to the KEV catalog.
SmarterMail Fixes Critical Unauthenticated RCE Flaw with CVSS 9.3 Score
SmarterTools patches critical CVE-2026-24423 (CVSS 9.3) unauthenticated RCE vulnerability in SmarterMail email server. Two other flaws including one under active exploitation also addressed. Update immediately.
SolarWinds Fixes Six Critical Web Help Desk Vulnerabilities Including RCE and Auth Bypass
SolarWinds patches six severe vulnerabilities in Web Help Desk, including four critical flaws (CVSS 9.8) enabling unauthenticated remote code execution and authentication bypass. Organizations should update to WHD 2026.1 immediately.
Fortinet Blocks Actively Exploited FortiCloud SSO Zero-Day Until Patch is Ready
Fortinet confirms CVE-2026-24858, a critical FortiCloud SSO authentication bypass zero-day actively exploited in the wild. The company has blocked FortiCloud SSO from vulnerable devices while patches are being developed.
Critical Microsoft Office Vulnerabilities Exploited in Latest Cyber Threat Campaign
Security researchers have identified sophisticated attack vectors leveraging Microsoft Office documents to bypass security measures and deliver malicious payloads. Learn about the latest threats and defensive strategies.
THIS WEEK IN SECURITY: LOOP DOS, FLIPPER RESPONDS, AND MORE!
by: Jonathan Bennett Here’s a fun thought experiment. UDP packets can be sent with an arbitrary source IP and port, so you can send a packet to one server, and could aim the response at another server. What happens if that response triggers another response? What if you could cra
Tool of First Resort: Israel-Hamas War in Cyber
Feb 14, 2024 | 4 min read | Sandra Joyce | Shane Huntley READ ARTICLE Cybersecurity plays a critical role in geopolitics — particularly during times of conflict. While offensive cyber operations have become nearly universal, the tactics, timing and objectives of threat actors can
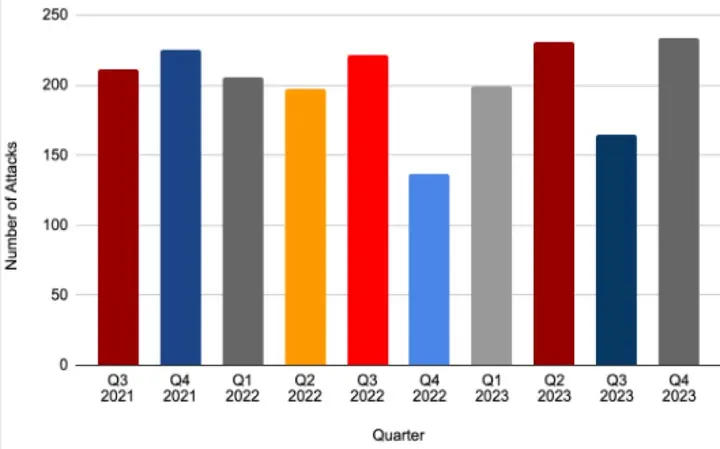
Flash Report: LockBit Ends 2023 with Record Number of Attacks
Read Article Key Findings
Hacked in China
Read Article foreign government’s response to a U.S. strategy document rarely earns front page coverage, but in the case of the Chinese Communist Party’s (CCP) recent reaction to the U.S. government’s new cyber strategy, we should all be paying attention. Tensions continue to esc
Financially motivated threat actors misusing App Installer
Read Article Since mid-November 2023, Microsoft Threat Intelligence has observed threat actors, including financially motivated actors like Storm-0569, Storm-1113, Sangria Tempest, and Storm-1674, utilizing the ms-appinstaller URI scheme (App Installer) to distribute malware. In
Turkish Hackers Exploiting Poorly Secured MS SQL Servers Across the GlobeTurkish Hackers Exploiting Poorly Secured MS SQL Servers Across the Globe
Read Article Poorly secured Microsoft SQL (MS SQL) servers are being targeted in the U.S., European Union, and Latin American (LATAM) regions as part of an ongoing financially motivated campaign to gain initial access. “The analyzed threat campaign appears to end in one of two wa
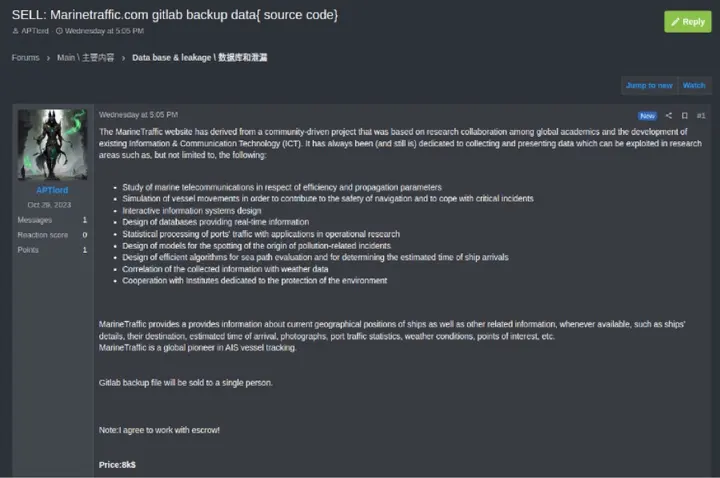
The Underground Economist: Volume 4, Issue 1
https://www.zerofox.com/blog/the-underground-economist-volume-4-issue-1/ On December 27, 2023, threat actor “APTlord” announced on the dark web forum RAMP that they were selling source code and other information owned by marinetraffic[.]com, which was allegedly obtained by the th