


Category Archive
Chinese Cyber Threat Intelligence
54 reports·All intelligence
Chinese APT activity and espionage tooling — group tracking, malware and TTP analysis, and the indicators defenders can act on.
Showing 1–24 of 54 reports
VAPOR PANDA’s ARTEX Campaign: Close the Trust Gaps Behind Parallel Intrusions
CrowdStrike’s VAPOR PANDA research connects parallel ARTEX intrusions with stale signing keys, broad cloud authority and endpoint blind spots. Recover trust, not just the entry point.
BRONZE SANDCASTLE: Hunt the DLL Load Chain, Not the Trusted Executable
Sophos details BRONZE SANDCASTLE DLL sideloading and memory-resident payloads. Practical hunting and response priorities for lean security teams.
Dutch Warning on Chinese Edge-Device Attacks Shows Why Firewall Logs Must Leave the Firewall
A Dutch AIVD/MIVD/NCSC advisory warns that Chinese actors are expected to intensify edge-device exploitation. For SMBs and government contractors, the priority is centralized logging, segmentation, forensic readiness, and faster perimeter patch decisions.
UAT-11985 Shows AI-Assisted Phishing Is Now Real-Time Account Takeover
Cisco Talos reported an APT campaign using AI-assisted event lures, malicious QR codes, and real-time Google AitM phishing. The defensive answer is phishing-resistant MFA, invitation verification, and identity telemetry that connects clicks to sessions.
Antino Backdoor Shows Why Microsoft 365 C2 Needs Cloud-Aware Detection
Cisco Talos reports China-nexus UAT-11587 used the Antino backdoor with Outlook and OneDrive as command-and-control channels. Here is what SMB and government-contractor defenders should monitor.
Warlock Ransomware Shows SharePoint Is Still Critical Infrastructure Risk
Recorded Future News and Symantec report China-nexus Warlock ransomware attacks against water, telecom, government, and university targets. Here is what SMB and government-contractor defenders should do about exposed SharePoint risk.
TA419 Shows AI Policy Is Now an Espionage Phishing Target
Proofpoint reports China-aligned TA419 is targeting U.S. AI policy experts with identity impersonation and adversary-in-the-middle phishing. Here is what SMBs, law firms, universities, and government contractors should take from it.
NeedyMantis Shows Why Post-Compromise Malware Needs Full Intrusion Review
Microsoft’s NeedyMantis analysis shows why targeted malware found after initial access should trigger full intrusion review, not a simple cleanup ticket.
UTA0565 Shows Why Browser Zero-Days Need Endpoint Correlation
Volexity reporting on UTA0565 shows how fake websites, Chrome zero-days, Windows privilege escalation, and CLEANGULP malware turn normal browsing into endpoint compromise. Here are practical controls for SMBs and government contractors.
Fire Ant Shows Why Trusted Infrastructure Needs First-Class Detection
Sygnia’s Fire Ant report shows how routers, TACACS, tunnels, and Linux management hosts can become attacker-controlled infrastructure. The defensive priority is treating the management plane as a monitored, hardened asset class.
PackClient Shows Why Phishing Defense Needs Execution Controls
Proofpoint reported TA4922 using PackClient in tax-themed phishing campaigns. The defensive lesson for SMBs and government contractors is to control the execution chain after the click.
White-Label Router Backdoors Show Why Edge Provenance Matters
ZBT white-label router backdoors are a reminder that SMBs and government contractors need real edge-device provenance, egress monitoring, and procurement controls.
QScan and QTRouter Show Why Proxy Infrastructure Is an Espionage Force Multiplier
The FBI/DOJ disruption of QScan and QTRouter shows how China-linked operators turn reconnaissance and proxy routing into reusable espionage infrastructure.
vCenter Exploitation Shows Patching Alone Is Not Incident Response
Active exploitation of CVE-2026-59310 shows why VMware vCenter patching must be paired with compromise assessment, egress controls, and management-plane segmentation.
vCenter Exploitation Shows Why Control Planes Need Containment
Active exploitation of CVE-2026-59310 shows why vCenter needs more than fast patching: control-plane containment, egress limits, and compromise assessment matter.
HoneyMyte’s CoolClient Rootkit Shows Why Kernel Visibility Matters
HoneyMyte’s CoolClient backdoor now includes signed kernel-mode rootkit capabilities, raising the bar for driver monitoring, Defender exclusion review, and post-compromise endpoint validation.
Pakistani Police Intrusions Show Why Public-Sector Data Systems Are Strategic Targets
SentinelLabs reporting on rival espionage activity against Pakistani law enforcement is a reminder that public-sector portals, case systems, and citizen-data apps are strategic intelligence targets — even when they are not classified systems.
UAT-7810 Shows Edge Devices Are Becoming China-Nexus Relay Infrastructure
Cisco Talos reports UAT-7810 is expanding ORB relay infrastructure using compromised edge and embedded devices. Here is what SMBs and government contractors should do now.
Water Systems Are Becoming Nation-State Pressure Points
Nation-state targeting of water systems shows why exposed OT, weak credentials, remote access, and poor IT/OT segmentation remain practical business risks—not just utility-sector problems.
CL-STA-1062 Shows Critical Infrastructure Intrusions Still Start With Web Shells
Unit 42’s CL-STA-1062 report shows why defenders should focus on exposed web apps, web shells, tunneling tools, scheduled-task persistence, and egress visibility — not just the TinyRCT malware name.
Showboat Malware Shows Telecom Linux Servers Need Rootkit-Level Monitoring
Showboat is a China-linked Linux post-exploitation framework aimed at telecom providers. The lesson for defenders: treat Linux server persistence, dynamic linker abuse, and low-noise C2 as first-class monitoring priorities.
Velvet Ant Shows Authentication Infrastructure Is Critical Infrastructure
Velvet Ant’s Operation Highland shows why PAM, OpenSSH, jump hosts, and proxy paths deserve the same defensive priority as identity providers and domain controllers.
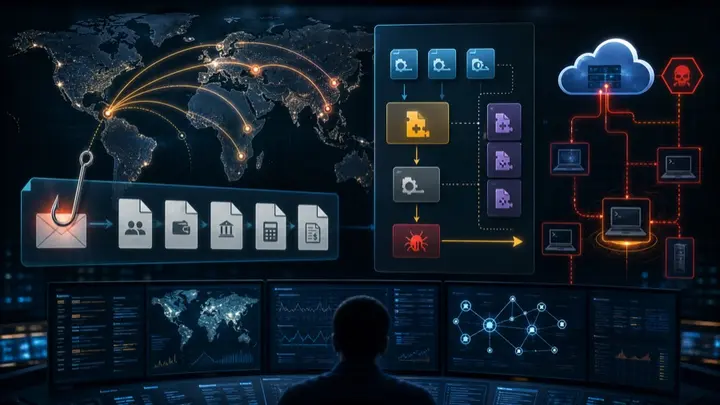
TA4922’s Global Expansion Shows HR and Tax Lures Are Initial Access Infrastructure
Proofpoint’s TA4922 reporting shows how localized HR, payroll, tax, and invoice lures can become full initial-access infrastructure through DLL sideloading, loaders, RATs, RMM tools, and browser credential theft.
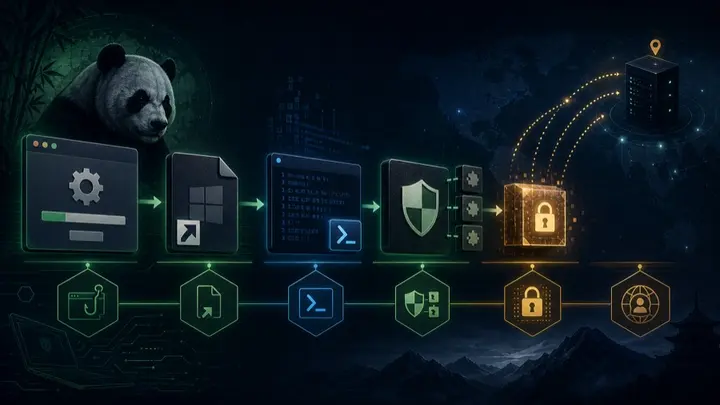
Mustang Panda’s Fake Browser Updater Shows Why LNK Files Still Matter
Mustang Panda’s fake browser updater chain shows why defenders still need to hunt LNK-to-PowerShell execution, DLL sideloading, user-context persistence, and suspicious HTTPS beaconing.