
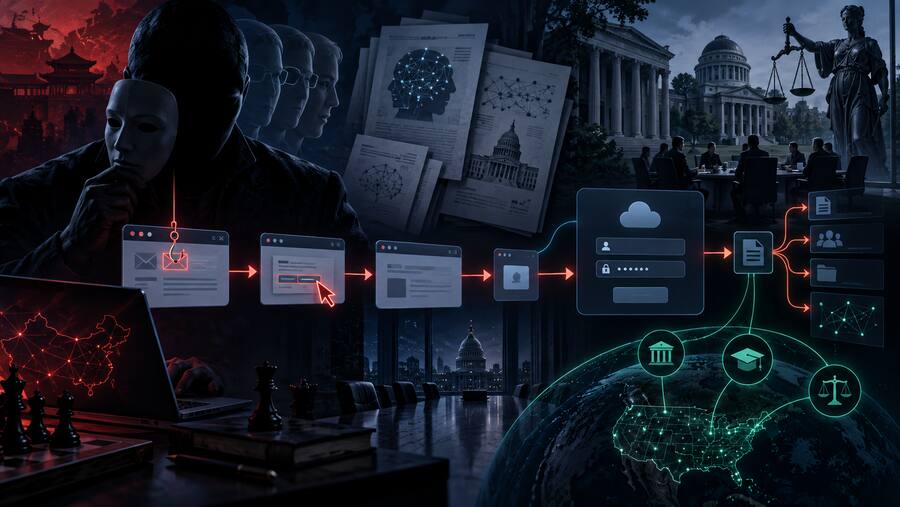





Symantec’s Threat Hunter Team is tracking renewed Warlock ransomware activity from the China-nexus group it calls Longlegs, also known as Storm-2603. The important part for defenders is not the ransomware name. It is the access pattern: exposed on-premises Microsoft SharePoint servers, web shells, machine-key abuse, living-off-the-land administration tools, vulnerable-driver defense evasion, and domain-wide ransomware deployment through SYSVOL.
The latest reporting says victims include a water utility, a telecommunications provider, a regional government body, and a university across Portuguese- and Spanish-speaking countries in Europe, Africa, and Latin America. That mix matters. It shows the same SharePoint exposure problem can jump from “IT incident” to critical-infrastructure disruption very quickly.
What Symantec reported
According to Symantec, Longlegs continues to rely on Microsoft SharePoint exploitation, including the earlier “ToolShell” chain and newer SharePoint-related vulnerabilities highlighted by CISA in 2026. After initial access, the attackers reportedly drop web shells into SharePoint LAYOUTS paths, harvest SharePoint farm ASP.NET machine keys, and use those keys to forge signed payloads that execute inside the SharePoint application pool.
From there, the activity looks like a full domain compromise playbook rather than a simple web-server hit. Symantec described reconnaissance with native Windows utilities, DLL sideloading, payload delivery through legitimate cloud storage services, Visual Studio Code tunnel abuse for covert remote access, NetExec use for Active Directory operations, and a BYOVD-style security-tool killer before Warlock ransomware execution.
The most concerning deployment detail is SYSVOL. In one intrusion, the attackers staged Warlock payloads inside the domain’s SYSVOL share, which is replicated across domain controllers and readable domain-wide. That gives an attacker a built-in distribution path for ransomware once Active Directory control has been achieved.
Why this matters for SMBs and government contractors
SharePoint is often treated as a collaboration service, but in many environments it is also a document repository, identity-integrated application platform, and internet-facing entry point. If it is on-premises and exposed, it deserves the same urgency as VPNs, firewalls, mail gateways, and remote-management appliances.
For small and mid-sized organizations, the risk is especially sharp because SharePoint can sit in a blind spot: patched by one team, backed up by another, monitored lightly, and trusted by identity systems everywhere. For government contractors, the stakes are higher still. SharePoint compromise can expose controlled documents, proposal material, CUI-adjacent workflows, partner data, and authentication paths that support lateral movement into the broader Microsoft estate.
Defensive takeaways
- Treat vulnerable SharePoint as possible compromise, not just patch debt. If an exposed server missed the relevant SharePoint updates, preserve logs and perform web-shell, machine-key, IIS, and application-pool review before closing the ticket.
- Rotate SharePoint farm secrets when compromise is plausible. Machine-key theft changes the game because attackers can forge trusted payloads. Patching alone may not invalidate what was already stolen.
- Watch SYSVOL like a deployment channel. Alert on unusual executables, scripts, ransom-note names, or unexpected directories under SYSVOL paths. SYSVOL should not become a ransomware content-delivery network.
- Baseline admin and developer remote-access tools. Visual Studio Code tunnels, NetExec-style activity, cloud storage downloads, and unexpected MSI execution should be investigated in context, especially from servers.
- Control vulnerable drivers. BYOVD defense evasion keeps showing up across ransomware cases. Enforce vulnerable-driver blocklists, HVCI where feasible, and EDR rules for suspicious driver loading or security-process tampering.
- Separate collaboration recovery from domain recovery. If SharePoint becomes the initial foothold and SYSVOL becomes deployment infrastructure, the recovery plan needs Active Directory validation, credential reset sequencing, and backup integrity checks.
Bulwark Black assessment
Warlock is another reminder that ransomware defense starts before the encryption event. The decisive moments are earlier: exposed SharePoint, stolen machine keys, sideloaded payloads, covert tunnels, domain reconnaissance, and security tooling disabled at scale. By the time ransomware lands from SYSVOL, the attacker has already won multiple smaller battles.
The practical move is to make SharePoint a first-class edge-risk item. Inventory every on-premises SharePoint deployment, confirm patch status, restrict exposure, centralize IIS and Windows event logging, hunt for web shells, and document a recovery path that includes machine-key rotation and Active Directory review. For critical infrastructure and government-adjacent organizations, “collaboration server” is no longer a low-priority asset class.
Original source: Recorded Future News — Warlock ransomware used in attacks on critical infrastructure. The article is based on reporting from Symantec Threat Hunter Team.