


Category Archive
Global Cyber Threat Intelligence
16 reports·All intelligence
Global and cross-region threat intelligence that doesn't sit under a single nation-state — emerging actors, campaigns, and anomalies.
Showing 1–16 of 16 reports
Optimizely Script Compromise: Verify the Cleanup, Recover the Browser Exposure
Optimizely confirms malicious JavaScript in customer projects. Verify clean snippet delivery and investigate earlier payment, session and mobile-device exposure separately.
SSHole Exploitation: Patch the Entry Point, Investigate the Earlier Access
GreyNoise reports successful SSHole exploitation and Previdian records attempts through November 16. Verify affected musl/no-PAM hosts, investigate earlier logins and recover exposed credentials.
BroadWorks Enters CISA KEV: Patch Provisioning, Review the Service Trust
CISA lists BroadWorks CVE-2026-20320 as exploited. Verify the provisioning fix and assess exposed service trust while preserving Cisco's evidence caveat.
N-central Exploitation: Recover the Management Authority, Not Just the Miner
Researchers report miner deployment on N-central servers running HF2. Disable the Legacy API, investigate root-level access and verify the customer-management trust behind the appliance.
Chainalysis Breach: Recover the Tokens, Verify the Screening Backlog
Chainalysis confirms all-user password-hash and live-token exposure. Recover customer access and API keys separately from restoring screening and reconciling missed work.
Stolen App Secrets: Recover the Cloud Access Behind the Credential
Microsoft and Todyl report app-credential intrusions reaching cloud secrets and customer tenants. Contain workload identities and recover the access behind each stolen key.
Cold-Chain Cyberattacks: Protect the Temperature, Not Just the Dashboard
U.S. agencies warn of ongoing refrigeration-controller attacks. Remove public control exposure and verify temperature visibility, safe limits and recovery independently.
NIKKE Launcher Compromise: Recover the Workstation, Not Just the Game
NIKKE launcher tampering shows why a vendor fix is not workstation recovery. Preserve evidence, investigate cached scripts and recover exposed sessions and developer credentials.
APT36 Vibeware Campaign: Pakistan’s Transparent Tribe Weaponizes AI to Mass-Produce Malware Targeting India
Pakistan-aligned threat actor Transparent Tribe (APT36) has embraced AI-assisted malware development to flood Indian government networks with disposable, polyglot implants—a technique security researchers are calling “vibeware” or Distributed Denial of Detection (DDoD). AI-Powere
Pakistan’s APT36 Floods Indian Government Networks With AI-Generated ‘Vibeware’ Malware
A Pakistan-linked threat group is overwhelming Indian government networks with a new breed of disposable, AI-generated malware in a campaign that marks a concerning shift in the digital conflict between the two nations. According to research from Bitdefender, the threat actor APT
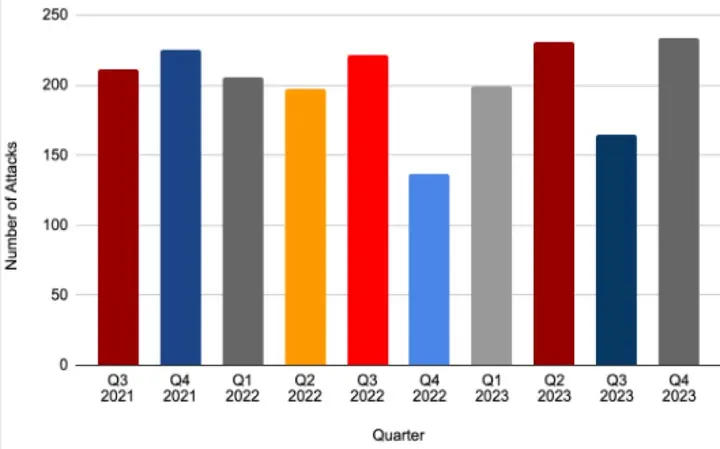
Flash Report: LockBit Ends 2023 with Record Number of Attacks
Read Article Key Findings
Backdoor.Win32 Carbanak (Anunak) / Named Pipe Null DACL
Read Article Discovery / credits: Malvuln (John Page aka hyp3rlinx) (c) 2024 Original source: https://malvuln.com/advisory/b8e1e5b832e5947f41fd6ae6ef6d09a1.txt Contact: malvuln13@gmail.com Media: twitter.com/malvuln Threat: Backdoor.Win32 Carbanak (Anunak) Vulnerability: Named Pi
Financially motivated threat actors misusing App Installer
Read Article Since mid-November 2023, Microsoft Threat Intelligence has observed threat actors, including financially motivated actors like Storm-0569, Storm-1113, Sangria Tempest, and Storm-1674, utilizing the ms-appinstaller URI scheme (App Installer) to distribute malware. In
Opening a Can of Whoop Ads: Detecting and Disrupting a Malvertising Campaign Distributing Backdoors
Read Article Earlier this year, Mandiant’s Managed Defense threat hunting team identified an UNC2975 malicious advertising (“malvertising”) campaign presented to users in sponsored search engine results and social media posts, consistent with activity reported in From DarkGate to
Turkish Hackers Exploiting Poorly Secured MS SQL Servers Across the GlobeTurkish Hackers Exploiting Poorly Secured MS SQL Servers Across the Globe
Read Article Poorly secured Microsoft SQL (MS SQL) servers are being targeted in the U.S., European Union, and Latin American (LATAM) regions as part of an ongoing financially motivated campaign to gain initial access. “The analyzed threat campaign appears to end in one of two wa
100 Days of YARA – 2023
https://bitsofbinary.github.io/yara/2023/01/01/100daysofyara.html