





Cisco Talos published research on UAT-11587, a China-nexus espionage cluster using a previously undocumented Rust-based Windows backdoor called Antino. The campaign matters because the final-stage malware does not rely on a classic suspicious command-and-control server. Talos says Antino uses Microsoft Graph to interact with Outlook and OneDrive, turning trusted Microsoft 365 services into the command, heartbeat, and file-transfer layer.
For defenders, this is the uncomfortable part: blocking bad domains is not enough when the post-compromise channel blends into normal SaaS traffic. SMBs and government contractors increasingly run their identity, email, storage, collaboration, and endpoint telemetry through cloud platforms. If attackers can hide tasking inside those same platforms, security teams need detection that understands identity behavior, application consent, process lineage, and cloud audit logs together.
What Cisco Talos reported
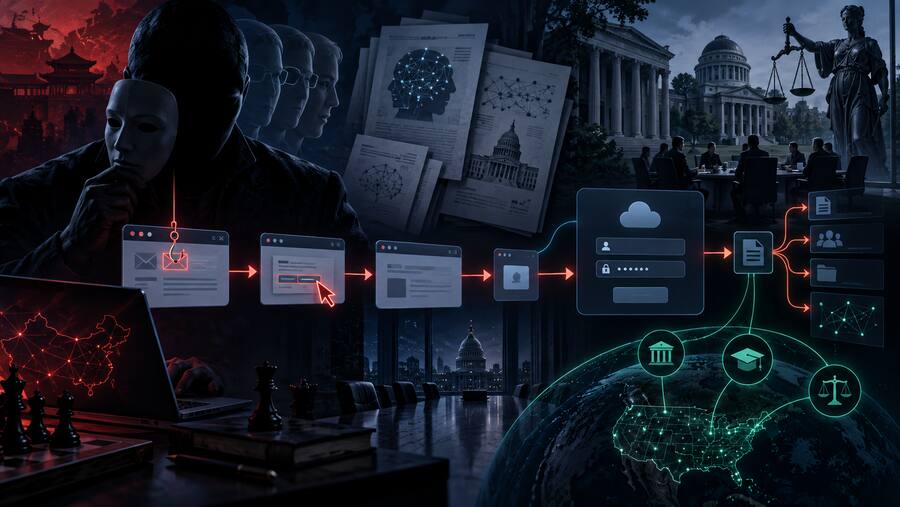
Talos tracks the activity as UAT-11587 and assesses with high confidence that it is China-nexus. The campaign targeted government, policy, academic, civil society, and national-security-adjacent organizations across Asia, including activity affecting or targeting environments in Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, Myanmar, and Syria.
The delivery chain begins with tailored spear-phishing. Talos described lures that cloned Gmail attachment widgets, used policy and regional-security themes, and exploited sender-domain alignment gaps where SPF could pass for the envelope sender while the visible From domain failed DMARC but was still delivered under a non-enforcing policy.
From there, the infection chain uses cloud-hosted HTA and WSF stagers, JavaScript downloaders, encrypted resources, .NET BinaryFormatter deserialization, DLL sideloading through a legitimate Microsoft-signed binary, and finally Antino. Talos says the actor relied heavily on Cloudflare Pages, Cloudflare R2, and Amazon CloudFront for delivery, staging, tracking, and decoy content.
Why Antino stands out
Antino is not just another commodity backdoor. Talos describes it as a Rust-compiled Windows implant with support for host reconnaissance, command execution, PowerShell execution, file listing, file upload and download, in-memory shellcode loading, and persistence through a Registry Run value.
The more important design choice is the C2 model. Antino receives commands through Outlook messages and uses OneDrive for heartbeat and file transfer. The implant polls the operator’s mailbox for command messages, executes tasks on the endpoint, and returns results through the same Microsoft 365-backed workflow.
That architecture creates a detection problem. A firewall may only see encrypted traffic to Microsoft services. A proxy may treat the destination as business-normal. An endpoint alert may show mshta.exe, Windows Script Host, or a signed Microsoft binary in the chain, but without cloud context the full intrusion can look fragmented.
Why this matters for SMBs and government contractors
Government contractors and small public-sector-adjacent organizations are often attractive because they sit near policy, defense, supply-chain, or grant-funded work but do not always have mature cloud detection. They may have Microsoft 365, MFA, EDR, and email security, but still lack the cross-layer visibility needed to connect suspicious endpoint behavior with unusual Graph, Outlook, or OneDrive activity.
This campaign is also a reminder that phishing defense cannot stop at user training. UAT-11587 used tailored content, official-looking documents, current geopolitical themes, cloud-hosted payloads, and sender-spoofing details that can defeat casual inspection. The defensive answer has to include technical controls around script execution, attachment handling, cloud application activity, and identity logging.
Defensive takeaways
- Correlate endpoint and cloud telemetry. Treat Microsoft 365 audit logs, Entra ID sign-in logs, Graph API activity, Defender telemetry, and EDR process trees as one investigation surface.
- Watch script-host process chains. Alert on mshta.exe, wscript.exe, cscript.exe, rundll32.exe, and signed binaries launching from unusual user-writable paths, especially after email or browser activity.
- Hunt for cloud-backed dead drops. Baseline normal Outlook and OneDrive usage. Investigate automated polling, unusual message subjects, repetitive Graph calls, unexpected file movement, and service activity from endpoints that do not normally automate Microsoft 365.
- Do not rely only on domain reputation. Cloudflare, CloudFront, Outlook, and OneDrive are legitimate services. Controls need to evaluate behavior, file type, process parentage, and tenant-level audit context.
- Harden email authentication enforcement. DMARC monitoring mode is useful during rollout, but high-risk domains should move toward quarantine or reject once aligned mail flows are understood.
- Restrict legacy script execution where possible. Reduce exposure to HTA, WSF, and other legacy Windows script paths with attack surface reduction rules, application control, and user-role-based restrictions.
- Review Microsoft Graph permissions and app consent. Investigate unusual delegated or application permissions that could support mailbox, OneDrive, or file access abuse.
- Use the published detections and IOCs as a starting point. Talos published Snort and ClamAV coverage plus indicators. Load them where applicable, but build behavior-based hunts as well.
Bulwark Black assessment
Antino is a good example of where intrusion tradecraft is heading: less obvious infrastructure, more abuse of trusted SaaS workflows, and more pressure on defenders to understand what “normal” looks like inside cloud applications. For smaller teams, the win is not to build a perfect nation-state detection stack overnight. The win is to close the biggest gaps first.
Start with visibility. Make sure Microsoft 365 audit logging is enabled, Entra ID logs are retained, endpoint telemetry captures script-host execution, and alerts can be investigated across identity, email, endpoint, and cloud storage. Then reduce easy execution paths: block unnecessary HTA/WSF usage, control unsigned scripts, monitor DLL sideloading patterns, and require stronger mail authentication handling for domains that represent executives, partners, or government stakeholders.
If your organization handles policy work, defense-adjacent projects, CUI, international programs, or government contracting data, this style of campaign should be treated as relevant even if the current victimology is Asia-focused. The technique is portable, the cloud services are common, and the defensive lesson applies broadly: trusted SaaS traffic still needs threat hunting.
Original source: Cisco Talos — China-nexus UAT-11587 targets government and policy organizations across Asia with Antino backdoor.