


Category Archive
Russian Cyber Threat Intelligence
32 reports·All intelligence
Russian state-sponsored and criminal cyber operations — the actors, malware, and infrastructure we track, and how their targeting shifts.
Showing 1–24 of 32 reports
Cyclops Blink on Cisco FMC Shows Why Edge Appliances Need Compromise Review
Sophos CTU and Cisco Talos reporting on Cyclops Blink activity against Cisco Secure FMC shows why edge security appliances need compromise review, not just emergency patching.
OWAReaper Shows Why Exchange Mailboxes Need Post-Patch Compromise Review
Resecurity’s OWAReaper report shows why on-prem Exchange response cannot stop at patching: defenders need mailbox-permission audits, token revocation, OWA exposure control, and post-patch compromise review.
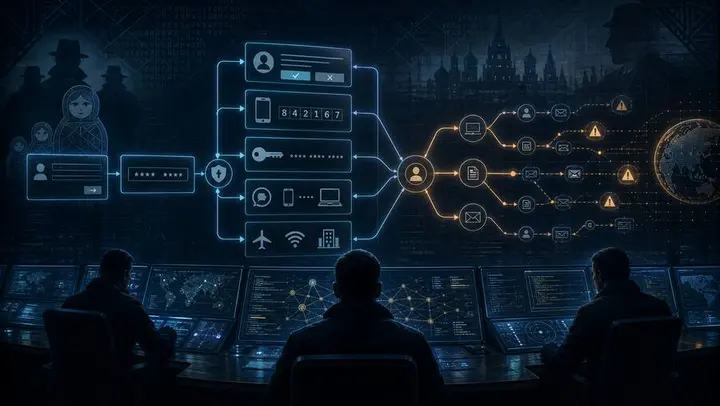
Russian Auth-Flow Phishing Shows MFA Can Be Bypassed Without Exploits
Russian-linked clusters are abusing app passwords, OAuth consent, device-code login, WhatsApp linking, and captive portals. The defense is visibility and governance around authorization flows—not just MFA at login.
CaptiveCrunch Shows Why Travel Wi-Fi Is an Identity Attack Surface
Zscaler reports that Midnight Blizzard operators are abusing hotel and conference Wi-Fi captive portals for Microsoft 365 credential theft, device-code phishing, and malware delivery. Here is what SMBs and government contractors should harden first.
TA488 Turns Outlook Web Access Into a Stealthy Persistence Layer
Proofpoint reports Russia-aligned TA488 abused an Outlook Web Access XSS flaw to deploy OWAReaper, a browser-based implant that can persist beyond passwords and endpoint rebuilds.
Water Systems Are Becoming Nation-State Pressure Points
Nation-state targeting of water systems shows why exposed OT, weak credentials, remote access, and poor IT/OT segmentation remain practical business risks—not just utility-sector problems.
Turla’s STOCKSTAY Backdoor Shows Why Espionage Defense Needs Egress Visibility
GTIG’s STOCKSTAY research shows how Turla blends modular .NET malware, WebSocket C2, and diplomatic targeting. Here are the defensive lessons for SMBs and government contractors.
Kazuar Shows Russian Espionage Malware Is Engineering for Resilience
Microsoft reports that Kazuar, attributed to Russian state actor Secret Blizzard, has evolved into a modular P2P botnet. Here is what SMBs and government contractors should take from it defensively.
Pro-Ukraine Bearlyfy Group Deploys Custom GenieLocker Ransomware Against 70+ Russian Companies
A pro-Ukrainian hacking group called Bearlyfy has been attributed to more than 70 cyber attacks targeting Russian companies since January 2025, with recent operations deploying a proprietary Windows ransomware strain called GenieLocker, according to research from Russian security
DarkSword iOS Exploit Kit: Russian Hackers Weaponize Six Vulnerabilities for Full iPhone Takeover
Google Threat Intelligence Group (GTIG), iVerify, and Lookout have jointly uncovered DarkSword, a sophisticated iOS exploit kit that enables complete device compromise with minimal user interaction. The kit, operational since at least November 2025, has been deployed by suspected
BlackSanta EDR Killer Campaign Targets HR Departments Through Weaponized Resume Files
A year-long malware campaign targets HR departments through weaponized resume files, deploying the previously undocumented BlackSanta EDR killer that disables endpoint security tools at the kernel level.
Russian APT Deploys Cat-Themed BadPaw and MeowMeow Malware to Target Ukraine
Security researchers from ClearSky have uncovered a sophisticated Russian cyber campaign targeting Ukrainian organizations using two previously unknown malware strains with distinctly playful names: BadPaw and MeowMeow. Despite their whimsical naming, these tools represent a seri
APT28 Exploited CVE-2026-21513 MSHTML Zero-Day as Attack Vector Before February Patch Tuesday
Russia’s state-sponsored threat actor APT28 (also known as Fancy Bear) has been linked to active exploitation of CVE-2026-21513, a high-severity MSHTML zero-day vulnerability, before Microsoft released its patch in February 2026. This finding comes from new research published by
Russian Cyberattacks Shift to Intelligence Gathering for Missile Strike Guidance on Ukraine Power Grid
Russian cyberattacks targeting Ukraine’s energy infrastructure have shifted focus from immediate disruption to intelligence gathering for guiding missile strikes, Ukrainian cybersecurity officials revealed at the Kyiv International Cyber Resilience Forum. Strategic Shift in Attac
Diesel Vortex: Russian Cybercrime Group Steals 1,600+ Credentials From Global Logistics Sector
A Russian-linked cybercrime group dubbed Diesel Vortex has been systematically targeting the global freight and logistics industry, stealing over 1,600 unique login credentials from users of major logistics platforms in a sophisticated phishing campaign that ran from September 20
APT28 Deploys Operation MacroMaze: Webhook-Based Macro Malware Targets European Entities
Russia-linked APT28 (also known as Fancy Bear, Pawn Storm, Sofacy Group, Sednit, BlueDelta, and STRONTIUM) has launched a sophisticated espionage campaign targeting entities across Western and Central Europe. The operation, codenamed Operation MacroMaze by S2 Grupo’s LAB52 threat
AI-Augmented Attack: Russian-Speaking Cybercriminals Compromise 600+ FortiGate Firewalls
A Russian-speaking cybercrime group has compromised more than 600 internet-exposed FortiGate firewalls across 55 countries in just over a month, leveraging off-the-shelf generative AI tools to automate and scale their operations, according to a new incident report from AWS. Attac
APT28 Targets European Entities with Operation MacroMaze Webhook Malware Campaign
Russia’s notorious state-sponsored threat actor APT28 (also known as Fancy Bear) has been attributed to a sophisticated new campaign targeting organizations across Western and Central Europe. According to S2 Grupo’s LAB52 threat intelligence team, the campaign—codenamed Operation
Russian Threat Actor Deploys CANFAIL Malware Against Ukrainian Organizations
Google Threat Intelligence Group (GTIG) has uncovered a new threat actor possibly affiliated with Russian intelligence services that has been systematically targeting Ukrainian organizations with a sophisticated malware strain known as CANFAIL. Target Profile The threat group has
APT28 Exploits CVE-2026-21509 in Operation Neusploit: Stealing Emails with MiniDoor Backdoor
Russia’s infamous APT28 (Fancy Bear/Forest Blizzard) threat group has weaponized a recently patched Microsoft Office vulnerability in just three days, launching a sophisticated espionage campaign dubbed Operation Neusploit targeting government and diplomatic entities across Centr
Russian Legion Hacker Alliance Launches OpDenmark Campaign Against Danish Critical Infrastructure
A newly formed Russian hacktivist alliance called Russian Legion has launched OpDenmark, a coordinated cyberattack campaign against Danish critical infrastructure in retaliation for the country’s 1.5 billion DKK military aid package to Ukraine.
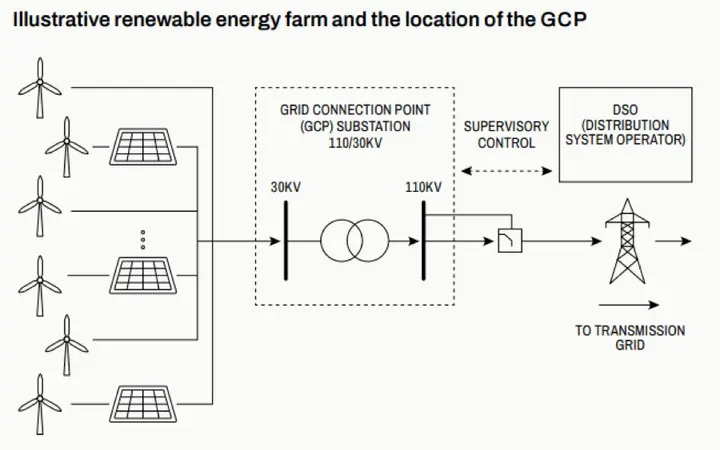
Russian Hackers Launch Coordinated Cyberattacks on Poland’s Renewable Energy Infrastructure
Russian state-sponsored threat actors launched coordinated cyberattacks against Poland’s energy sector on December 29, 2025, targeting over 30 wind and solar farms, a manufacturing company, and a major combined heat and power (CHP) plant that serves nearly 500,000 people, accordi
Poland Thwarts Russian Sandworm Wiper Attack on Power Plants
Russian APT group Sandworm attempted to deploy destructive DynoWiper malware against Polish power plants in late December 2025. The attack was thwarted, but highlights ongoing threats to critical infrastructure from state-sponsored actors.
Poland Thwarts Russian Wiper Malware Attack on Power Plants
Source: Hackread | Author: Deeba Ahmed Poland has narrowly avoided a massive energy crisis following what officials are calling the largest cyberattack on the country in years. Between 29 and 30 December 2025, hackers attempted to break into the nation’s energy infrastructure, sp