


Category Archive
Malware
180 reports·All intelligence
Malware family breakdowns and reversing notes, mapped to the behavior defenders can actually detect and block.
Showing 1–24 of 180 reports
Optimizely Script Compromise: Verify the Cleanup, Recover the Browser Exposure
Optimizely confirms malicious JavaScript in customer projects. Verify clean snippet delivery and investigate earlier payment, session and mobile-device exposure separately.
N-central Exploitation: Recover the Management Authority, Not Just the Miner
Researchers report miner deployment on N-central servers running HF2. Disable the Legacy API, investigate root-level access and verify the customer-management trust behind the appliance.
CWPdoor: Check the Management Server, Not Just Its Access Logs
XLab's CWPdoor analysis exposes a passive backdoor inside CWP's management web server. Check binary integrity, preserve evidence and recover the host's authority.
3AM Ransomware: Keep Backup Authority Outside the Domain Blast Radius
Bitdefender's 3AM investigation links backup credential theft, rogue admins and domain trusts to ransomware spread. Separate recovery authority and test the real blast radius.
NIKKE Launcher Compromise: Recover the Workstation, Not Just the Game
NIKKE launcher tampering shows why a vendor fix is not workstation recovery. Preserve evidence, investigate cached scripts and recover exposed sessions and developer credentials.
APT29-Linked Mobile Watering Holes: Patch the Phone, Recover the Sessions
Sekoia links mobile watering holes to APT29 with moderate-to-high confidence. Verify phone updates and recover exposed sessions separately from device cleanup.
VAPOR PANDA’s ARTEX Campaign: Close the Trust Gaps Behind Parallel Intrusions
CrowdStrike’s VAPOR PANDA research connects parallel ARTEX intrusions with stale signing keys, broad cloud authority and endpoint blind spots. Recover trust, not just the entry point.
BRONZE SANDCASTLE: Hunt the DLL Load Chain, Not the Trusted Executable
Sophos details BRONZE SANDCASTLE DLL sideloading and memory-resident payloads. Practical hunting and response priorities for lean security teams.
Siemens Software Center ClickFix Attacks: Hunt Beyond the Trusted Signature
Siemens confirms active DLL-sideloading attacks. Update Software Center, investigate unexpected signed copies, and correlate process paths, persistence and network evidence.
PEERSTITCH: Recover the Management Trust, Not Just the Firewall
PEERSTITCH research highlights the recovery gap after firewall-management compromise: patch the entry point, investigate managed devices, and replace exposed trust material.
CikaBika Bot: Detect the Document-to-Discord Attack Chain
CikaBika Bot turns a document lure into Discord-based remote control. Practical detection priorities for lean security teams, from shortcut execution to outbound service access.
AOMEI Update Tampering Shows Why Clean URLs Cannot Close Endpoint Alerts
Google researchers documented brief AOMEI update-server tampering windows. A practical response guide for SMBs and government contractors: preserve event-time evidence and distinguish vendor remediation from endpoint recovery.
AhsayCBS Webshell Attacks Show Backup Servers Are High-Value Entry Points
Active exploitation of AhsayCBS backup-management flaws shows why backup consoles need restricted access, compromise hunting, credential rotation, and recovery validation.
Trojanized Terraform Providers Show IaC Pipelines Are Developer Endpoints
Zscaler ThreatLabz detailed a suspected TraderTraitor campaign using a fake Terraform provider to launch cross-platform malware. The practical lesson: infrastructure-as-code plugins run on developer and CI/CD systems, so they need endpoint controls, provenance checks, and egress monitoring.
Ransomware Negotiation Arrest Shows Why Extortion Response Needs Guardrails
A ShinyHunters-linked arrest report is a reminder that ransomware negotiation is not just a tactical service. SMBs and government contractors need clear authority, evidence handling, vendor vetting, and legal guardrails before extortion starts.
Midnight Mimosa Shows Why Cheap Android Devices Need Supply-Chain Controls
Bitdefender found firmware-level Android malware preinstalled on low-cost devices. For SMBs and government contractors, the lesson is procurement discipline, segmentation, mobile access policy, and monitoring for proxy-like behavior.
AI-Analysis Evasion Shows Why Malware Triage Needs Prompt Boundaries
Cisco Talos found malware families embedding natural-language instructions meant to steer AI-assisted analysis. The lesson for defenders: treat sample text as evidence, not instruction.
ClingSTUN Shows Why IoT Edge Devices Need Real Egress Monitoring
Fortinet’s ClingSTUN research shows how compromised IoT and edge devices can abuse public STUN infrastructure to become proxy backdoors. SMBs and government contractors should treat exposed firmware, unexpected UDP/STUN traffic, and unmanaged edge devices as a real incident-response priority.
Ransomware Data Theft Surge Shows Why Exfiltration Defense Comes First
Zscaler ThreatLabz reports ransomware data theft surged 275.8% year over year, with government, healthcare, education, and utilities facing larger exfiltration events. Defenders need controls that stop data movement before encryption begins.
Antino Backdoor Shows Why Microsoft 365 C2 Needs Cloud-Aware Detection
Cisco Talos reports China-nexus UAT-11587 used the Antino backdoor with Outlook and OneDrive as command-and-control channels. Here is what SMB and government-contractor defenders should monitor.
Warlock Ransomware Shows SharePoint Is Still Critical Infrastructure Risk
Recorded Future News and Symantec report China-nexus Warlock ransomware attacks against water, telecom, government, and university targets. Here is what SMB and government-contractor defenders should do about exposed SharePoint risk.
DragonForce TURN and MQTT Backdoors Show Why Ransomware Defense Needs Egress Visibility
Lab52 reports DragonForce-linked backdoors abusing TURN relays and MQTT for resilient command-and-control. Here is what SMBs and government contractors should monitor now.
2CLoader Shows Why Malware Loader Alerts Need Identity Response
Zscaler ThreatLabz detailed 2CLoader delivering Vidar, Remus, and XWorm. Here is why SMB and government-contractor defenders should treat loader detections as credential and identity incidents.
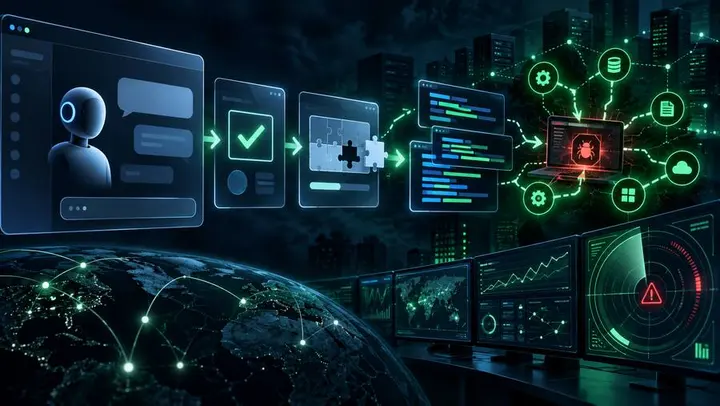
Custom GPT ClickFix Shows Why AI Trust Needs Browser-to-Shell Controls
Attackers abused ChatGPT Custom GPT pages and fake verification prompts to push victims into a ClickFix-to-RAT chain. Here is what SMB and government-contractor defenders should monitor.