
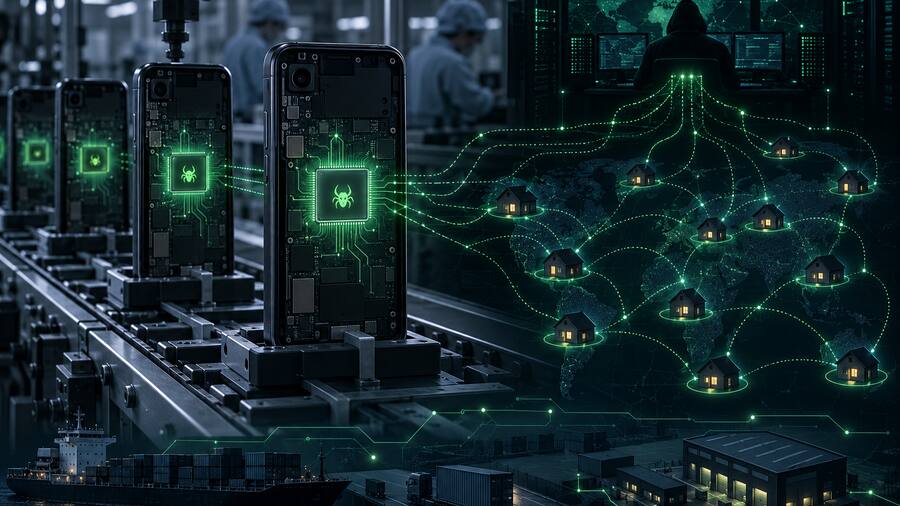







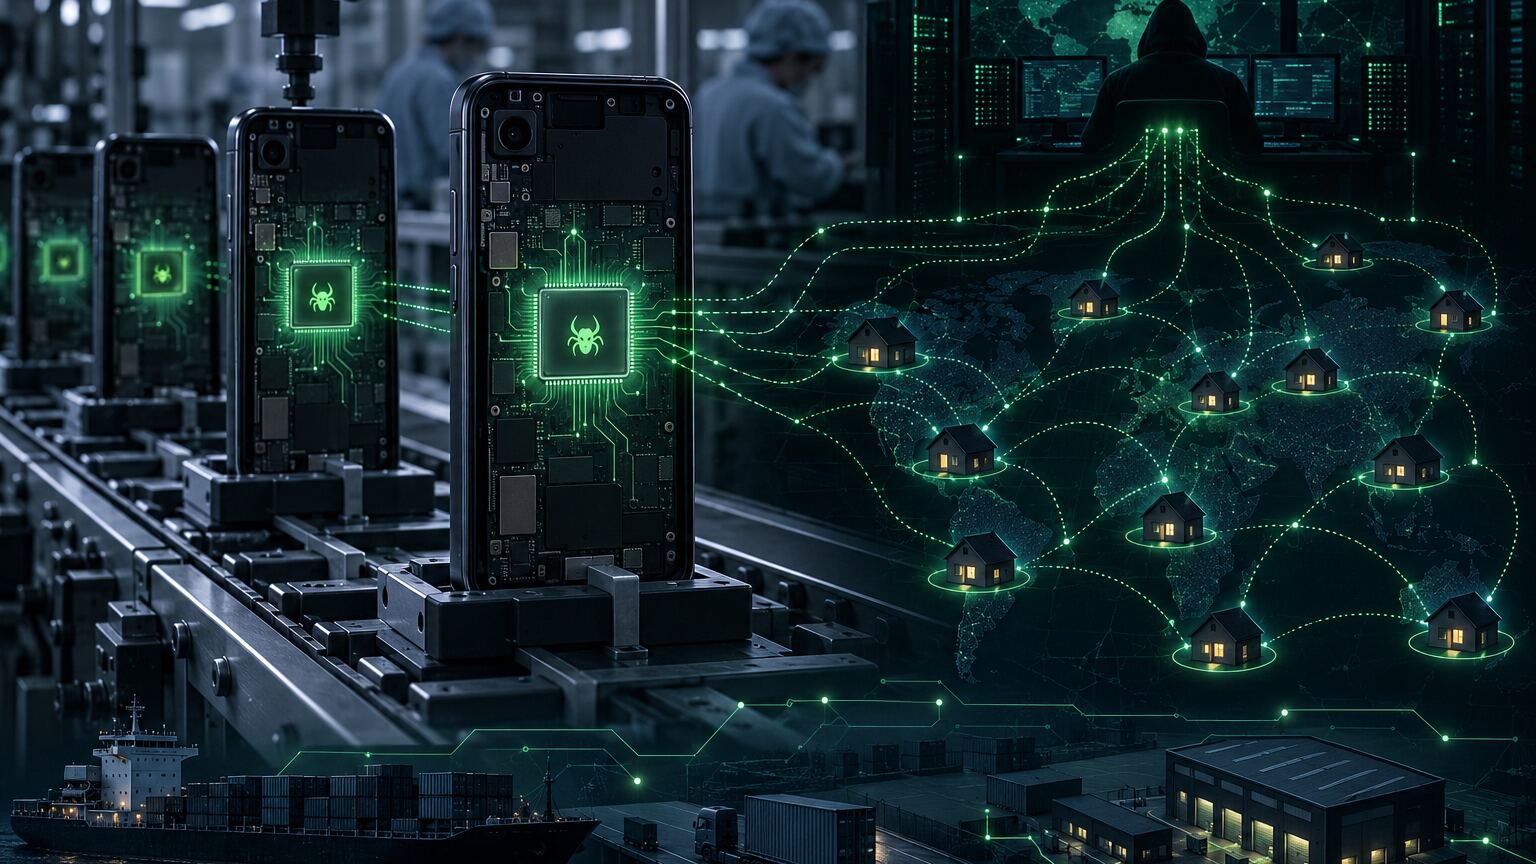
Bitdefender published research on a malware campaign it calls Midnight Mimosa, and the uncomfortable part is not just what the malware does. It is where it starts: inside the firmware of low-cost Android devices before the customer ever turns the phone on.
That changes the defensive model. This is not a normal mobile malware story where the fix is simply “do not install sketchy apps.” In this case, the device can arrive with a privileged system component already present, already trusted by the operating system, and already capable of silently installing additional payloads.
For small businesses, managed service providers, and government contractors, the lesson is direct: cheap unmanaged devices are not harmless endpoints. They can become proxy infrastructure, ad-fraud nodes, data collection points, and footholds on networks that were never designed to trust them.
What Bitdefender reported
According to Bitdefender, Midnight Mimosa affects low-cost, multi-brand Android devices built on MediaTek platforms. The core malware is installed as a persistent system application with elevated privileges. Researchers observed system-sounding package names such as com.android.system.lite, com.android.sys.prot, com.android.sys.gmsprot, and com.android.sys.bcprot.
Because the malicious component is platform-signed and lives in the system partition, a normal user cannot remove it like a typical app. That matters because the malware can silently deploy other applications, grant sensitive permissions, remove payloads, and load remotely supplied code.
Bitdefender says the campaign has been used for multiple monetization paths, including hidden ad fraud, automated click fraud, device profiling, and residential proxy functionality. In practice, that means an infected phone can be turned into a relay point for someone else’s traffic. From the outside, activity may appear to come from the victim’s normal internet connection rather than the operator’s infrastructure.
The research also found related apps in Google Play that communicated with the same infrastructure. Those apps did not have the same system-level privileges as the firmware components, but they show how the same operation can blend preinstalled compromise with ordinary app-store distribution.
Why this matters for SMBs and contractors
The obvious consumer warning is “do not buy suspiciously cheap phones.” That is true, but it is not enough for business security.
Many organizations have device exposure that is informal and poorly inventoried: temporary phones, employee-owned Android devices, shared shop-floor tablets, field devices, visitor devices, test hardware, contractor phones, and cheap devices purchased quickly to solve an operational problem. Those devices often sit outside formal endpoint management, but they still touch Wi-Fi, email, MFA prompts, cloud portals, messaging apps, or internal web tools.
For companies working around government contracts, the risk is bigger than nuisance malware. A compromised mobile device can create:
- Network reputation risk: residential proxy abuse can make malicious traffic appear to originate from the organization’s connection.
- Access risk: unmanaged phones may receive MFA prompts, email links, calendar invites, or files tied to business workflows.
- Segmentation risk: guest Wi-Fi that can still reach printers, admin panels, cameras, or internal services is not really guest Wi-Fi.
- Procurement risk: unknown firmware provenance becomes part of the attack surface, especially for bargain devices and marketplace hardware.
- Incident-response risk: a device compromised at the firmware level may not be cleanable through normal app removal or factory reset assumptions.
Defensive takeaways
1. Treat procurement as a security control. Avoid bargain Android devices from unclear supply chains for business use. Standardize on supported models from reputable vendors with predictable update channels. If a device is important enough to access business systems, it is important enough to buy from a trusted source.
2. Separate guest, BYOD, and managed assets. Guest and personal-device networks should not have lateral access to internal systems. That includes printers, NAS devices, cameras, router admin pages, hypervisors, and management interfaces. If segmentation is not enforced, one bad phone can become a useful pivot point.
3. Put mobile access behind policy. Email, VPN, cloud apps, and admin consoles should require compliant devices where possible. At minimum, restrict sensitive access from unmanaged mobile devices and require phishing-resistant MFA for privileged accounts.
4. Monitor for proxy-like behavior. Residential proxy malware may show up as unusual outbound connections, long-lived sessions to unfamiliar infrastructure, repeated connections from guest networks, or unexpected bandwidth patterns from mobile subnets. Small teams do not need perfect mobile EDR to notice that a guest Wi-Fi client is behaving like infrastructure.
5. Do not assume a factory reset solves firmware compromise. If malware is in the system image, wiping user data may not remove the root cause. Firmware reflash, vendor remediation, device retirement, or ADB-based disabling may be required. For business environments, replacement is often cheaper than investigation time.
Bulwark Black assessment
Midnight Mimosa is a reminder that endpoint trust starts before login. If the hardware and firmware supply chain are weak, the operating system can be compromised before the user makes a single bad decision.
For defenders, the practical answer is not panic. It is boundaries. Keep unmanaged devices away from sensitive networks, tighten mobile access to cloud services, standardize procurement, and watch for devices acting like relays. Cheap devices are only cheap if they do not become part of your incident report.