




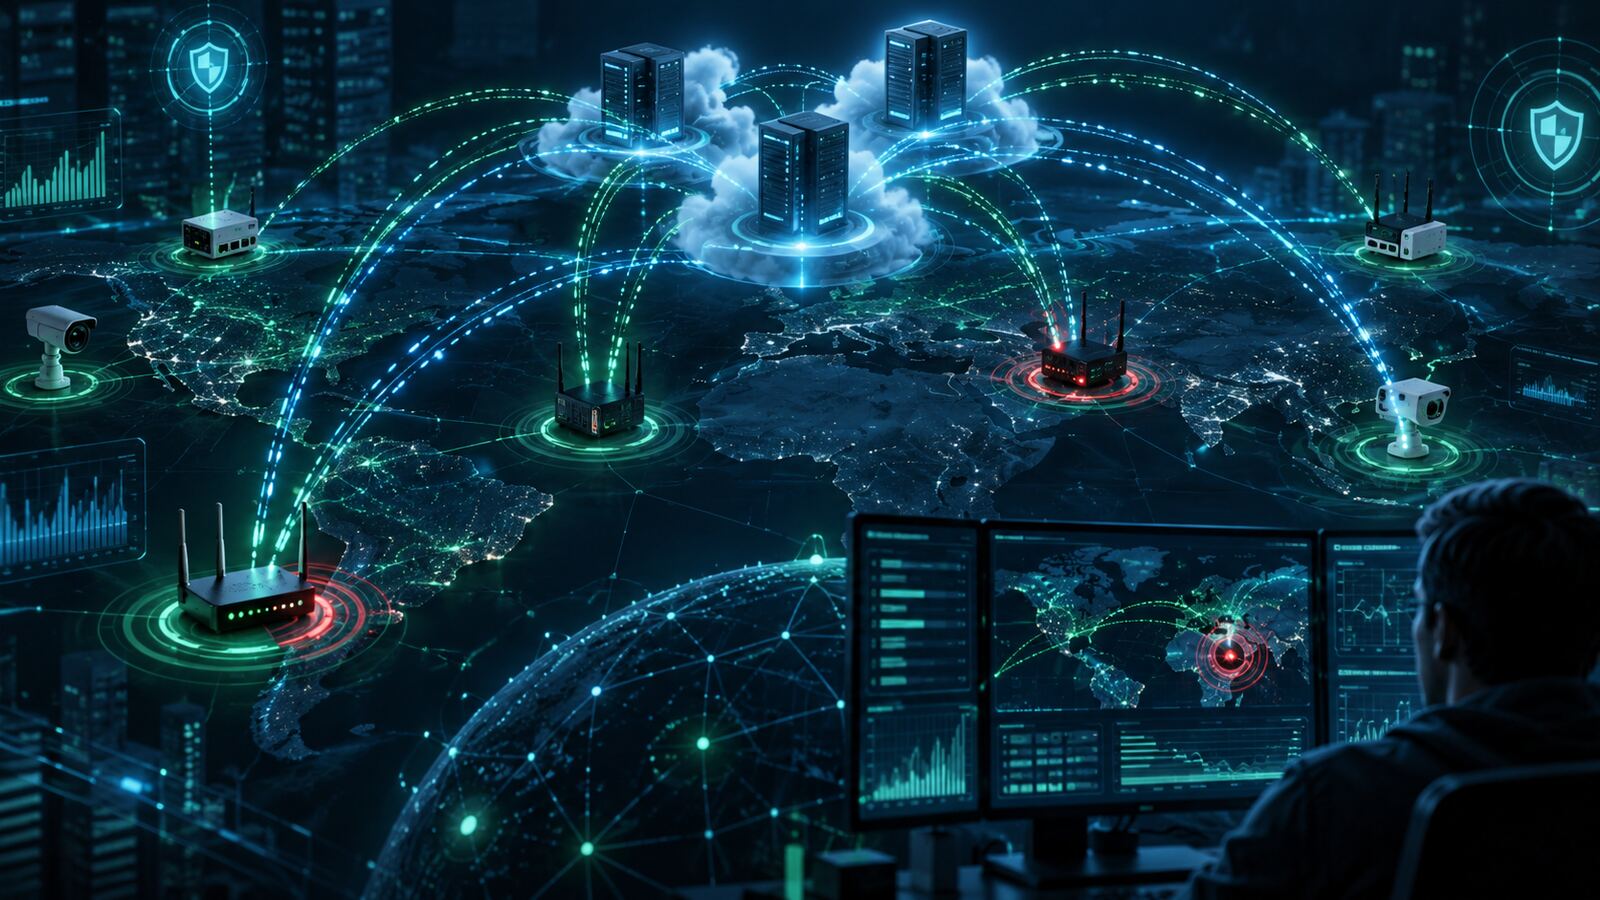
FortiGuard Labs has published research on ClingSTUN, a Linux back-connect proxy backdoor that compromises exposed routers, DVRs, gateways, and other Internet-facing devices by exploiting known vulnerabilities. The important part for defenders is not just that another IoT botnet exists. It is how the malware keeps access useful after compromise: it abuses legitimate public STUN infrastructure to learn external IP and port mappings, maintain NAT reachability, and make infected devices usable as proxy nodes.
That matters for small businesses and government contractors because these devices often sit at the messy edge of the network: branch routers, cameras, old VPN gear, vendor-managed appliances, and embedded systems that rarely receive the same asset-management attention as laptops and servers. Once compromised, they can become durable relay points for intrusion activity, credential attacks, scanning, or traffic laundering while blending into traffic patterns that may look like normal VoIP or WebRTC behavior.
What Fortinet reported
Fortinet describes ClingSTUN as a Linux malware family that targets unpatched Internet-facing devices and turns them into remotely controlled proxy infrastructure. The campaign has shifted download sources over time and uses multiple known vulnerabilities across vendors, including flaws affecting Hytec Inter routers, EnGenius IoT cloud service components, D-Link UPnP, Realtek SDK devices, TP-Link Archer AX21, AVTECH cameras, Ivanti Connect Secure / Policy Secure, Tenda devices, and other embedded platforms.
After execution, the malware attempts to improve persistence and survival. Fortinet observed behavior including watchdog manipulation, process killing, persistence through startup files, command-line concealment, and remote command execution. The STUN behavior is the differentiator: ClingSTUN sends STUN binding requests to public endpoints to discover its external mappings and preserve connectivity through NAT. Fortinet notes that those public STUN services should not automatically be treated as attacker-controlled infrastructure; defenders need to evaluate that traffic alongside host behavior and other suspicious network signals.
Why this matters for SMBs and government contractors
Edge and IoT compromise is easy to underestimate because the affected devices may not hold sensitive files themselves. The risk is that they provide position. A compromised router, camera, DVR, or gateway can give an attacker a foothold that is hard to inventory, hard to monitor, and useful as a proxy for additional operations.
For organizations that handle government work, this also creates documentation and due-care problems. If an old device is exposed to the Internet, no longer supported by the vendor, and missing from the asset inventory, it becomes difficult to prove that patching, vulnerability management, incident response, and boundary protection are being handled consistently. Even when the compromised device is not a CUI repository, it can still weaken the environment that protects business systems, remote access, and contractor operations.
Defensive takeaways
- Inventory the forgotten edge. Include routers, cameras, DVRs, wireless bridges, IoT gateways, branch devices, lab gear, and vendor-managed appliances. If it has an IP address and talks externally, it belongs in scope.
- Find unsupported firmware. Patchable devices should be updated. End-of-life devices should be replaced, isolated, or blocked from direct Internet exposure.
- Reduce public exposure. Disable unnecessary WAN-facing administration, UPnP, legacy web interfaces, and unused services. Put management behind VPN or trusted administrative networks.
- Watch for suspicious UDP and STUN patterns. STUN is not malicious by itself, but unexpected STUN traffic from routers, cameras, DVRs, or appliances deserves review—especially when paired with odd processes, repeated keepalives, or connections to unusual public endpoints.
- Monitor for abnormal outbound proxy behavior. Look for edge devices initiating traffic that does not match their role: broad outbound connections, unusual ports, scanning behavior, or traffic volumes inconsistent with normal operation.
- Preserve evidence before wiping devices. If compromise is suspected, collect logs, configuration backups, firmware versions, network flows, and packet captures where possible. Reimaging without evidence may remove the only visibility into how the device was used.
Bulwark Black assessment
ClingSTUN is a reminder that attackers do not need a domain controller on day one. A reliable proxy node on the edge can be enough to support reconnaissance, intrusion routing, credential abuse, or follow-on exploitation. The practical defense is not exotic: asset inventory, firmware lifecycle management, exposure reduction, and egress monitoring. The hard part is applying those basics to the devices that sit outside normal endpoint tooling.
For SMBs and government contractors, the priority should be a focused edge-device sprint: identify every Internet-facing appliance, confirm vendor support and firmware level, remove unnecessary exposure, and baseline outbound traffic. If a device cannot be patched or monitored, assume it is a liability and isolate it accordingly.
Source: Fortinet FortiGuard Labs — “ClingSTUN Linux Backdoor Abuses Public STUN Infrastructure”.