



Cisco’s latest Catalyst SD-WAN Manager advisory is a reminder that the management plane is now one of the highest-value targets in enterprise and government-contractor networks. CVE-2026-76504 is not just another edge-device CVE: it is an actively exploited authentication bypass that can give an unauthenticated remote attacker administrator-level access to the SD-WAN Manager API.
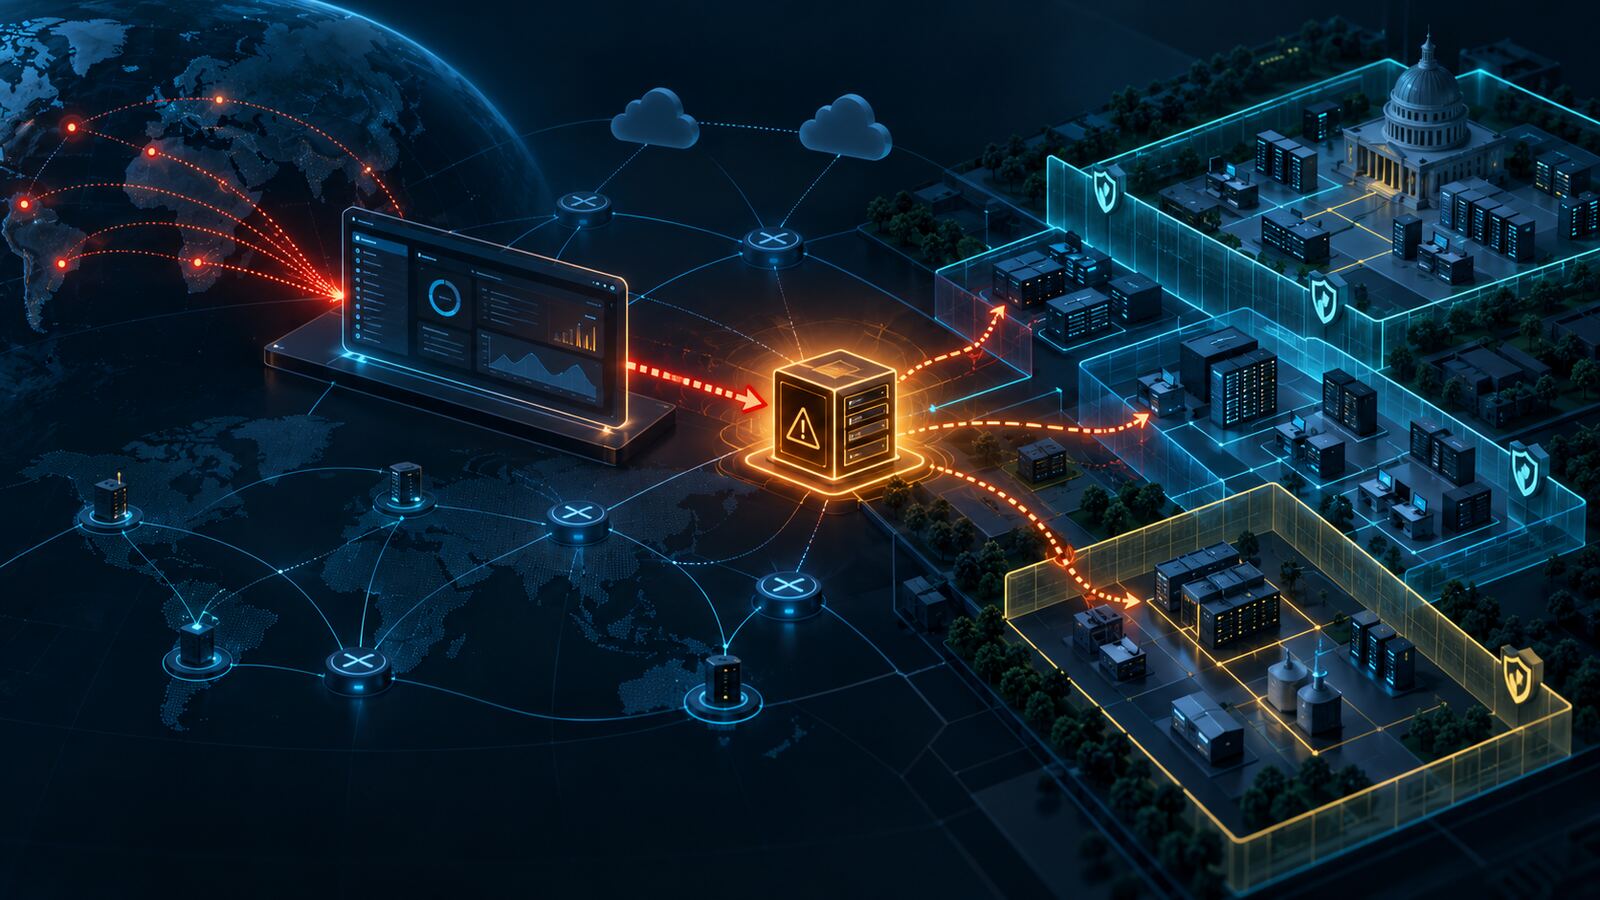
For organizations that use SD-WAN to connect offices, cloud environments, remote users, and partner sites, that API sits dangerously close to the routing and policy heart of the business. If the manager is exposed or reachable from untrusted networks, this needs emergency handling: patch, reduce exposure, preserve logs, and review for compromise.
What Cisco disclosed
Cisco says the vulnerability exists in API session-based authentication management for Catalyst SD-WAN Manager, formerly known as vManage. The issue is tied to improper handling of URI encoding in HTTP requests. In practical terms, a crafted request can bypass an authentication rule meant to restrict access to a protected API endpoint.
A successful exploit allows the attacker to reach the API as the admin user. Cisco rated the flaw critical with a CVSS score of 9.8, confirmed active exploitation, released fixed software, and stated that there are no full workarounds. Cisco also noted that its Live Protect shield can provide temporary partial coverage for upgrade planning, but upgrade to a fixed release is the actual remediation path.
The fixed-release guidance includes Cisco Catalyst SD-WAN Manager 20.9.10.1, 20.12.8.2, 20.15.6.1, 20.18.4.1, 26.1.2.1, and 26.2.1, with earlier-than-20.9 deployments needing migration to a fixed release path. Cloud-managed Cisco SD-WAN customers should still verify their service status and vendor guidance, but on-premises and exposed management-plane deployments deserve immediate attention.
Why this matters beyond Cisco shops
The deeper lesson is not vendor-specific. Edge and network-control platforms concentrate trust. SD-WAN managers, VPN concentrators, firewalls, email gateways, identity appliances, and remote-access platforms often sit at the boundary between the internet and everything the business needs to protect. When attackers gain administrative access to those systems, they may not need noisy malware to create serious risk.
For SMBs and government contractors, SD-WAN compromise can create several business-impact scenarios:
- Configuration exposure. Attackers may learn network topology, site relationships, routing paths, VPN details, and security policy structure.
- Policy manipulation. Admin-level API access can potentially change how traffic moves, what is reachable, and which controls are enforced.
- Credential and secret risk. Management platforms often contain integrations, certificates, tokens, or configuration data that may support follow-on access.
- Persistence through infrastructure. Attackers with control-plane access may be able to create users, modify settings, or prepare later access paths.
- Contract and compliance exposure. If the network supports regulated workloads, customer systems, or CUI-adjacent data flows, compromise review becomes more than an IT cleanup task.
Immediate defensive actions
Treat this as an emergency change window, not a routine monthly patch item.
- Identify every Catalyst SD-WAN Manager instance. Include production, lab, disaster-recovery, cloud-hosted, and abandoned migration systems.
- Patch to a fixed release. Follow Cisco’s compatibility guidance and do not rely on configuration changes as a substitute for upgrade.
- Remove internet exposure where possible. Management interfaces should be reachable only from trusted administrative networks, VPN paths, or hardened jump infrastructure.
- Restrict access if temporary exposure remains. Use filtering controls to allow only known administrative source addresses while the upgrade is being completed.
- Preserve relevant logs before rebuilding or wiping. Evidence may be needed for incident response, customer reporting, insurance, or contractual review.
- Open a vendor support case if compromise is suspected. Cisco recommends TAC review for potentially compromised systems and references admin-tech collection for support analysis.
What to hunt for
Cisco’s advisory points defenders toward requests involving the j_security_check path with URI-encoded characters, including the example %6a encoding for the letter “j.” BleepingComputer and Rapid7 both highlighted Cisco’s recommended log review locations, including /var/log/nms/containers/service-proxy/serviceproxy-access.log and /var/log/nms/vmanage-server.log.
Do not stop at one string match. Cisco cautions that the provided encoded character is an example, and that some indicators may also appear during normal operations. A useful review should combine path anomalies, source IP reputation, administrative activity, configuration changes, account creation, API actions, and timeline correlation with patch status.
Priority questions for responders:
- Was the SD-WAN Manager reachable from the internet or from a broad internal network segment?
- Do logs show encoded-character requests to authentication or API paths from unknown sources?
- Were new users, tokens, certificates, templates, devices, policies, or integrations created or modified?
- Did administrative activity occur from unusual IP addresses, geographies, user agents, or times?
- Were configuration exports, backups, admin-tech bundles, or sensitive files downloaded?
- Are there downstream indicators on managed routers, branch sites, VPN paths, or logging systems?
How to reduce repeat risk
This is the kind of vulnerability that should trigger a management-plane architecture review. The goal is not just to survive CVE-2026-76504; it is to make the next edge-control flaw less catastrophic.
- Inventory all internet-facing management planes. Include network, identity, security, backup, hypervisor, and SaaS administration interfaces.
- Put management behind a separate trust boundary. Administrative access should require strong identity, device posture, network allowlisting, and logging.
- Monitor API administration separately from user activity. API calls often show compromise faster than dashboard logins.
- Log before you need it. Send appliance and controller logs to a place attackers cannot easily modify from the compromised appliance itself.
- Practice edge-device incident response. Know how to preserve evidence, rotate secrets, validate configuration integrity, and rebuild trust in managed devices.
Bulwark Black assessment
CVE-2026-76504 belongs in the same mental category as exploited VPN, firewall, and email-gateway flaws: a single exposed management surface can become an attacker’s shortcut around the rest of the security stack. For smaller organizations, the danger is that these systems are often treated as “set and forget” infrastructure even though they control the paths attackers want most.
The practical move is simple but urgent: patch the manager, restrict who can reach it, and review for signs that exploitation already happened. If your organization supports government customers, regulated data, or distributed operations, document the remediation and evidence review. That record matters when the question becomes not only “did we patch?” but “did we verify trust in the control plane?”
Original source: Cisco — Catalyst SD-WAN Manager API Authentication Bypass Vulnerability.
Additional context: CIS MS-ISAC advisory, Rapid7 emergent threat response, and BleepingComputer coverage.