
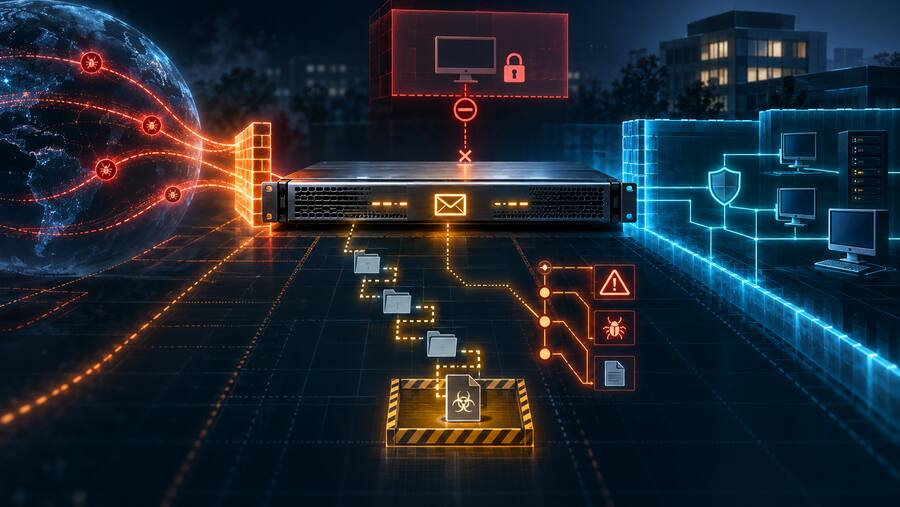





Fortinet has warned that CVE-2026-104286, a critical FortiMail vulnerability, is being exploited in the wild. The issue affects the FortiMail management interface and can allow an unauthenticated attacker to write arbitrary files through crafted HTTP or HTTPS requests. CISA added the flaw to the Known Exploited Vulnerabilities catalog on October 1, 2026, which should move it from “patch queue” to “incident-response queue” for any organization with exposed FortiMail management access.
The most important defensive point is simple: when an internet-facing security appliance is exploited before broad patch availability, the job is not only to apply a workaround. Teams need to assume the device may have been used as a foothold, preserve logs, hunt for the vendor-published indicators, and verify whether mail archive or management functions were abused.
What Fortinet reported
Fortinet’s PSIRT advisory describes CVE-2026-104286 as a path traversal and NULL-byte handling flaw affecting FortiMail 7.2, 7.4, 7.6, and 8.0 branches. Fortinet says exploitation has been observed in the wild and urges customers to apply workarounds while fixed versions are released. FortiMail 7.2 users are directed to move to 7.4 or later; FortiMail 7.4.9, 7.6.7, and 8.0.2 are listed as upcoming fixed releases for affected branches.
The vendor-published workaround is to disable IBE feature support, or alternatively remove the FortiMail management interface from internet exposure and restrict it to trusted private networks. For government contractors and SMBs, the second control is the bigger architectural lesson: appliance management planes should not be casually reachable from the public internet, even when the appliance itself protects a public-facing service.
Why this matters to SMBs and government contractors
FortiMail sits in a sensitive position. It is close to inbound and outbound email flow, often has privileged administrative access, and may store or process message-security artifacts that are useful for follow-on operations. A compromised mail-security appliance can become more than a single-device problem: it can give an attacker durable infrastructure inside the environment, visibility into communications, and a path to stage or exfiltrate data.
This is especially relevant for small businesses and defense-adjacent organizations that rely on edge appliances but may not monitor them with the same rigor as servers and endpoints. Attackers understand that gap. Edge devices, VPNs, mail gateways, and management consoles are high-value because they often sit outside normal EDR coverage and have inconsistent logging pipelines.
Defensive actions to take now
- Identify exposure first. Confirm whether any FortiMail management interface is reachable from the internet. If it is, restrict access immediately to VPN/private networks or tightly controlled administrative IP ranges.
- Apply Fortinet’s workaround. Disable IBE feature support where applicable and track Fortinet’s fixed releases for the affected branch.
- Hunt the appliance, not just the network. Review Fortinet’s listed file paths, hashes, IP indicators, and log patterns. Pay attention to unexpected archive-account changes, cron activity, modified binaries, preload configuration, and anomalous management events.
- Preserve logs before making changes. If exploitation is suspected, collect appliance logs, configuration exports, management access logs, and upstream firewall/VPN records before rebooting, upgrading, or wiping the device.
- Rotate exposed secrets. If the appliance was reachable or shows suspicious indicators, treat stored credentials, admin accounts, archive destinations, API keys, and integration secrets as potentially exposed.
- Validate outbound paths. Fortinet’s advisory includes indicators suggesting remote archive or upload behavior. Review egress from FortiMail to unusual destinations and alert on unexpected file transfer patterns.
Bulwark Black assessment
CVE-2026-104286 is a reminder that perimeter security products can become perimeter risk. The worst response is to treat this as a normal monthly patch item. The better response is a short, disciplined incident review: exposure check, workaround, IOC hunt, log preservation, credential review, and management-plane hardening.
For teams with limited staff, the priority order should be: remove public management exposure, apply Fortinet’s workaround, search for Fortinet’s indicators, and document the decision path. If you support regulated or government-contracting environments, that documentation matters. It shows that the organization understood this as an actively exploited KEV issue and responded based on risk rather than waiting for a routine maintenance window.
Sources: Fortinet PSIRT advisory FG-IR-26-175; CISA KEV alert; BleepingComputer reporting.