



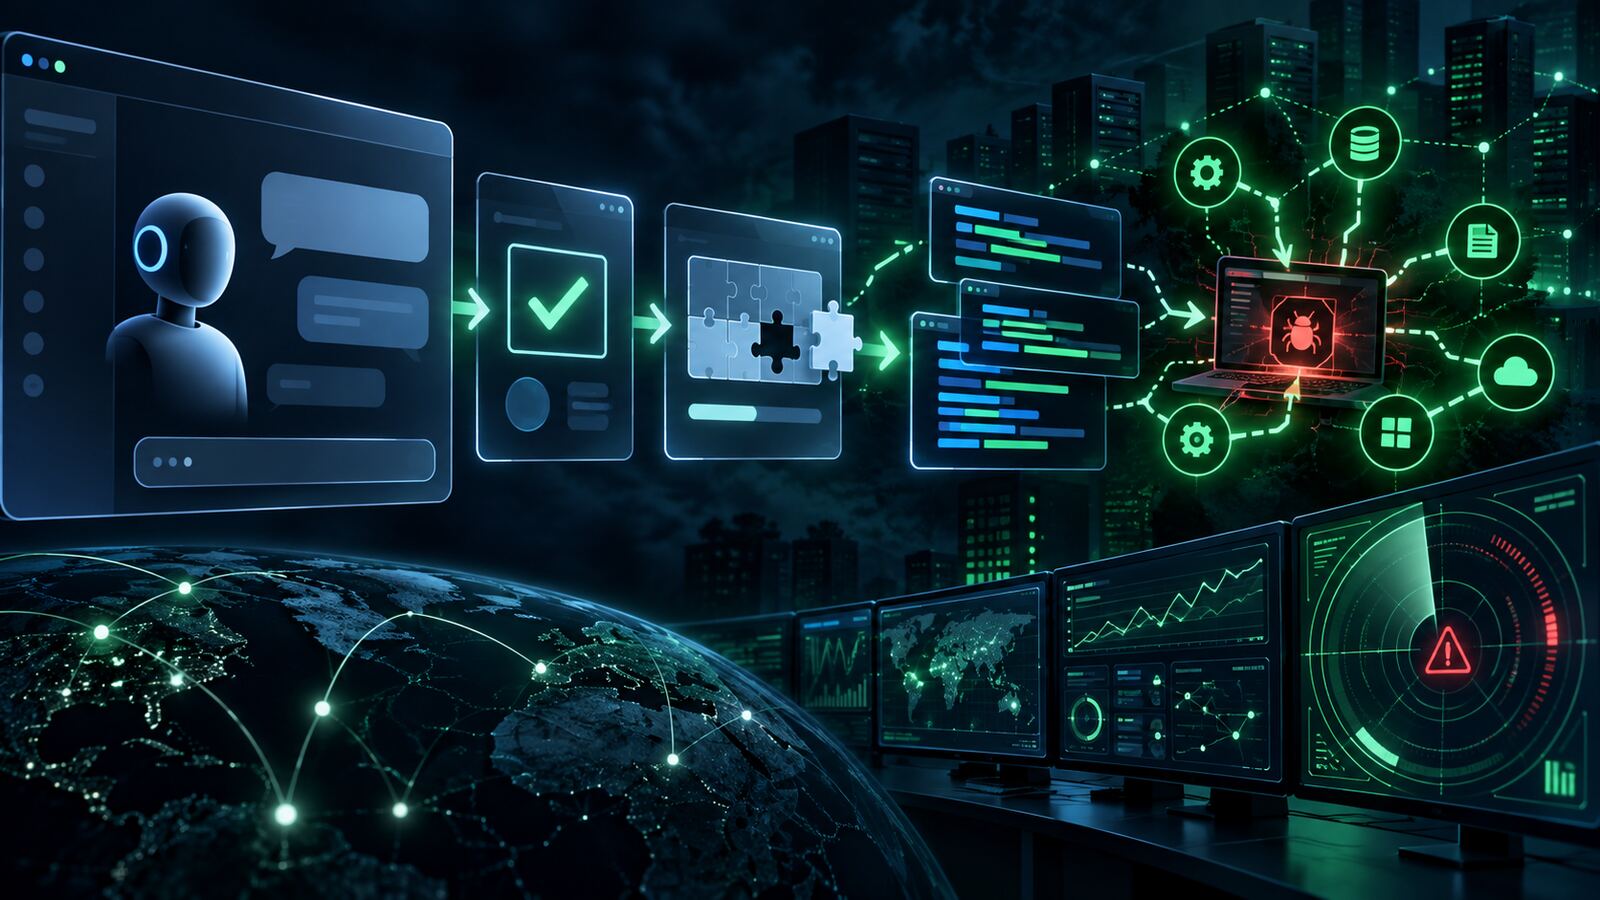
Attackers are continuing to turn trusted AI workflows into delivery infrastructure. Huntress reported a campaign where threat actors abused ChatGPT Custom GPT pages to steer victims into a fake “service availability” flow, then pushed them toward a Google Sites page posing as a verification check. From there, the attack became a ClickFix-style lure: the victim was instructed to paste and run a command, starting a multi-stage Windows malware chain.
The important lesson for small businesses and government contractors is not “do not use AI.” The lesson is that AI platforms now sit inside the user trust boundary. If a legitimate-looking AI page can convince a user to cross from browser interaction into shell execution, endpoint controls, user training, and identity response need to account for that path.
What Huntress Reported
According to Huntress, victims encountered an attacker-created Custom GPT that appeared to be a newer “Plus” style experience. The page lived on a legitimate ChatGPT domain, which made the lure more believable than a normal fake login page. The Custom GPT then directed users to a Google Sites “backup” page that imitated a CAPTCHA or verification workflow.
That fake verification page did not verify anything. It instructed the user to run a PowerShell command. Once executed, the command downloaded an obfuscated script, installed a malicious MSI package, and launched a sideloading chain built around legitimately signed software. Huntress’ analysis describes persistence through a Run key and scheduled task, additional loader stages, anti-analysis behavior, and a final remote access trojan with hands-on-keyboard capability.
The campaign matters because it blends several trends defenders are already seeing separately: malvertising, AI-platform impersonation, ClickFix social engineering, signed-binary abuse, DLL sideloading, and full remote access malware.
Why This Matters for SMBs and Government Contractors
Most organizations have trained users to be suspicious of random downloads and suspicious login pages. Fewer have trained users to reject instructions from a legitimate AI platform page that says, in effect, “open PowerShell and paste this.” That is the gap ClickFix abuses.
For government contractors, the risk is bigger than one infected workstation. A successful RAT deployment can expose proposal data, Controlled Unclassified Information, Microsoft 365 sessions, browser credentials, VPN access, cloud consoles, and customer communications. Even when the first machine is not a server, it can become the staging point for mailbox access, lateral movement, credential theft, or follow-on ransomware activity.
This is also a detection problem. The initial lure may happen entirely in the browser, while the damaging behavior appears moments later as PowerShell, msiexec, scheduled tasks, local application folders, and unusual signed binaries running from user-writable paths. If those signals are monitored in isolation, the intrusion can look like a series of unrelated oddities instead of one attack chain.
Defensive Takeaways
- Block browser-to-shell workflows where possible. Users should not need to paste commands from a webpage into PowerShell, Terminal, Run, or command prompt for normal business activity.
- Hunt for PowerShell spawning installer activity. Investigate PowerShell or script hosts that download content and launch
msiexec, especially when payloads land in temporary directories. - Watch signed binaries in strange places. Legitimate vendor executables running from
%LOCALAPPDATA%or other user-writable locations deserve scrutiny, especially when paired with nearby unsigned DLLs. - Correlate Run keys and scheduled tasks. Persistence mechanisms with matching names, repeated recreation, or links to unexpected local application paths should trigger incident review.
- Treat ClickFix as phishing, not user error. Add examples to security awareness training: real CAPTCHA checks do not require opening PowerShell or pasting commands.
- Prepare identity cleanup steps. If a RAT is suspected, rotate browser-saved passwords, revoke sessions, review mailbox rules, reset high-risk credentials, and check cloud audit logs.
Bulwark Black Assessment
This campaign is a good example of why AI security cannot be limited to prompt injection discussions. The attacker did not need to compromise the AI provider to benefit from the platform’s trust. They abused a legitimate feature, wrapped it in advertising and familiar verification language, then moved the victim into a classic endpoint compromise chain.
For defenders, the practical answer is workflow control. If a webpage asks a user to execute a shell command, that should be considered a high-risk behavior regardless of whether the page is hosted on a trusted domain. Pair that policy with endpoint detections for script-to-installer behavior, signed-binary sideloading, and persistence in user-writable paths, and the organization has a much better chance of catching this before it becomes a full credential and remote-access incident.
Original source: Huntress — Attackers Abuse ChatGPT Custom GPTs to Deliver RAT via ClickFix