Volexity’s latest reporting on UTA0565’s Chrome and Windows zero-day campaign is a useful reminder that browser patching is not a standalone control. The campaign used fake websites, hidden exploit delivery, and a Windows payload to turn believable web content into endpoint compromise.
For small businesses and government contractors, the important lesson is not only “patch faster.” It is that high-end exploit chains can arrive through ordinary-looking sites, policy content, media impersonation, or partner-adjacent links. Defense has to connect browser exposure, endpoint behavior, identity risk, and network egress into one incident story.
What Volexity reported
Volexity attributes this activity to a Chinese threat actor it tracks as UTA0565. The actor reused the same broader Chrome and Windows exploit chain Volexity had previously documented, but adapted the delivery to fake websites that impersonated legitimate organizations and media properties.
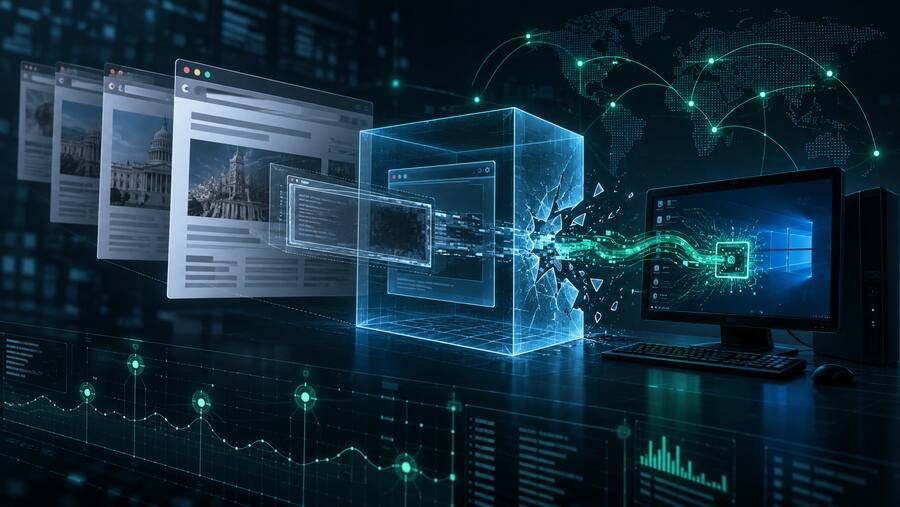
The campaign used typosquatted domains and copied legitimate site content to reduce suspicion. One observed site impersonated the Center for American Progress, loaded mostly legitimate content, and quietly included a hidden iframe that delivered exploit components. Another campaign used a spoofed China Digital Times domain in phishing aimed at Asian government entities.
The exploit chain involved Chrome vulnerabilities CVE-2026-85046 and CVE-2026-87491, followed by Windows local privilege escalation CVE-2026-85880. Volexity reported that the UTA0565 activity occurred on September 3–4, 2026, while the vulnerabilities were still unpatched.
The CLEANGULP payload
In this campaign, the final downloaded payload was a Windows executable Volexity tracks as CLEANGULP. According to Volexity, CLEANGULP installs under a Microsoft IME-looking path, persists with a scheduled task named MicrosoftIME, and supports operator commands such as shell execution, process listing, file upload, file download, and beacon object file execution.
That capability set matters because it is not noisy commodity malware behavior. It is enough to support hands-on-keyboard access, follow-on tooling, file collection, and stealthy post-exploitation inside an environment that may initially see only a browser visit and a suspicious Windows process.
Why this matters for SMBs and government contractors
Most smaller organizations do not have exploit-kit visibility at the browser layer. They depend on vendor patching, endpoint detection, DNS filtering, and user reporting. That is reasonable, but it leaves a gap when a site looks legitimate and the exploit does not require the victim to download an obvious attachment.
Government contractors should pay special attention because the lure themes in this case included policy, civil society, and media-style content. Those are normal browsing patterns for leadership, business development, compliance teams, analysts, and anyone tracking geopolitical or procurement-related developments.
Defensive takeaways
- Prioritize browser and OS patch velocity. Track Chrome/Edge and Windows patch status like externally exposed infrastructure, especially for executives, analysts, and users who research policy or threat topics.
- Hunt for browser-to-process anomalies. Alert when browser activity is followed by unexpected executable creation, scheduled task creation, COM-based launch behavior, or suspicious processes under user profile paths.
- Monitor scheduled tasks. Baseline legitimate tasks and investigate newly created tasks with trusted-looking names such as IME, updater, cleanup, browser, security, or support themes.
- Use DNS and web telemetry together. Look for typosquatted domains, newly registered domains, copied-site infrastructure, and beaconing to lookalike news or nonprofit domains.
- Segment high-risk browsing. Consider hardened browser profiles, isolation, or dedicated research workstations for users who routinely open foreign-policy, malware, or adversary-adjacent content.
- Correlate endpoint and identity quickly. If a browser exploit is suspected, assume credential access may follow. Review tokens, sessions, mailbox rules, VPN logins, and privileged account use.
Bulwark Black assessment
UTA0565 shows how mature operators are blending credible web impersonation with real exploit capability. The fake site is not just a phishing page; it is the delivery vehicle for a chained browser-to-OS compromise path.
The practical answer is layered control. Patch fast, but do not stop there. Watch for abnormal browser child-process activity, suspicious scheduled tasks, new executables in user profile paths, and outbound traffic to lookalike domains. For contractors handling CUI or working around federal customers, treat browser compromise as a possible identity and data-protection incident, not just an endpoint cleanup ticket.
Original source: Volexity — “Mind the (Patch) Gap, Part 2: Fake Websites Used to Deploy Chrome & Windows 0-Day Exploits”