
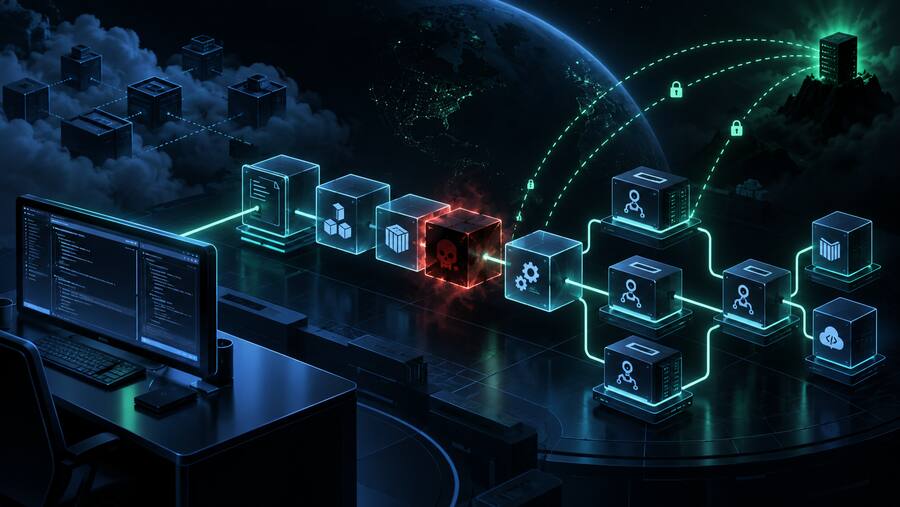


A suspected TraderTraitor campaign abusing a trojanized Terraform provider is a clean reminder that developer tooling is now part of the endpoint attack surface. The malware did not need to start as a suspicious email attachment. It hid inside the kind of executable plugin infrastructure engineers already expect Terraform to load.
Zscaler ThreatLabz reported that the campaign used a Go-based binary named terraform-provider-awsbeta_v1.0.0, masquerading as an AWS-related Terraform provider. The provider retained enough legitimate-looking scaffolding to appear functional while calling a malicious package during startup. That matters because Terraform providers execute on developer workstations and CI/CD runners — exactly where cloud credentials, repository access, deployment permissions, and production context often live.
What Zscaler found
The trojanized provider used a temporary session.lock marker to avoid repeated execution, then downloaded a Bash loader over HTTPS from infrastructure designed to look like legitimate Terraform-related activity. The loader wrote a file named safari_updater and continued the infection chain across macOS, Linux, and Windows environments with Unix-like shell support.
The next-stage payloads were disguised as web font files. The loader mapped operating systems and CPU architectures to believable font-family and style names, then downloaded encrypted .woff-like files from multiple sources including dynamic DNS, GitHub, and Vercel-hosted infrastructure. After a marker in the file, the loader extracted and decrypted an executable payload using locally available tools such as Python, Node.js, Perl, or OpenSSL.
Zscaler assessed the payloads as consistent with FLATROOF, a cross-platform Rust backdoor linked to TraderTraitor-related activity. The malware supported Telegram Bot API, GitHub API polling, and HTTP webhook channels for tasking and exfiltration. Zscaler also identified related ROOFDECK variants using layered command-and-control discovery through local configuration, Pastebin, and Nostr metadata.
Why this matters
This is not just a malware story. It is a trust-boundary story. Terraform providers are executable code. They are often pulled into environments where defenders focus heavily on cloud misconfiguration but less on the workstation or build runner that drives those cloud changes.
For SMBs, SaaS teams, MSPs, and government contractors, infrastructure-as-code systems often hold the keys to the kingdom: cloud API tokens, deployment roles, state files, SSH material, secrets references, and privileged network paths. If a malicious provider runs in that context, the attacker may not need to exploit the cloud platform directly. They can compromise the person or pipeline authorized to manage it.
The campaign also shows why “developer endpoint” does not only mean a laptop. CI/CD workers, build containers, self-hosted runners, automation hosts, and ephemeral deployment boxes all execute tooling. If they can apply infrastructure, they can also be abused to stage malware, collect secrets, or create persistence.
Defensive takeaways
- Treat Terraform providers like software dependencies. Pin provider sources and versions, review unexpected provider names, and avoid installing lookalike packages from untrusted locations.
- Restrict provider installation paths. Monitor plugin cache directories, temporary execution paths, and unusual provider binaries appearing outside approved workflows.
- Lock down CI/CD egress. Build runners rarely need unrestricted outbound access. Alert on connections to dynamic DNS, paste sites, unfamiliar GitHub repositories, Vercel-style staging domains, Telegram APIs, or new webhook endpoints.
- Separate deployment identities. Do not let developer workstations and build runners inherit broad human admin tokens. Use scoped roles, short-lived credentials, and environment-specific permissions.
- Harden state and secrets handling. Terraform state, provider config, environment variables, cloud credential files, and repository secrets should be treated as high-value data.
- Monitor developer endpoints for post-install behavior. Watch for scripts dropped into temporary directories, unexpected executable permission changes, shell-spawned child processes, browser credential access, keychain access, and persistence creation.
- Review public-hosting dependencies. GitHub and Vercel are normal developer infrastructure, which makes them useful for attackers. Baseline expected repositories and domains instead of blanket-trusting the platform.
What to do this week
Start by listing where Terraform runs: laptops, CI/CD systems, automation servers, self-hosted runners, containers, and managed build services. For each location, identify which credentials are available at runtime and whether outbound traffic is restricted.
Next, review provider configuration. Look for unexpected provider names, recently added provider sources, provider binaries stored outside normal cache paths, and workflows that download tooling with generic shell commands. If your team uses private providers, document the expected source, checksum strategy, and update process.
Finally, add a small set of practical detections: Terraform or shell processes launching from temporary directories, provider binaries creating child processes, build runners contacting Telegram or paste services, and CI/CD jobs accessing browser, keychain, SSH, or cloud credential stores. Those signals are more useful than waiting for a perfect malware family signature.
Bulwark Black assessment
The lesson is straightforward: infrastructure-as-code is production access in executable form. A fake provider is not just a poisoned dependency; it is a potential bridge from developer trust into cloud control.
Organizations should handle Terraform providers, CI/CD runners, and developer automation with the same seriousness they apply to privileged endpoints. Verify provenance, reduce egress, scope credentials, and make sure build systems are observable. The attacker path is getting more developer-native. Defensive controls need to meet it there.
Source: Zscaler ThreatLabz — Trojanized Terraform Provider Campaign.