
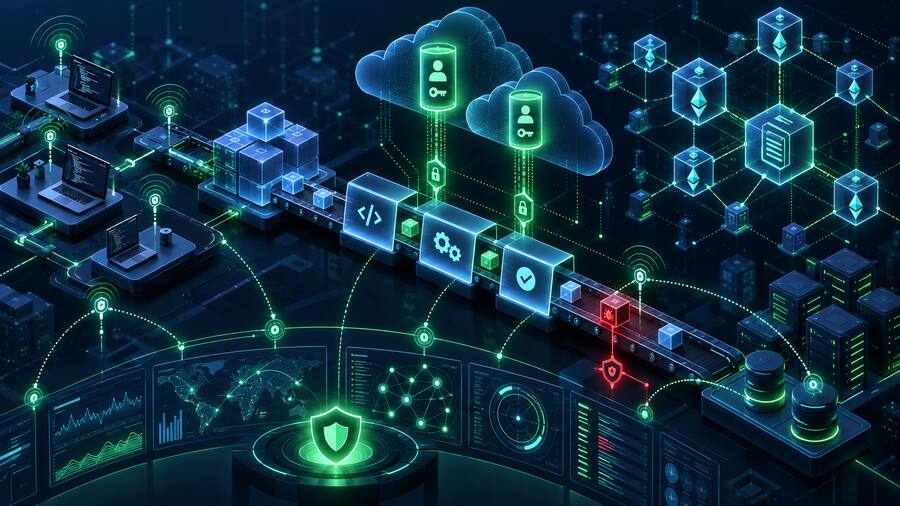







Unit 42’s latest research is a useful reminder that software supply-chain risk is no longer just about malicious packages reaching developer laptops. The more serious pattern is what happens next: poisoned dependencies are being engineered to steal cloud credentials from developer workstations and CI/CD runners, then use decentralized Web3 infrastructure to keep command-and-control resilient.
The core issue is simple. Modern build environments often hold the keys to the kingdom: cloud identity tokens, service account credentials, deployment secrets, package-registry tokens, signing material, and short-lived OIDC credentials. If a malicious package executes during install, build, workspace load, or test automation, the attacker may not need to phish an administrator. They can compromise the automation path that already has privileged access.
Source: Unit 42, “Evolution of Web3 in Cloud Supply Chain Attacks”.
What Unit 42 Reported
Unit 42 describes an evolution in supply-chain malware where command-and-control is no longer limited to static domains, hard-coded IP addresses, or conventional malware infrastructure. Campaigns such as ChainDrop and PolinRider show attackers using Web3 mechanisms — including smart contracts, transaction data, and zero-data wallet activity — to dynamically resolve infrastructure.
That matters because traditional takedown and blocklist models assume there is a domain, IP, or fixed endpoint to remove. Web3-based resolution changes the defensive problem. A malicious loader can query public blockchain infrastructure, retrieve or derive the current C2 endpoint, and shift infrastructure without republishing the malicious package.
Unit 42 also connects this trend to cloud-focused supply-chain intrusion. The target is not just cryptocurrency. The target is enterprise cloud access: developer secrets, CI/CD tokens, cloud IAM credentials, and deployment paths that can provide durable access into production environments.
Why This Matters for SMBs and Government Contractors
Small and mid-sized organizations often underestimate how much authority their build systems have. A single GitHub Actions runner, self-hosted build agent, developer workstation, or package publishing workflow may be able to deploy code, read secrets, push containers, access cloud storage, or assume production roles.
For government contractors, the risk compounds. A compromised developer pipeline can expose customer data, controlled project artifacts, software deliverables, cloud environments, and downstream partners. Even if the organization is not building Web3 products, its developers may still reach public blockchain RPC gateways if malware uses them as infrastructure.
The uncomfortable defensive takeaway: if your business has no legitimate blockchain use case, outbound Web3 traffic from build systems should be treated as a strong anomaly, not background noise.
The Defensive Pivot: Watch the Build Path, Not Just the Endpoint
Most organizations already know to scan dependencies. That is necessary, but it is not enough. Modern supply-chain malware is increasingly designed to execute through lifecycle hooks, workspace automation, repository configuration, build scripts, IDE behaviors, and runner context. Defenders need visibility into what build tools do after dependency resolution begins.
Practical controls should include:
- Baseline outbound traffic from CI/CD runners. Build systems should have a narrow expected egress profile. Public blockchain RPC gateways, unknown VPS providers, paste sites, and newly registered domains should stand out quickly.
- Restrict secrets available to builds. Do not expose production credentials to every pipeline job. Use short-lived credentials, scoped roles, environment protections, and approval gates for sensitive deployments.
- Separate build, test, and deploy authority. A dependency install step should not have the same access as a production deployment step.
- Audit package lifecycle hooks. Pay close attention to preinstall, postinstall, prepare, build, and workspace automation behaviors across npm, Python, Go, Rust, PHP, and container build contexts.
- Monitor process context, not just destinations. A browser reaching a crypto site is one signal. A compiler, package manager, shell, Bun/Node runtime, or CI runner querying blockchain infrastructure is a much higher-confidence signal.
- Rotate secrets after suspicious build activity. If a build runner executed untrusted code, treat exposed environment variables and tokens as compromised until proven otherwise.
What to Hunt For
Security teams can start with a focused set of detections that do not require a large SOC:
- Package managers or build runtimes initiating outbound connections to public blockchain RPC endpoints.
- Unexpected execution of Bun, Node, Python, PowerShell, curl, wget, or shell interpreters during dependency install.
- New or modified package lifecycle scripts in repositories, lockfiles, or dependency manifests.
- CI/CD jobs reading unusually broad environment variables or secret stores.
- Build agents making outbound connections to infrastructure unrelated to source control, artifact repositories, vulnerability scanners, or deployment targets.
- Developer workstations with wallet-like, blockchain-RPC, or transaction-query traffic despite no approved Web3 business function.
Bulwark Black Assessment
This is the next logical stage of supply-chain compromise. Attackers are no longer satisfied with publishing a malicious package and hoping an endpoint tool catches it. They are designing packages to survive takedown, evade static infrastructure blocking, and steal the temporary cloud credentials that make modern development fast.
The strongest defense is not a single tool. It is reducing trust in the build path. Treat CI/CD as production infrastructure. Limit what jobs can access. Make egress explicit. Inspect lifecycle hooks. Keep developer and deployment identities separate. Most importantly, rehearse the response path for a compromised package: identify where it ran, what secrets were exposed, what cloud roles were reachable, and what must be revoked immediately.
For organizations without a Web3 business need, the first quick win is straightforward: inventory and restrict blockchain-related network access from developer systems and build environments. If that traffic appears anyway, investigate it like a potential supply-chain incident.