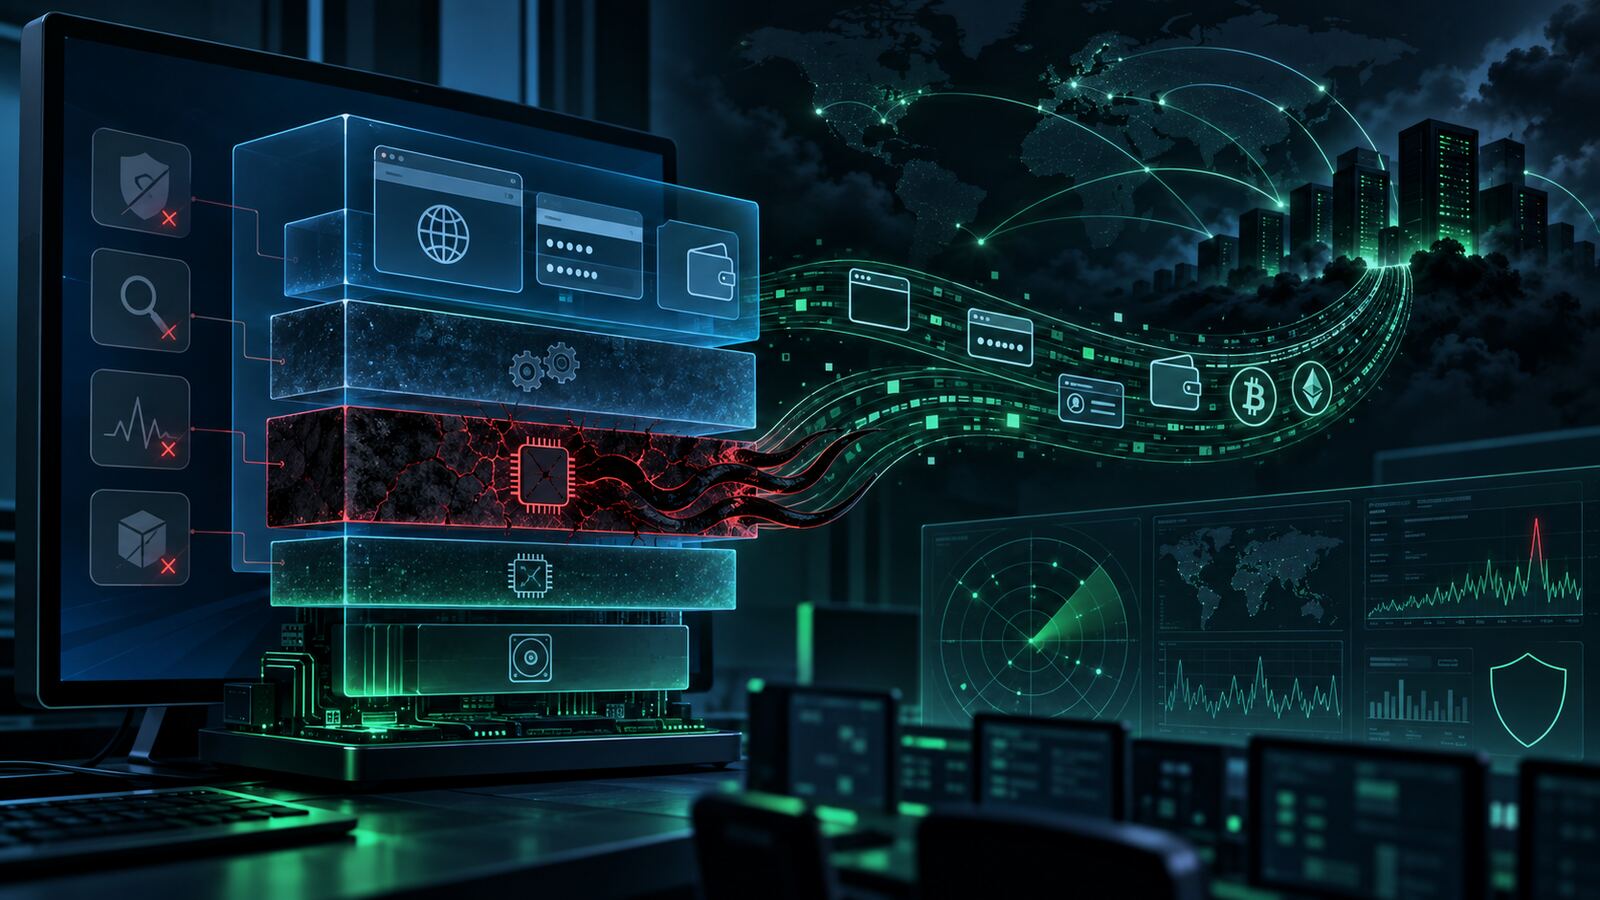
Information stealers are usually treated as noisy commodity malware. Lunex deserves more attention because it combines familiar credential theft with a more advanced pre-theft move: abusing a vulnerable signed driver to interfere with endpoint security before the final stealer runs.
Ontinue’s analysis of the Lunex malware-as-a-service platform describes a four-stage chain aimed at Ukrainian-speaking users. The campaign starts with fake CAPTCHA-style delivery, installs a loader, abuses the vulnerable AMD PDFWKRNL.sys driver associated with CVE-2023-20598, then deploys the final Lunex/Psychedelic Stealer payload. The Hacker News also summarized the findings and the broader infrastructure growth around the platform.
Why this one matters
The important part is not just that another stealer is harvesting browser passwords, cookies, and wallet data. The important part is that Lunex uses a bring-your-own-vulnerable-driver technique before the stealer stage. That puts it closer to ransomware tradecraft, where attackers routinely try to weaken EDR before deploying their main payload.
For small businesses and government contractors, that changes the risk calculation. A single infected workstation may expose browser-stored credentials, session cookies, SaaS access, crypto wallets, developer accounts, and remote file access. If the endpoint tool is blinded instead of cleanly terminated, the incident may look less severe than it really is.
What defenders should notice
- Fake verification pages are still working. ClickFix-style lures keep succeeding because they turn the user into the execution mechanism.
- Signed drivers are not automatically safe. Vulnerable legitimate drivers can give malware kernel-level leverage without looking like a traditional exploit kit.
- Browser persistence is becoming more operationally useful. Native messaging hosts and malicious extension manipulation can survive simple binary removal and keep access near the user’s active sessions.
- Credential theft is an identity incident. Treat stolen cookies, OAuth sessions, saved passwords, and wallet data as compromise paths — not cleanup artifacts.
Practical defensive takeaways
- Block known vulnerable drivers. Review Microsoft vulnerable driver blocklist coverage, WDAC/App Control policy, and EDR-specific driver controls. Do not assume the default blocklist catches every abused variant.
- Monitor driver load events. Alert on unusual service creation and kernel driver loads from user-writable locations, especially under
%LOCALAPPDATA%, temp paths, or recently created directories. - Reduce browser credential exposure. Push users toward managed password vaults, phishing-resistant MFA, session controls, and conditional access rather than saved browser passwords alone.
- Audit Chrome native messaging hosts and extensions. Unapproved native messaging host registrations should be treated as suspicious, especially after stealer detections.
- Reset identity, not just the endpoint. After an infostealer event, rotate passwords, revoke sessions, refresh OAuth tokens, review mailbox rules, and inspect SaaS audit logs.
Bulwark Black assessment
Lunex is a good example of where commodity malware is heading: less “grab passwords and leave,” more “disable visibility, install durable browser access, and monetize identity.” The defensive answer is not one magic detection. It is layered control: restrict driver abuse, harden browsers, limit credential reuse, and make identity telemetry part of endpoint incident response.
Original research: Ontinue — Lunex Unmasked: A New Information Stealer Deployed Through BYOVD. Additional reporting: The Hacker News.