Source: Group-IB, “RemControl: AI Built the Overlays. Victims Lose their PINs”
Group-IB has reported a previously undocumented Android banking trojan called RemControl, and the useful lesson is bigger than one mobile malware family. The campaign combines familiar mobile-fraud tradecraft — fake app pages, abuse of Android Accessibility Service, banking overlays, keystroke capture, screen streaming, and remote control — with a more industrial backend: exposed panel documentation, affiliate-style campaign tracking, dynamic infrastructure, and signs that parts of the criminal workflow were built with AI assistance.
For SMBs, banks, credit unions, fintech vendors, and government contractors with mobile workforces, this is a reminder that mobile devices are now part of the identity perimeter. If an employee’s phone can approve MFA prompts, access email, open financial portals, or receive recovery codes, then a mobile banking trojan is not just a consumer fraud problem. It is an identity, payments, and help-desk risk.
What Group-IB reported
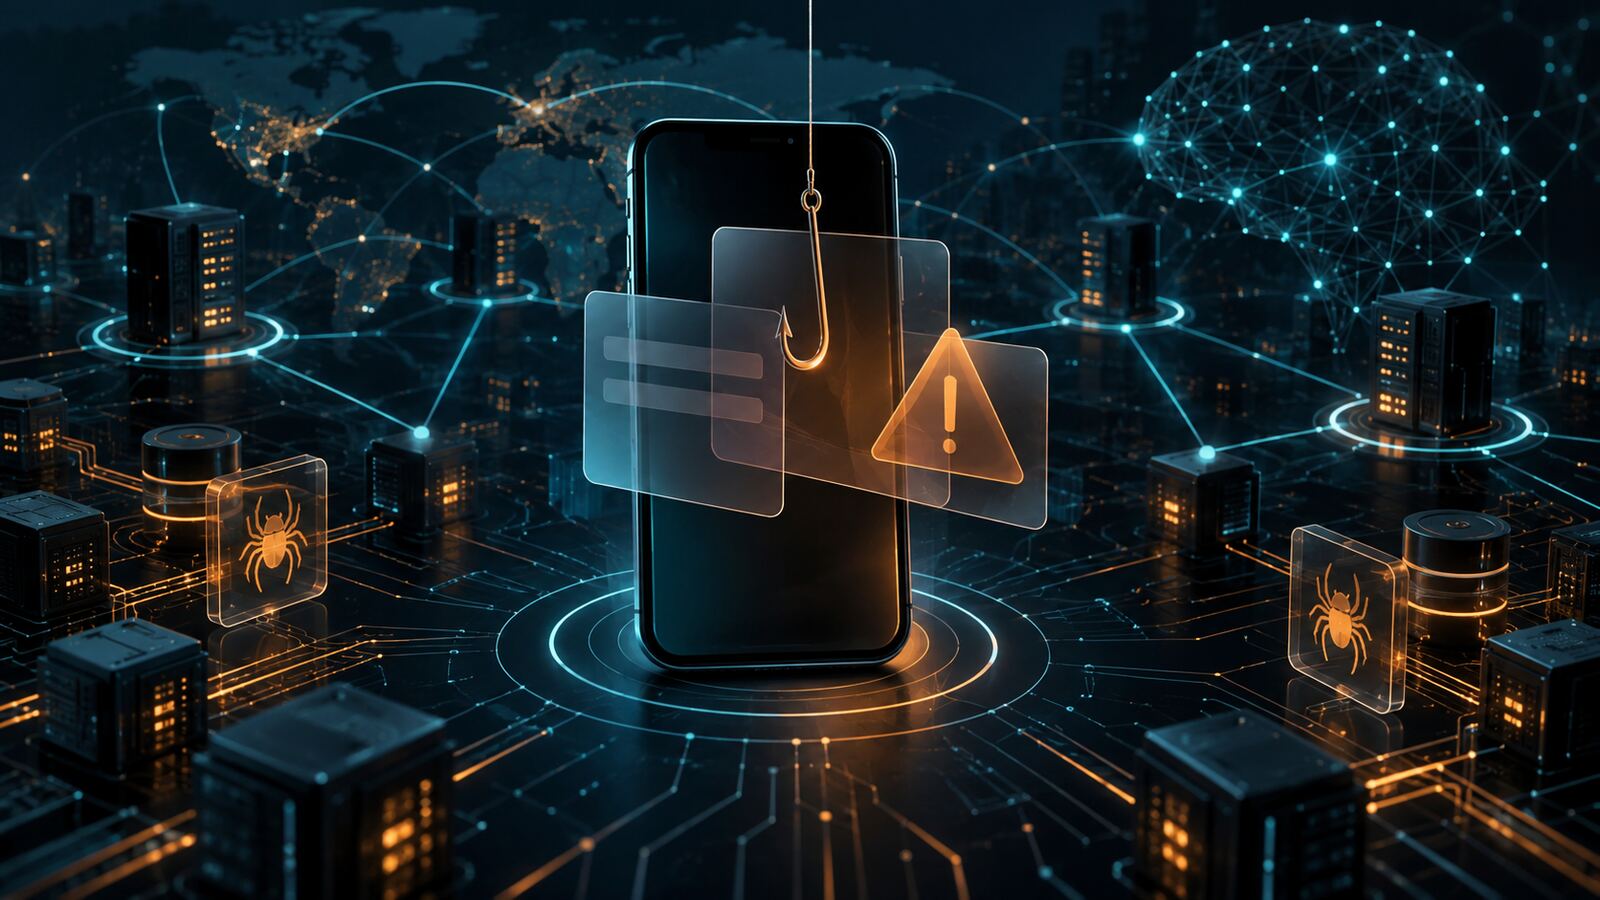
According to Group-IB, RemControl targets retail banking users in Western Europe, the Middle East, and Canada. The malware is distributed through fake Google Play Store-style pages impersonating a third-party IPTV application, with malvertising identified as one delivery path.
Once installed, the trojan abuses Android Accessibility Service to display phishing overlays over legitimate banking apps, capture user input, stream the victim’s screen, and give operators remote control of the device. Group-IB also observed techniques meant to make detection and takedown harder, including dynamic command-and-control resolution through an encrypted Telegram dead drop, per-install signing certificate generation, and attempts to interfere with Google Play Protect during installation.
The infrastructure matters as much as the malware. Group-IB found exposed operator-panel API documentation that described overlay management, build functions, commands, affiliate tracking, and campaign mechanics. The researchers also found AI-assistance artifacts in the criminal infrastructure, including an AI assistant response left inside a live phishing page.
Why this matters for defenders
RemControl is a clean example of how mobile fraud operations are becoming easier to scale. The core attack path is not exotic: trick a user into installing a fake app, request dangerous permissions, overlay the real banking app, steal credentials or PINs, then remotely complete fraud while the victim thinks they are interacting with a legitimate screen.
The newer concern is operational efficiency. If criminals can use AI to generate overlay pages, panel code, documentation, localization, and affiliate infrastructure faster, defenders should expect more variants, more regional targeting, and faster retooling after takedowns. Even sloppy AI-generated artifacts do not make a campaign harmless. They can still help a low-skill operator ship working fraud infrastructure.
That has direct implications for organizations that rely on personal or lightly managed phones for business workflows. Mobile malware can become the first step in account takeover, payment diversion, payroll fraud, help-desk social engineering, or recovery-code interception.
Defensive takeaways
- Treat mobile devices as identity infrastructure. If phones approve MFA, access email, or receive recovery codes, include them in security architecture, monitoring, and incident response.
- Restrict risky app installation paths. For managed devices, block unknown sources, enforce app-store allowlisting where possible, and use mobile device management policies for high-risk roles.
- Monitor for Accessibility Service abuse. Accessibility permissions are powerful. MDM/EMM tools should flag unexpected accessibility grants, screen-sharing behavior, and device-admin changes.
- Reduce SMS and push-only dependence. Strong phishing-resistant MFA and number-matching controls reduce the blast radius when a mobile device is compromised.
- Harden payment and banking workflows. Require out-of-band verification for new payees, payroll changes, wire instructions, and vendor-bank-account updates. Do not let a single mobile session authorize high-risk financial actions.
- Train users on fake app-store pages. The practical rule is simple: if a page outside the official app store asks for an APK install, it should be treated as hostile until proven otherwise.
- Build a mobile compromise playbook. Include token revocation, password resets, banking contact steps, device isolation, screenshots/log preservation, and review of recent payment or identity changes.
Bulwark Black assessment
RemControl is not just another Android banking trojan story. It shows the direction of travel: mobile fraud, malware-as-a-service mechanics, AI-assisted build workflows, and identity compromise are converging.
For small businesses and government contractors, the best response is not to chase every new mobile malware family by name. The better move is to close the repeatable failure points: unmanaged devices, risky app installation, weak MFA recovery paths, over-trusted mobile approvals, and payment processes that assume the person holding the phone is the legitimate user.
If a phone is allowed to approve access, move money, or reset credentials, it needs the same seriousness as a laptop on the network.
Original research: Group-IB — RemControl: AI Built the Overlays. Victims Lose their PINs