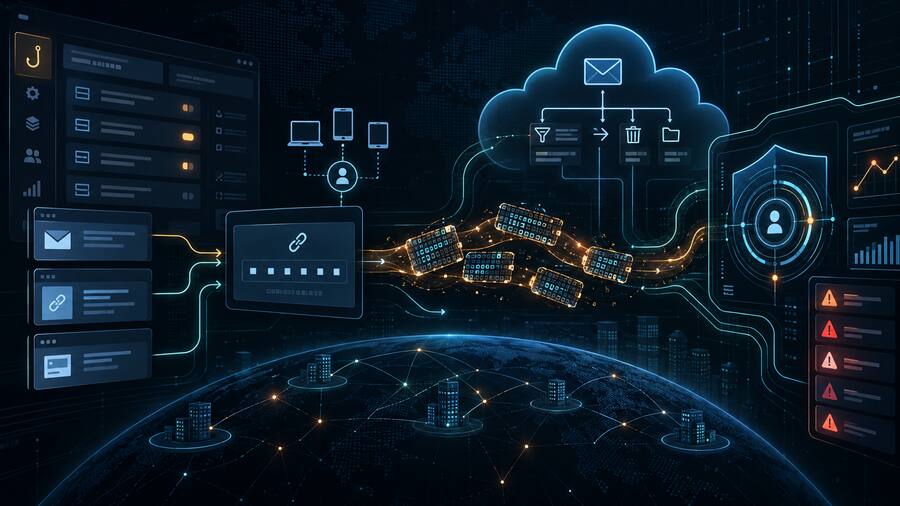
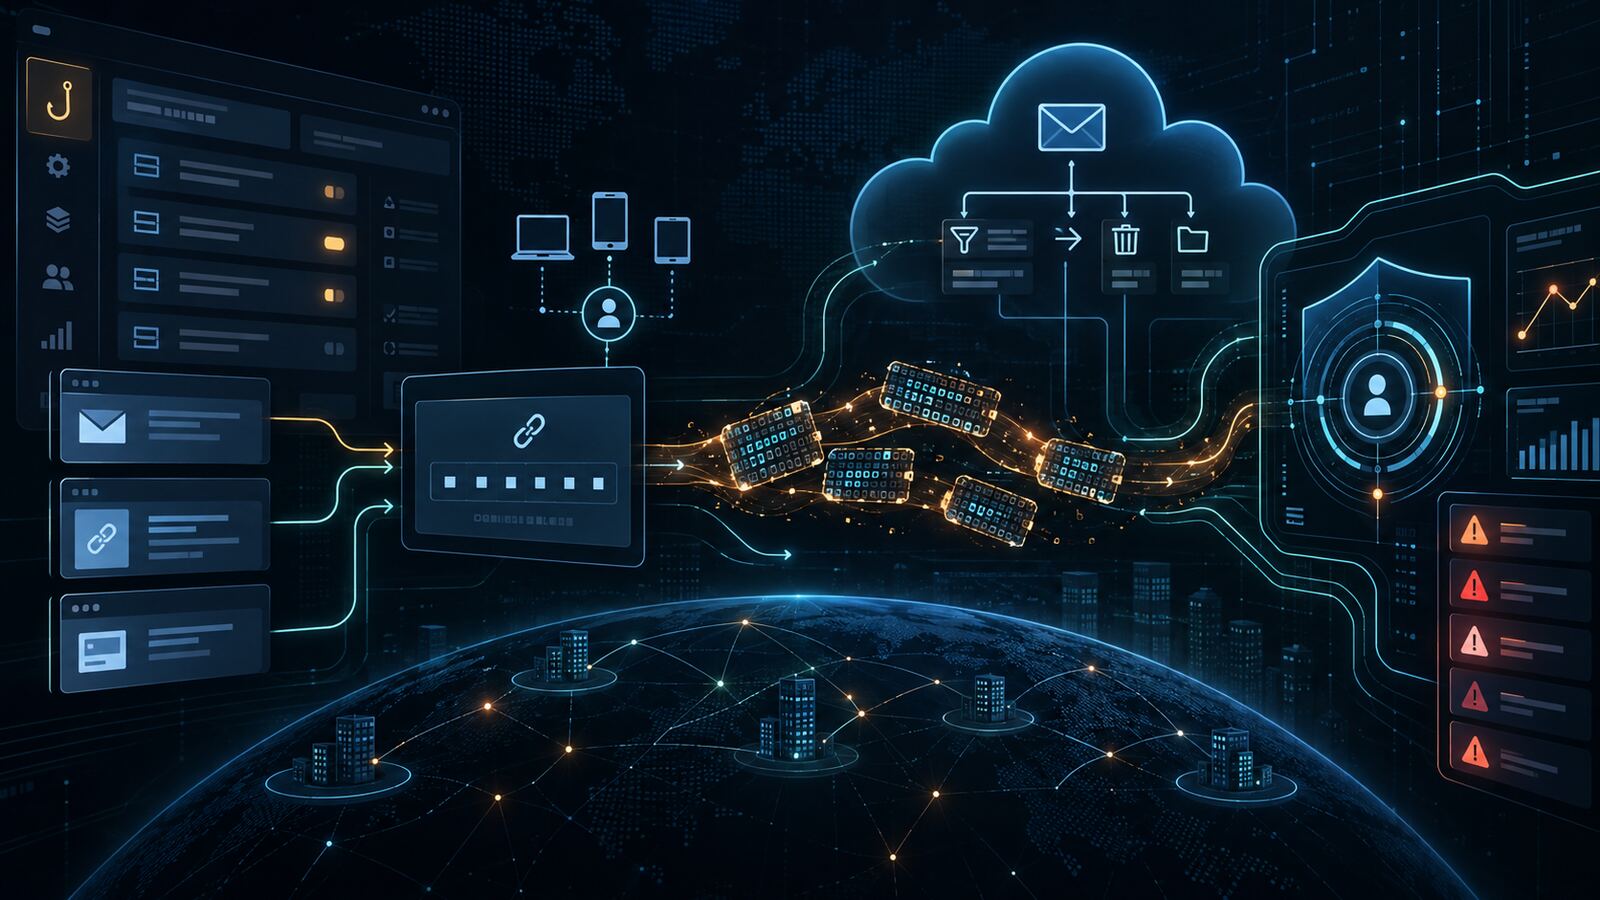
Microsoft’s latest EvilTokens reporting is a clean reminder that multifactor authentication is not the finish line for identity security. The campaign abused the legitimate Microsoft device code authentication flow to authorize attacker-controlled sessions, then used stolen tokens for mailbox access, Microsoft Graph reconnaissance, inbox-rule persistence, and business email compromise activity.
According to Microsoft, EvilTokens emerged in February 2026 and helped compromise more than 12,000 inboxes across over 10,000 organizations. The platform operated as phishing-as-a-service, giving affiliates prebuilt lures, landing pages, token capture workflows, AI-assisted email generation, victim tracking, and post-compromise tooling. Microsoft tracks the developer/operator behind the kit as Storm-2992 and says its Digital Crimes Unit coordinated a disruption of EvilTokens infrastructure with partners.
What makes this different
Device code phishing is dangerous because the user can complete authentication on a legitimate Microsoft page while unknowingly approving a session started by the attacker. The victim is not handing over a password to a fake login form in the classic sense. They are entering a code into a real identity portal, which makes the social engineering harder to explain and easier to miss in training.
EvilTokens industrialized that flow. Microsoft describes campaigns using invoice, RFP, shared-file, voicemail, eFax, password-expiration, and cloud-service themes; redirects through high-reputation platforms; fake CAPTCHA gates; and serverless infrastructure such as Cloudflare Workers, Vercel, and AWS Lambda. After a token was captured, operators could search mailbox content, identify executives or finance staff, map organizational relationships through Microsoft Graph, create inbox rules, and in some cases register devices for longer-term persistence.
Why SMBs and government contractors should care
This is exactly the kind of tradecraft that hurts smaller organizations. It does not require a zero-day, a noisy malware payload, or domain admin on day one. A single approved device-code session can give an attacker enough mailbox visibility to understand invoices, contracts, subcontractor relationships, bid timing, CUI-adjacent workflows, and executive approval chains.
For government contractors, the risk is bigger than email fraud. A compromised Microsoft 365 account can expose proposal data, procurement conversations, partner contact graphs, document links, and internal approval processes. If the attacker can preserve access with malicious inbox rules or refreshed tokens, the incident can turn into a long-running intelligence collection problem rather than a one-time phishing event.
Defensive takeaways
- Block device code flow by default. If your environment does not have a real business need for it, disable or restrict it with Conditional Access. If Teams rooms or shared devices require it, scope exceptions narrowly to those resource accounts.
- Treat token theft as active access, not just a password problem. Resetting a password may not be enough. Revoke sessions, force reauthentication, and consider temporarily disabling the account during containment when hands-on activity is suspected.
- Hunt for suspicious inbox rules. Look for rules that delete, archive, forward, or hide security notices, invoices, wire instructions, MFA alerts, and executive correspondence.
- Monitor Graph and mailbox behavior. New consent patterns, unusual Graph queries, mailbox searches, device registration, and access from unfamiliar infrastructure should be investigated together.
- Harden email controls against lures. Safe Links, anti-phishing policies, spoof protections, ZAP, attachment detonation, and user-reporting workflows all matter because EvilTokens used multiple delivery styles.
- Train users on the specific device-code pattern. The key message is simple: do not enter a device login code unless you personally initiated the sign-in on a device you control and expect.
Bulwark Black assessment
EvilTokens is another sign that identity security has shifted from “protect the password” to “protect the session.” MFA still matters, but attackers are increasingly targeting the authorization flows around MFA: device codes, OAuth consent, session cookies, refresh tokens, and mailbox persistence. The organizations that handle this well will be the ones that combine Conditional Access design, token revocation playbooks, mailbox-rule hunting, and identity telemetry review into one incident response motion.
Original source: Microsoft Security — “Unmasking EvilTokens: Getting to the root of device code phishing”.