


Showing 49–72 of 180 reports
PackClient Shows Why Phishing Defense Needs Execution Controls
Proofpoint reported TA4922 using PackClient in tax-themed phishing campaigns. The defensive lesson for SMBs and government contractors is to control the execution chain after the click.
Signed ClickOnce Lures Show Why Hiring Workflows Need Endpoint Guardrails
A fake Web3 interview chain used signed ClickOnce delivery to deploy credential stealers and a Go hVNC RAT. Here is what SMBs and government contractors should tighten now.
AI-Enabled Malware Still Behaves Like Malware
Unit 42’s telemetry shows most AI-enabled malware remains experimental, but the real risk is faster iteration and AI-branded delivery. Defenders still win by watching behavior, identity, signing, and execution.
BTR.sys Shows Why Trusted Security Drivers Need Behavioral Monitoring
Check Point Research shows how Microsoft Defender’s boot-time remediation driver can be repurposed for privileged file and registry operations. The defensive lesson is simple: monitor trusted security components by behavior, not signature alone.
WeedHack Shows SEO Poisoning Is Malware Delivery Infrastructure
McAfee says WeedHack is still using fake gaming sites, SEO poisoning, Discord links, MediaFire, and GitHub-style trust signals to deliver malware. The same playbook can hit business users searching for tools and downloads.
Fake AI Tools Show Brand Trust Has Become Malware Delivery
Sophos X-Ops found attackers repeatedly impersonating AI brands with fake installers, malicious extensions, phishing lures, and AI-assisted tooling. The near-term defense is not exotic: approved sources, browser governance, endpoint telemetry, DNS controls, token hygiene, and clear AI software rules.
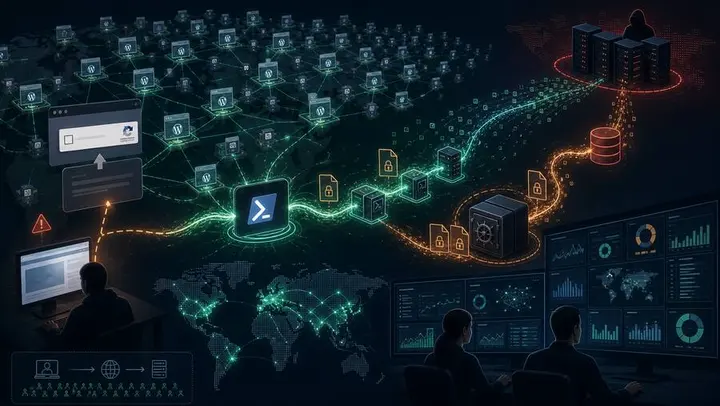
StopAndProtect Shows Why WordPress Sites Are Attack Infrastructure
Check Point Research exposed StopAndProtect, an operation abusing thousands of compromised WordPress sites for ClickFix delivery, malware staging, command routing, victim logging, data theft, and ransomware. The practical lesson: public websites need the same ownership, telemetry, and incident-response discipline as other production infrastructure.
MacSync Stealer Shows Why Behavioral Pivots Beat Rotating Domains
Microsoft Defender Experts expanded MacSync Stealer tracking from a small domain set to 30+ related domains by correlating durable endpoint and network behaviors. For defenders, the lesson is to hunt the attack chain—not just the rotating infrastructure.
C2Looper Shows Why GitHub-Based C2 Belongs in Ransomware Triage
Zscaler ThreatLabz found C2Looper, a Rust-based backdoor that evolved to use GitHub for command-and-control. Here is what SMBs and government contractors should monitor before trusted-platform abuse becomes ransomware.
Ransomware’s Long Tail Means Defenders Need Faster Triage
Check Point Research’s Q2 2026 ransomware data shows a wider operator ecosystem, faster exploitation windows, and lower payment rates. Here is what SMBs and government contractors should harden first.
Signed ClickOnce Shows Fake Interviews Are Now a Credential-Theft Delivery System
A fake Web3 interview chain used a signed ClickOnce app to deliver stealers and a RAT. Here is what SMBs and government contractors should change in endpoint, identity, and hiring-workflow defenses.
Dropcatch Domains Show Why Reputation Is Not Trust
Threat actors are buying expired domains with inherited reputation, backlinks, and traffic, then using them for redirects, scams, malware, and command-and-control. Here is what SMBs and government contractors should harden first.
HoneyMyte’s CoolClient Rootkit Shows Why Kernel Visibility Matters
HoneyMyte’s CoolClient backdoor now includes signed kernel-mode rootkit capabilities, raising the bar for driver monitoring, Defender exclusion review, and post-compromise endpoint validation.
Evooo1Bot Shows Why Exposed Linux and Edge Devices Are Still High-Value Targets
FortiGuard Labs documented Evooo1Bot, a Linux botnet combining Mirai-style DDoS with SSH brute forcing, SOCKS relay, credential sniffing, persistence, and exploit-driven infection of exposed devices.
Malware Crypting Services Show Why Behavioral Detection Matters
Recorded Future’s look at malware crypting services shows why SMBs and government contractors need behavioral detection, endpoint telemetry, and incident response—not just clean file scans.
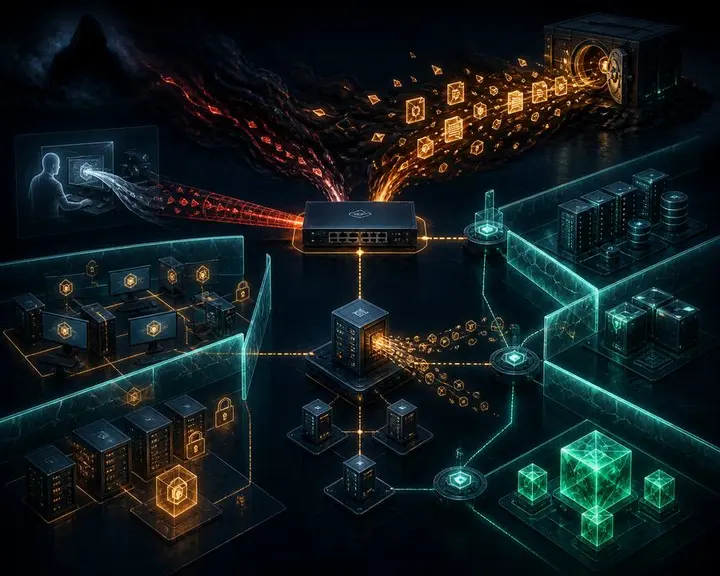
Gunra Ransomware Shows Why VPN Compromise Is an Incident, Not a Patch Ticket
Gunra ransomware activity tied to Fortinet VPN exploitation shows why edge-device compromise requires incident response: credential review, session validation, segmentation checks, and backup protection — not just patching.
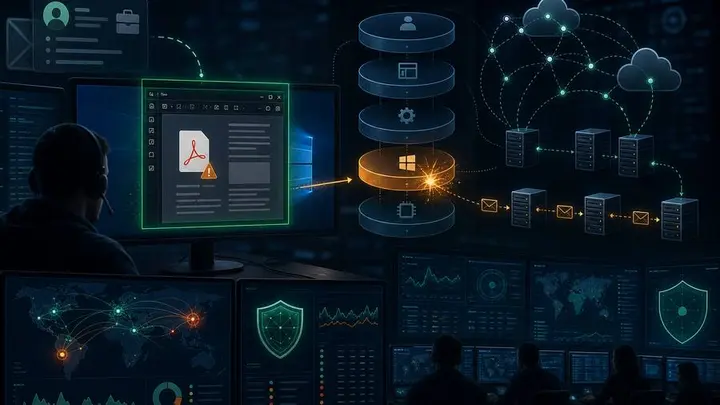
Lazarus Dream Job Campaign Turns Fake Recruiting Into a Windows Zero-Day Intrusion
Check Point Research reports a new Lazarus Operation Dream Job wave using fake recruiting lures, trojanized PDF tooling, Microsoft Graph/OneDrive C2, Roundcube relay infrastructure, and the patched CVE-2026-68820 Windows AFD.sys zero-day.
Deno Runtime Abuse Shows Why Developer Tooling Needs Security Governance
Sophos MDR observed attackers bringing the legitimate Deno runtime into intrusions to execute malicious JavaScript through less-monitored paths. Here is what SMBs and government contractors should monitor.
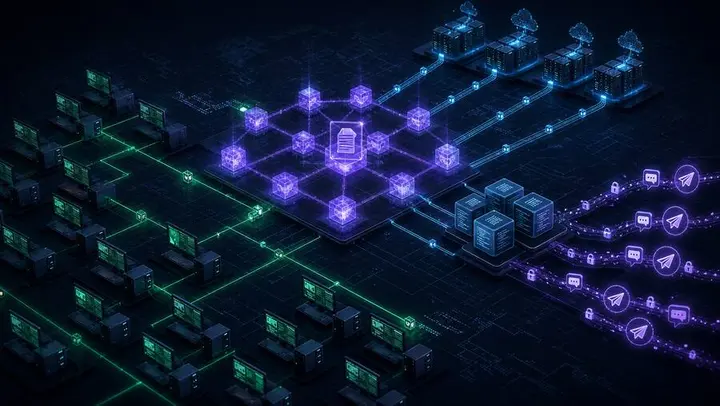
Aeternum Shows Why Blockchain-Based C2 Is a Practical Defense Problem
Aeternum uses Polygon smart contracts, GitHub staging, and Telegram exfiltration to make botnet command-and-control more resilient. Here is what SMBs and government contractors should watch for.
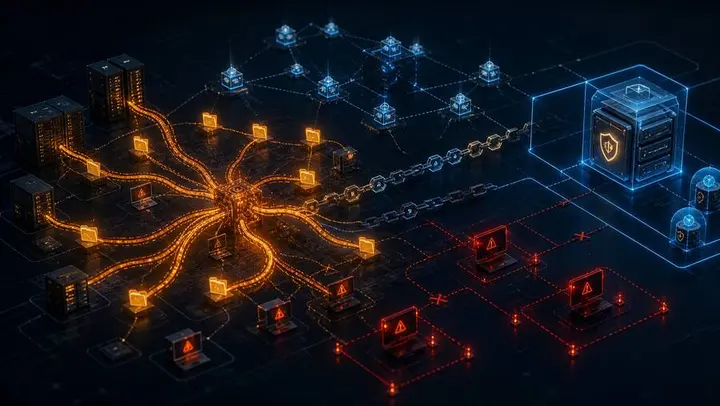
DeadLock Ransomware Shows Why Recovery Infrastructure Is Part of the Attack Surface
Microsoft’s DeadLock ransomware analysis shows why SMBs and government contractors need to protect backups, logs, identity, and recovery workflows before encryption starts.
BINDCLOAK Shows Why C2 Detection Needs Message-Level Visibility
Zscaler ThreatLabz detailed BINDCLOAK, a modular backdoor used after TELESHIM and MIXEDKEY in targeted government intrusions. The defensive lesson: endpoint visibility, token-use monitoring, DLL side-loading detection, and outbound C2 inspection all need to work together.
DPRK npm Compromises Show Why Dependency Trust Is Now Identity Risk
Amazon linked compromises of popular npm packages to a DPRK-linked actor. The defensive lesson for SMBs and government contractors: dependency risk is no longer just code review — it is maintainer identity, build-pipeline behavior, and runtime trust.
HOLLOWGRAPH Shows Why Microsoft 365 Is Now Part of the C2 Battlefield
Group-IB’s HOLLOWGRAPH research shows how attackers can turn Microsoft 365 calendars, Graph API traffic, and DNS into covert command-and-control. Here is what SMBs and government contractors should hunt for now.
Fuyao Android TV Botnet Shows Why Cheap Streaming Sticks Are Business Network Risk
KrebsOnSecurity and Bitsight report that some low-cost Android TV boxes are being used for both residential proxy traffic and AI-assisted ad fraud. For SMBs and government contractors, the lesson is simple: consumer IoT does not belong on trusted business networks.