


Showing 73–96 of 173 reports
UAT-7810 Shows Edge Devices Are Becoming China-Nexus Relay Infrastructure
Cisco Talos reports UAT-7810 is expanding ORB relay infrastructure using compromised edge and embedded devices. Here is what SMBs and government contractors should do now.
FortiBleed Shows Firewall Credentials Are Ransomware Fuel
SOCRadar linked the FortiBleed FortiGate credential-harvesting campaign to INC and Lynx ransomware operations. Here is what SMBs and government contractors should do next.
NetNut and Popa Takedown Shows Residential Proxies Are Now Attack Infrastructure
The FBI and industry partners disrupted NetNut and the Popa botnet. Here is why residential proxy abuse matters for SMBs, government contractors, and defenders.
Vect and TeamPCP Show Supply-Chain Credentials Are Ransomware Fuel
Sophos CTU reports that Vect and TeamPCP have linked ransomware deployment with supply-chain credential theft. Here is what SMBs and government contractors should harden now.
Ousaban Shows Banking Trojans Are Learning to Hide From Sandboxes
Ousaban’s Spain and Portugal campaign shows how banking trojans use geofencing, phishing PDFs, steganography, and daily-changing C2 to evade sandbox-heavy defenses.
SimpleHelp Exploitation Shows RMM Is a Credential Control Plane
Active exploitation of SimpleHelp CVE-2026-48558 shows why RMM platforms must be treated as privileged credential control planes, not routine support tools.
Bing SEO Poisoning Shows IT Admin Downloads Are Ransomware Initial Access
A DFIR Report case study shows how a fake ManageEngine OpManager download led from BumbleBee and AdaptixC2 to Akira ransomware. The defensive lesson: admin software downloads need control, verification, and monitoring.
Shai Hulud Shows CI/CD Identity Is Production Cloud Identity
Fortinet’s Shai Hulud case study shows how poisoned CI/CD dependencies can become cloud identity compromise, IAM escalation, and Redshift data theft. Here is what SMBs and government contractors should harden now.
Hospitality Photo-ZIP Campaign Shows Front Desk Workflows Are Initial Access Paths
Microsoft’s hospitality photo-ZIP campaign shows why front desk, booking, and customer intake workflows need executable-content controls, redirect-chain inspection, and endpoint hunting for unusual Node.js persistence.
StrikeShark Shows Loader Malware Is an Edge-Exposure Problem
Kaspersky’s StrikeShark research shows how opportunistic exploitation of exposed servers can become a multi-stage SharkLoader and Cobalt Strike intrusion. Here is what SMBs and government contractors should review now.
MuddyWater’s Chaos Masquerade Shows Ransomware Response Needs Attribution Discipline
Iran-linked MuddyWater activity shows why ransomware response needs to examine identity compromise, remote access, and adversary objectives instead of trusting the ransom note at face value.
SocGholish Takedown Shows Website Trust Is Malware Infrastructure
Operation Endgame disrupted SocGholish infrastructure, but the defensive lesson is bigger: compromised trusted websites are malware delivery infrastructure.
Mastra npm Compromise Shows AI Frameworks Are Supply-Chain Targets
Microsoft linked the Mastra AI npm package compromise to North Korean actor Sapphire Sleet. Here is what SMBs and government contractors should do about AI framework supply-chain risk.
Showboat Malware Shows Telecom Linux Servers Need Rootkit-Level Monitoring
Showboat is a China-linked Linux post-exploitation framework aimed at telecom providers. The lesson for defenders: treat Linux server persistence, dynamic linker abuse, and low-noise C2 as first-class monitoring priorities.
SmartApeSG Okendo Compromise Shows Third-Party Widgets Are Supply-Chain Risk
Zscaler ThreatLabz reported that SmartApeSG injected malicious JavaScript into the Okendo Reviews widget, creating downstream exposure across e-commerce sites. Here is what SMBs and government contractors should do about third-party browser code risk.
Tor-Based Crypto Clipper Shows Clipboard Theft Is Now Backdoor Activity
Microsoft research on a Tor-routed crypto clipper shows why defenders should connect USB shortcut execution, script interpreters, localhost proxy activity, and clipboard theft into one investigation path.
Shai-Hulud Shows AI Package Scanners Need Prompt-Injection Boundaries
Zscaler ThreatLabz says the Shai-Hulud campaign has expanded across package ecosystems and introduced prompt-injection tactics aimed at automated AI security triage. The defense lesson is simple: treat package content as hostile input, even when an LLM is doing the review.
IMA Diligence Breach Shows Legacy Servers Are Still Third-Party Risk
A reported IMA Diligence breach affecting more than 525,000 people shows why legacy third-party servers need ownership, monitoring, decommissioning, and data-risk review.
C0XMO Shows IoT Botnets Are Still an Edge Exposure Problem
Fortinet researchers detailed C0XMO, a Gafgyt variant spreading through DD-WRT and other exposed devices. Here is what SMBs and government contractors should lock down before compromised routers become DDoS infrastructure.
TA4922’s Global Expansion Shows HR and Tax Lures Are Initial Access Infrastructure
Proofpoint’s TA4922 reporting shows how localized HR, payroll, tax, and invoice lures can become full initial-access infrastructure through DLL sideloading, loaders, RATs, RMM tools, and browser credential theft.
Red Hat’s Miasma npm Compromise Shows Trusted Publishing Is Not a Control Boundary
A Red Hat Cloud Services npm compromise shows why signed releases and trusted publishing must be paired with install-time controls, CI/CD isolation, and fast credential rotation.
AI-Assisted Ransomware Tooling Shows EDR Evasion Is Now an Iteration Problem
Sophos observed ransomware-linked operators using AI-assisted development workflows to accelerate EDR evasion testing and Active Directory discovery. The defensive lesson: validate controls, harden identity, and monitor behavior before attackers iterate around your tooling.
FlutterBridge Shows Why macOS Malvertising Is Backdoor Delivery, Not Just Adware
Unit 42’s FlutterBridge research shows macOS malvertising evolving from adware into FlutterShell backdoor delivery. Here is what SMBs and government contractors should tighten first.
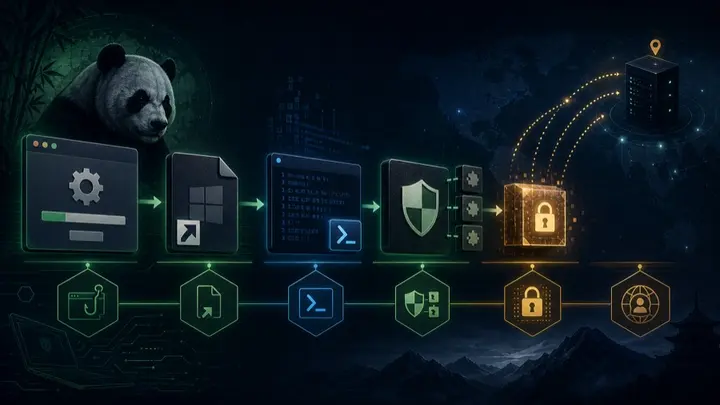
Mustang Panda’s Fake Browser Updater Shows Why LNK Files Still Matter
Mustang Panda’s fake browser updater chain shows why defenders still need to hunt LNK-to-PowerShell execution, DLL sideloading, user-context persistence, and suspicious HTTPS beaconing.