


Showing 265–288 of 379 reports
MediaInfoLib Parser Bugs Show File Metadata Is an Execution Boundary
Cisco Talos disclosed four patched MediaInfoLib heap-based buffer overflow vulnerabilities. The bigger lesson: automated media metadata parsing belongs inside a sandboxed, monitored execution boundary.
Poisoned Search and AI Recommendations Turn Utility Downloads Into RMM Access
Microsoft reported a cryptojacking campaign that uses poisoned search results, AI-surfaced software recommendations, fake utility downloads, and abused ScreenConnect access. Here is what SMBs and government contractors should defend first.
LiteSpeed cPanel KEV Shows Shared Hosting Is Privilege Escalation Terrain
CISA added CVE-2026-48172 to KEV after active exploitation of a LiteSpeed cPanel user-end plugin flaw that can let compromised hosting accounts execute scripts as root.
Megalodon GitHub Actions Backdoor Shows CI/CD Is Now a Credential Battlefield
The Megalodon GitHub campaign shows why CI/CD pipelines must be treated like production infrastructure: malicious workflow commits can harvest cloud credentials, OIDC tokens, SSH keys, and package secrets at scale.
Chinese-Language PhaaS Shows MFA Bypass Is Becoming Real-Time Fraud
Google’s reporting on Chinese-language phishing-as-a-service shows why MFA bypass, real-time OTP interception, and digital wallet fraud require phishing-resistant authentication and session monitoring.
KnowledgeDeliver RCE Shows Shared Machine Keys Are Shared Blast Radius
Mandiant’s KnowledgeDeliver CVE-2026-5426 report shows how shared ASP.NET machine keys can turn ViewState into unauthenticated RCE and user-facing malware delivery.
Laravel-Lang Compromise Shows Dependency Tags Can Be Weaponized
A Laravel-Lang package compromise shows why trusted dependency tags, Composer autoload behavior, and runtime secrets need security monitoring—not just engineering review.
Cl0p’s South Staffs Water Case Shows SOC Coverage Must Be Proven
The South Staffordshire Water breach shows why outsourced SOC coverage, legacy server risk, and vulnerability management must be proven—not assumed—for SMBs, utilities, and government contractors.
ROADtools Abuse Shows Cloud Identity Is the New Attack Surface
Unit 42’s ROADtools research shows why Microsoft Entra ID token abuse, rogue device registration, and Graph API enumeration need to be treated as core incident-response signals for SMBs and government contractors.
Drupal CVE-2026-9082 Shows Web Asset Inventory Is Emergency Response
Drupal CVE-2026-9082 is already being scanned and exploited in the wild. The lesson for SMBs and government contractors: know where your Drupal sites are, verify PostgreSQL exposure, patch fast, and review logs before probing turns into compromise.
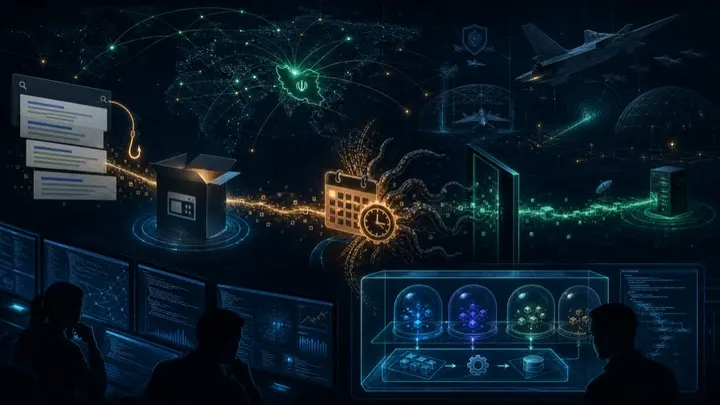
Nimbus Manticore Shows Iranian APTs Are Moving Faster With AI-Assisted Tooling
Check Point Research reports that IRGC-affiliated Nimbus Manticore resurfaced with fake Zoom and SQL Developer lures, SEO poisoning, AppDomain hijacking, and a new MiniFast backdoor. Here is what SMBs and government contractors should tighten first.
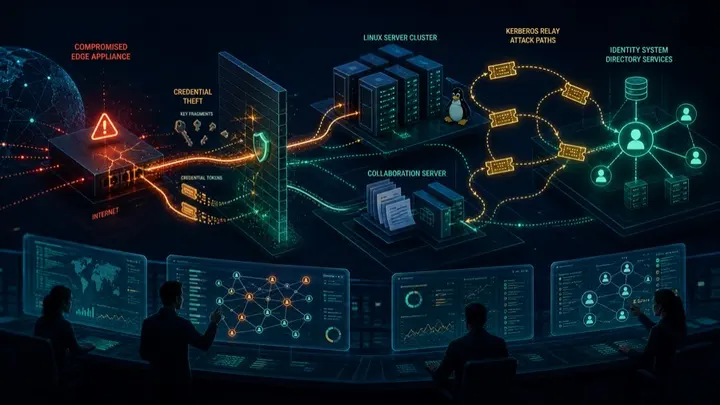
F5-to-Confluence Intrusion Shows Edge Devices Are Identity Attack Paths
Microsoft analyzed an intrusion where an F5 BIG-IP edge appliance led to Linux access, Confluence compromise, credential theft, and identity relay attempts. Here is what SMBs and government contractors should tighten first.
Screening Serpens Shows Recruiting Is Now an Espionage Attack Surface
Iran-nexus Screening Serpens used recruitment and meeting lures, new RAT variants, and .NET AppDomainManager hijacking. Here is what SMBs and government contractors should tighten now.
Kimwolf Arrest Shows DDoS Risk Starts on Forgotten IoT
The alleged Kimwolf botmaster arrest is a useful reminder for SMBs and government contractors: DDoS resilience starts with asset visibility, upstream protection, and hardening forgotten IoT and edge devices.
TamperedChef Shows Signed Productivity Apps Cannot Be Trusted by Default
TamperedChef-style malware hides inside convincing signed productivity apps. Here is what SMBs and government contractors should do about it.
Patriot Bait Shows AI-Enabled Fraud Can Turn Trust Into Attack Surface
Trend Micro’s Patriot Bait research shows how one operator used AI assistance, social trust, WordPress credential attacks, and crypto fraud infrastructure to scale a low-cost cybercrime operation.
Mini Shai-Hulud Shows CI/CD Secrets Are the Real npm Supply-Chain Prize
Mini Shai-Hulud’s @antv npm compromise shows why dependency malware should be treated as a CI/CD credential-theft threat, not just a package hygiene problem.
ExifTool CVE-2026-3102 Shows Image Metadata Belongs in the Threat Model
CVE-2026-3102 in ExifTool shows why image metadata processing should be patched, isolated, and monitored like any other untrusted file-ingest path.
P2Pinfect Shows Exposed Redis in Kubernetes Can Become Dormant Botnet Infrastructure
Fortinet observed P2Pinfect infections inside GKE clusters where exposed Redis instances became long-lived botnet footholds. For SMBs and government contractors, the lesson is clear: cloud misconfiguration, runtime visibility, and egress monitoring matter as much as patching.
Verizon DBIR 2026 Shows Vulnerability Exploitation Is Now the Breach Priority
Verizon’s 2026 DBIR shows vulnerability exploitation overtaking credential abuse as the top breach access vector. Here is what SMBs and government contractors should fix first.
Fox Tempest Shows Code Signing Trust Can Be Weaponized
Microsoft disrupted Fox Tempest, a malware-signing-as-a-service operation that helped ransomware crews make malicious binaries look trusted. Here is what SMBs and government contractors should review now.
CISA GovCloud Leak Shows Secret Scanning Cannot Be Optional
A reported CISA contractor GitHub leak shows why secret scanning, token rotation, and CI/CD hardening need to be enforced controls, not optional developer hygiene.
Storm-2949 Shows Cloud Breaches Start With Identity, Not Malware
Microsoft’s Storm-2949 case study is a clean warning for SMBs and government contractors: once cloud identity and control-plane access are compromised, attackers can steal data without deploying traditional malware.
AI Agent Governance Is Becoming a Security Control, Not a Nice-to-Have
AI agents now operate with real credentials inside business systems. Here is how SMBs and government contractors should govern identity, authority, action, and evidence before agentic workflows become unmanaged risk.