


Showing 289–312 of 379 reports
SGLang RCE Flaws Show AI Inference Servers Need Real Network Isolation
CERT/CC disclosed three SGLang vulnerabilities affecting AI inference deployments, including remote code execution and path traversal risks. Here is what SMBs and government contractors should do now.
Grafana GitHub Token Breach Shows Why Source Code Access Needs Guardrails
Grafana disclosed unauthorized GitHub access tied to a leaked token and codebase download. Here is what SMBs and government contractors should tighten around source-code access, CI/CD tokens, and extortion readiness.
node-ipc Backdoor Shows Why CI Secrets Need Supply Chain Controls
Malicious node-ipc npm releases turned a package update into a credential-exposure event. Here is what SMBs and government contractors should check first.
Exchange OWA Zero-Day Shows Why Email Servers Need Emergency Mitigation
CISA added Microsoft Exchange Server CVE-2026-42897 to KEV after evidence of active exploitation. For SMBs and government contractors, the lesson is simple: internet-facing email infrastructure needs emergency mitigation playbooks before the patch lands.
Device Code Phishing Turns Legitimate Login Flows Into Token Theft
Device code phishing is scaling because it abuses legitimate OAuth flows instead of simply stealing passwords. Here is what SMBs and government contractors should review now.
Recent Linux Kernel Exploits Make Attack Surface Reduction a Practical Priority
Recent Linux kernel exploit discussions show why SMBs and government contractors should reduce unused modules and services, not just wait for patches.
PawsRunner Steganography Shows Infostealers Are Hiding in Plain Sight
FortiGuard Labs reports PureLogs is being delivered through PawsRunner steganography. Here is what SMBs and government contractors should watch for defensively.
BlackFile Vishing Campaign Shows Why MFA Alone Is Not Enough
GTIG reports UNC6671 / BlackFile is using vishing, AiTM phishing, and SaaS data theft to extort organizations. Here is what SMBs and government contractors should harden now.
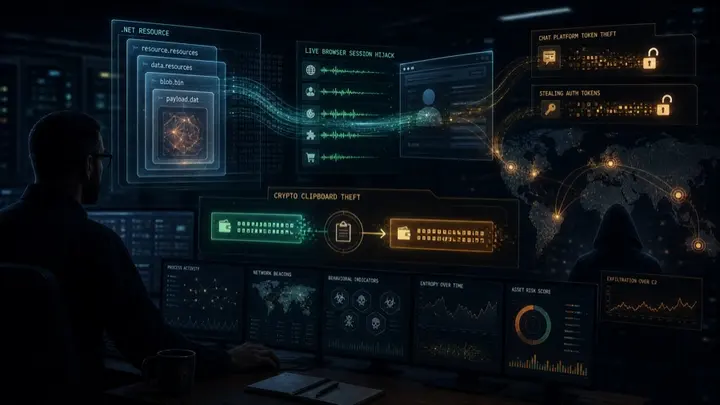
Gremlin Stealer Shows Why Browser Sessions Are Now High-Value Targets
Unit 42 reports Gremlin Stealer has evolved with resource-file obfuscation, session hijacking, Discord token theft, and crypto clipboard fraud. Here is what SMBs and government contractors should do defensively.
Cisco SD-WAN Exploitation Shows Edge Controllers Need Emergency Review
Cisco Talos reports active exploitation of Catalyst SD-WAN authentication bypass and related vulnerabilities. Here is what SMBs and government contractors should prioritize now.
Kazuar Shows Russian Espionage Malware Is Engineering for Resilience
Microsoft reports that Kazuar, attributed to Russian state actor Secret Blizzard, has evolved into a modular P2P botnet. Here is what SMBs and government contractors should take from it defensively.
Exposed AI Apps Turn Misconfiguration Into RCE Risk
Microsoft warns that publicly exposed AI apps, MCP servers, and Kubernetes-hosted agent tooling can turn weak defaults into practical paths for RCE, credential theft, and data exposure.
May 2026 Patch Tuesday: How SMBs Should Prioritize 132 Microsoft CVEs
Microsoft’s May 2026 Patch Tuesday shipped 132 CVEs. Here is how SMBs and government contractors should prioritize identity, server, and Office risks first.
The Gentlemen RaaS Leak Shows Ransomware Is Still an Edge-Device Problem
Check Point’s look inside The Gentlemen ransomware operation is a useful reminder for SMBs and government contractors: exposed edge appliances, weak identity controls, and unmanaged remote access paths still drive real ransomware risk.
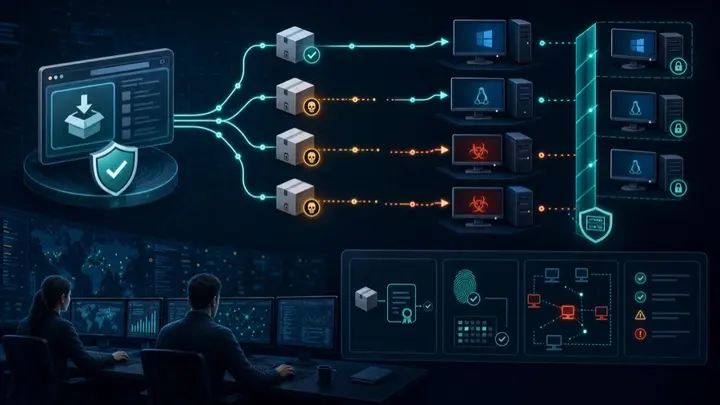
JDownloader Site Compromise Shows Why Trusted Downloads Still Need Verification
Attackers swapped selected JDownloader website download links with malicious installers. Here is what SMB and government-contractor defenders should do about trusted-download risk.
Fake OpenAI Hugging Face Repo Shows AI Supply Chain Risk Is Already Here
A fake OpenAI Privacy Filter repository on Hugging Face delivered Windows infostealer malware. Here is what SMB and gov-contractor defenders should take from it.
MCP Server Command Injection Shows Why AI Tools Need Real Isolation
A critical GitHub advisory for @profullstack/mcp-server shows how unsafe AI tool endpoints can turn domain lookup functionality into unauthenticated remote code execution.
Dirty Frag Turns Linux Footholds Into Root: What Defenders Should Do Now
Microsoft is tracking active Dirty Frag Linux privilege escalation activity. Here is what SMB and gov-contractor defenders should prioritize now.
Prompt Injection Just Became an RCE Problem for AI Agents
Microsoft disclosed Semantic Kernel vulnerabilities showing how prompt injection can cross into code execution when AI agents are connected to unsafe tools. Here is what defenders should review now.
PAN-OS Captive Portal Zero-Day Shows Why Internet-Facing Edge Devices Need Immediate Review
Unit 42 reports limited exploitation of CVE-2026-0300, a PAN-OS Captive Portal zero-day. Here is what SMB and government-contractor defenders should check now.
PCPJack Shows Cloud Malware Is Moving From Cryptomining to Credential Theft
SentinelLabs reported PCPJack, a cloud-focused worm that evicts TeamPCP artifacts, steals credentials from exposed infrastructure, and spreads across cloud systems.
Critical Cisco IMC Authentication Bypass Grants Remote Attackers Admin Privileges
Cisco has released emergency security updates to patch a critical authentication bypass vulnerability in its Integrated Management Controller (IMC), a critical component embedded on the motherboard of Cisco UCS C-Series and E-Series servers that provides out-of-band management ca
UAT-10608: NEXUS Listener Framework Compromises 766 Next.js Hosts in 24-Hour Credential Harvesting Blitz
Cisco Talos has disclosed a large-scale automated credential harvesting campaign carried out by a threat cluster they are tracking as “UAT-10608.” The systematic exploitation campaign leverages a custom framework called “NEXUS Listener” to target Next.js applications vulnerable t
ShinyHunters Breaches European Commission: 350GB of Sensitive Data Exfiltrated from AWS Cloud
The European Commission has confirmed a significant data breach after its Europa.eu web platform was compromised in a cyberattack claimed by the notorious ShinyHunters extortion gang. The attackers allegedly exfiltrated over 350GB of sensitive data from the Commission’s Amazon We