Showing 145–168 of 173 reports
Facebook Malvertising Campaign Uses Fake Windows 11 Pages to Deploy Credential-Stealing Malware
Attackers are running a sophisticated malvertising campaign that leverages paid Facebook ads to distribute credential-stealing malware disguised as official Windows 11 updates. The campaign uses convincing fake Microsoft download pages and includes multiple technical countermeasu
Kimwolf Botnet Swamps I2P Anonymity Network in Massive Sybil Attack
The massive Kimwolf IoT botnet has caused significant disruptions to The Invisible Internet Project (I2P), a decentralized privacy network, after botnet operators accidentally overwhelmed the system while attempting to use it for command-and-control evasion. The Attack According
Russian Threat Actor Deploys CANFAIL Malware Against Ukrainian Organizations
Google Threat Intelligence Group (GTIG) has uncovered a new threat actor possibly affiliated with Russian intelligence services that has been systematically targeting Ukrainian organizations with a sophisticated malware strain known as CANFAIL. Target Profile The threat group has
ClawHavoc Supply Chain Attack Poisons OpenClaw ClawHub With 1,184 Malicious AI Agent Skills
A massive supply chain attack dubbed ClawHavoc has compromised ClawHub, the official skill marketplace for OpenClaw, an open-source AI agent platform formerly known as ClawdBot and Moltbot. Researchers have uncovered at least 1,184 malicious “Skills”—plugin-style packages that ex
NexShield Fake Ad Blocker Uses CrashFix Attack to Deliver ModeloRAT Malware
Security researchers at Huntress have uncovered a sophisticated new malware campaign that weaponizes browser stability against users. The attack, dubbed CrashFix, represents an evolution of the notorious ClickFix social engineering technique—but with a dangerous twist: instead of
OysterLoader: Sophisticated Multi-Stage Malware Loader Linked to Rhysida Ransomware Campaigns
A highly sophisticated malware loader known as OysterLoader has emerged as a significant cybersecurity threat, employing advanced multi-layer obfuscation techniques to evade detection while delivering dangerous payloads including Rhysida ransomware and the widespread Vidar infost
AiFrame Campaign: 30 Fake AI Chrome Extensions with 300K Users Steal Credentials, Gmail Content
Researchers at browser security platform LayerX have uncovered a coordinated malware campaign dubbed “AiFrame” involving 30 malicious Chrome extensions installed by more than 300,000 users. The extensions masquerade as AI assistants while secretly stealing credentials, email cont
Phorpiex Botnet Resurfaces: Phishing Campaign Delivers Offline-Capable Global Group Ransomware
A new phishing campaign leveraging the infamous Phorpiex botnet has been observed distributing Global Group ransomware through weaponized Windows shortcut (.LNK) files, according to a new advisory from Forcepoint X-Labs. The Attack Chain The campaign uses phishing emails with the
Cybercriminals Weaponize ChatGPT and Grok to Distribute AMOS Stealer on macOS
A sophisticated attack campaign is exploiting user trust in artificial intelligence platforms to distribute the Atomic macOS Stealer (AMOS), representing a dangerous evolution in social engineering tactics that combines legitimate AI chatbot services with paid Google advertising.
XWorm RAT Campaign Exploits CVE-2018-0802 in Multi-Language Phishing Attacks Using Fileless Injection
FortiGuard Labs has uncovered a sophisticated phishing campaign delivering XWorm version 7.2, a multi-functional Remote Access Trojan (RAT) that provides attackers with full remote control of compromised Windows systems. Campaign Overview The campaign utilizes multiple phishing e
Fake 7-Zip Downloads Convert Home PCs Into Residential Proxy Nodes for Cybercriminals
A sophisticated brand impersonation campaign is weaponizing the popular 7-Zip file archiver to silently transform infected Windows computers into residential proxy nodes—monetizing victims’ IP addresses for fraud, scraping, and anonymity laundering operations. The Lookalike Domai
Silver Fox APT Unleashes ValleyRAT with Rare PoolParty Process Injection Technique
A sophisticated malware campaign targeting Chinese-speaking users has revealed a significant evolution in the Silver Fox APT group’s capabilities. According to new research from Cybereason Security Services, the threat actors are deploying fake software installers to deliver Vall
SystemBC Botnet Survives Law Enforcement Takedown, Infects Over 10,000 Devices Worldwide
The SystemBC malware loader has demonstrated remarkable resilience, continuing to operate despite targeted efforts during Europol’s Operation Endgame in May 2024. Cybersecurity firm Silent Push has identified more than 10,000 unique infected IP addresses across a massive botnet i
PDFSider: The Stealthy Backdoor Targeting Fortune 100 Financial Institutions
A newly identified Windows malware strain called PDFSider has emerged as a dangerous tool in the arsenals of multiple ransomware operators, with at least one confirmed attack targeting a Fortune 100 finance company. Security researchers at Resecurity uncovered the malware during
ShadowHS: Fileless Linux Post-Exploitation Framework Runs Entirely in Memory
Cyble Research & Intelligence Labs (CRIL) has uncovered a sophisticated Linux intrusion framework dubbed ShadowHS — a stealthy, fileless post-exploitation tool that executes entirely from memory, leaving virtually no traces on disk. This discovery highlights the growing sophistic
Android Malware Campaign Abuses Hugging Face AI Platform to Distribute RAT
Threat actors are abusing the Hugging Face AI platform to host Android malware, using server-side polymorphism to generate thousands of RAT variants every 15 minutes.
Fake Clawdbot VS Code Extension Deploys ScreenConnect RAT
A malicious VS Code extension impersonating the popular Clawdbot AI assistant has been caught deploying ScreenConnect RAT on Windows machines. The trojanized extension worked as a functional AI coding tool while silently installing remote access software.
Poland Thwarts Russian Wiper Malware Attack on Power Plants
Source: Hackread | Author: Deeba Ahmed Poland has narrowly avoided a massive energy crisis following what officials are calling the largest cyberattack on the country in years. Between 29 and 30 December 2025, hackers attempted to break into the nation’s energy infrastructure, sp
New Go loader pushes Rhadamanthys stealer
READ ARTICLE Posted: March 22, 2024 by Jérôme Segura Malware loaders (also known as droppers or downloaders) are a popular commodity in the criminal underground. Their primary function is to successfully compromise a machine and deploy one or multiple additional payloads. A good
DreamBus Unleashes Metabase Mayhem With New Exploit Module
Read Article Key Takeaways
Hundreds of Thousands of Dollars Worth of Solana Cryptocurrency Assets Stolen in Recent CLINKSINK Drainer Campaigns
Read Article On January 3, 2024, Mandiant’s X social media account was taken over and subsequently used to distribute links to a cryptocurrency drainer phishing page. Working with X, we were able to regain control of the account and, based on our investigation over the following
Custom GPTs: A Case of Malware Analysis and IoC Analyzing
Read Article On November 6, 2023, CustomGPTs, a new feature that OpenAI stated on its blog, became available. We can already say that the emergence of Custom Generative Pre-trained Transformers (GPTs) could mark a significant shift in the dynamics of both digital defense and offe
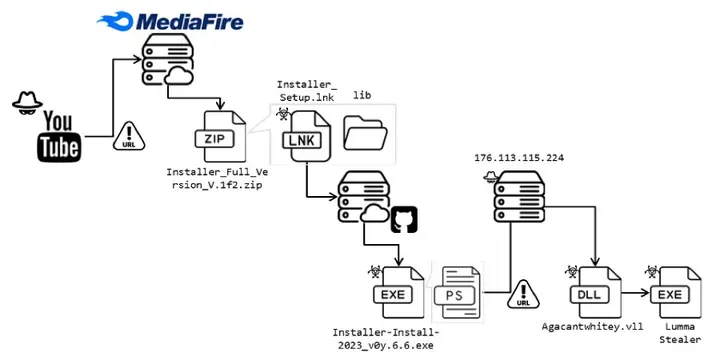
Deceptive Cracked Software Spreads Lumma Variant on YouTube
Read Article Initial Infection Vector The hacker initially breaches a YouTuber’s account and uploads videos masquerading as sharing cracked software. Figure 3 shows the video descriptions in which a malicious URL is embedded, enticing users to download a ZIP file that harbors mal