


Showing 73–92 of 92 reports
Chinese-Language PhaaS Shows MFA Bypass Is Becoming Real-Time Fraud
Google’s reporting on Chinese-language phishing-as-a-service shows why MFA bypass, real-time OTP interception, and digital wallet fraud require phishing-resistant authentication and session monitoring.
KnowledgeDeliver RCE Shows Shared Machine Keys Are Shared Blast Radius
Mandiant’s KnowledgeDeliver CVE-2026-5426 report shows how shared ASP.NET machine keys can turn ViewState into unauthenticated RCE and user-facing malware delivery.
Laravel-Lang Compromise Shows Dependency Tags Can Be Weaponized
A Laravel-Lang package compromise shows why trusted dependency tags, Composer autoload behavior, and runtime secrets need security monitoring—not just engineering review.
Cl0p’s South Staffs Water Case Shows SOC Coverage Must Be Proven
The South Staffordshire Water breach shows why outsourced SOC coverage, legacy server risk, and vulnerability management must be proven—not assumed—for SMBs, utilities, and government contractors.
ROADtools Abuse Shows Cloud Identity Is the New Attack Surface
Unit 42’s ROADtools research shows why Microsoft Entra ID token abuse, rogue device registration, and Graph API enumeration need to be treated as core incident-response signals for SMBs and government contractors.
Drupal CVE-2026-9082 Shows Web Asset Inventory Is Emergency Response
Drupal CVE-2026-9082 is already being scanned and exploited in the wild. The lesson for SMBs and government contractors: know where your Drupal sites are, verify PostgreSQL exposure, patch fast, and review logs before probing turns into compromise.
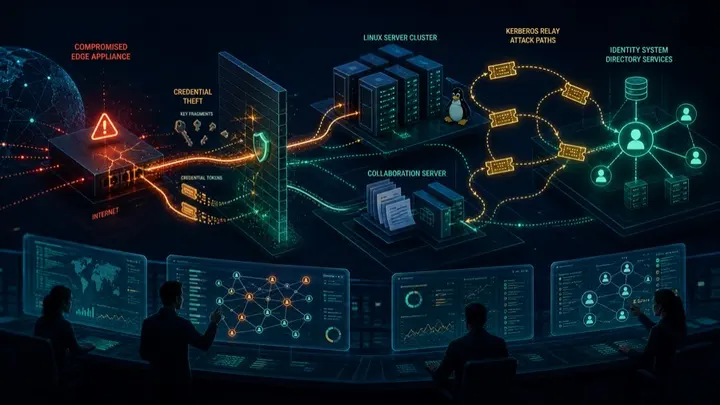
F5-to-Confluence Intrusion Shows Edge Devices Are Identity Attack Paths
Microsoft analyzed an intrusion where an F5 BIG-IP edge appliance led to Linux access, Confluence compromise, credential theft, and identity relay attempts. Here is what SMBs and government contractors should tighten first.
Screening Serpens Shows Recruiting Is Now an Espionage Attack Surface
Iran-nexus Screening Serpens used recruitment and meeting lures, new RAT variants, and .NET AppDomainManager hijacking. Here is what SMBs and government contractors should tighten now.
TamperedChef Shows Signed Productivity Apps Cannot Be Trusted by Default
TamperedChef-style malware hides inside convincing signed productivity apps. Here is what SMBs and government contractors should do about it.
Patriot Bait Shows AI-Enabled Fraud Can Turn Trust Into Attack Surface
Trend Micro’s Patriot Bait research shows how one operator used AI assistance, social trust, WordPress credential attacks, and crypto fraud infrastructure to scale a low-cost cybercrime operation.
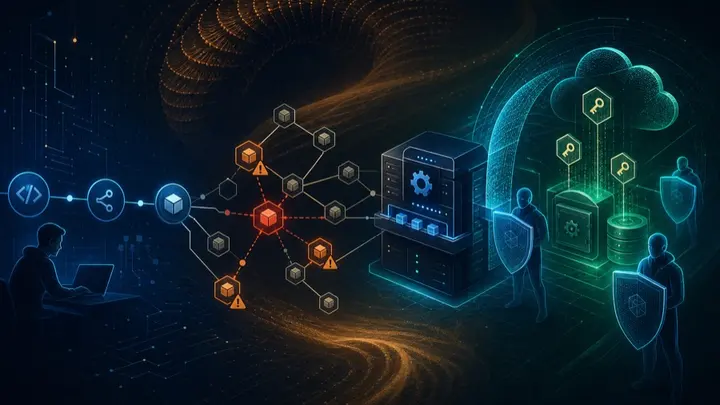
Mini Shai-Hulud Shows CI/CD Secrets Are the Real npm Supply-Chain Prize
Mini Shai-Hulud’s @antv npm compromise shows why dependency malware should be treated as a CI/CD credential-theft threat, not just a package hygiene problem.
ExifTool CVE-2026-3102 Shows Image Metadata Belongs in the Threat Model
CVE-2026-3102 in ExifTool shows why image metadata processing should be patched, isolated, and monitored like any other untrusted file-ingest path.
Fox Tempest Shows Code Signing Trust Can Be Weaponized
Microsoft disrupted Fox Tempest, a malware-signing-as-a-service operation that helped ransomware crews make malicious binaries look trusted. Here is what SMBs and government contractors should review now.
CISA GovCloud Leak Shows Secret Scanning Cannot Be Optional
A reported CISA contractor GitHub leak shows why secret scanning, token rotation, and CI/CD hardening need to be enforced controls, not optional developer hygiene.
Storm-2949 Shows Cloud Breaches Start With Identity, Not Malware
Microsoft’s Storm-2949 case study is a clean warning for SMBs and government contractors: once cloud identity and control-plane access are compromised, attackers can steal data without deploying traditional malware.
AI Agent Governance Is Becoming a Security Control, Not a Nice-to-Have
AI agents now operate with real credentials inside business systems. Here is how SMBs and government contractors should govern identity, authority, action, and evidence before agentic workflows become unmanaged risk.
Grafana GitHub Token Breach Shows Why Source Code Access Needs Guardrails
Grafana disclosed unauthorized GitHub access tied to a leaked token and codebase download. Here is what SMBs and government contractors should tighten around source-code access, CI/CD tokens, and extortion readiness.
Exchange OWA Zero-Day Shows Why Email Servers Need Emergency Mitigation
CISA added Microsoft Exchange Server CVE-2026-42897 to KEV after evidence of active exploitation. For SMBs and government contractors, the lesson is simple: internet-facing email infrastructure needs emergency mitigation playbooks before the patch lands.
Device Code Phishing Turns Legitimate Login Flows Into Token Theft
Device code phishing is scaling because it abuses legitimate OAuth flows instead of simply stealing passwords. Here is what SMBs and government contractors should review now.
BlackFile Vishing Campaign Shows Why MFA Alone Is Not Enough
GTIG reports UNC6671 / BlackFile is using vishing, AiTM phishing, and SaaS data theft to extort organizations. Here is what SMBs and government contractors should harden now.