


Intel Feed
Cyber Threat IntelligencePage 20
Reports
Reporting archive — page 20
Showing 457–480 of 584 reports
Google Blocks Massive Model Extraction Campaign Targeting Gemini AI with 100,000+ Malicious Prompts
Google has revealed it detected and blocked a sophisticated campaign involving more than 100,000 prompts designed to extract the proprietary reasoning capabilities of its Gemini AI model, according to the Google Threat Intelligence Group’s latest quarterly threat report. The Grow
Metro4Shell: Critical React Native CLI Vulnerability Actively Exploited to Deploy Malware
Threat actors are actively exploiting a critical remote code execution vulnerability in the popular @react-native-community/cli npm package, impacting countless mobile application developers worldwide. The Vulnerability: CVE-2025-11953 Dubbed Metro4Shell, this critical vulnerabil
AiFrame Campaign: 30 Fake AI Chrome Extensions with 300K Users Steal Credentials, Gmail Content
Researchers at browser security platform LayerX have uncovered a coordinated malware campaign dubbed “AiFrame” involving 30 malicious Chrome extensions installed by more than 300,000 users. The extensions masquerade as AI assistants while secretly stealing credentials, email cont
Phorpiex Botnet Resurfaces: Phishing Campaign Delivers Offline-Capable Global Group Ransomware
A new phishing campaign leveraging the infamous Phorpiex botnet has been observed distributing Global Group ransomware through weaponized Windows shortcut (.LNK) files, according to a new advisory from Forcepoint X-Labs. The Attack Chain The campaign uses phishing emails with the
Cybercriminals Weaponize ChatGPT and Grok to Distribute AMOS Stealer on macOS
A sophisticated attack campaign is exploiting user trust in artificial intelligence platforms to distribute the Atomic macOS Stealer (AMOS), representing a dangerous evolution in social engineering tactics that combines legitimate AI chatbot services with paid Google advertising.
XWorm RAT Campaign Exploits CVE-2018-0802 in Multi-Language Phishing Attacks Using Fileless Injection
FortiGuard Labs has uncovered a sophisticated phishing campaign delivering XWorm version 7.2, a multi-functional Remote Access Trojan (RAT) that provides attackers with full remote control of compromised Windows systems. Campaign Overview The campaign utilizes multiple phishing e
Google Warns of Sustained Russia and China Cyberattacks Targeting Defense Industrial Base
Google Threat Intelligence Group (GTIG) has published a comprehensive report revealing persistent cyber operations targeting the defense industrial base (DIB) from Russia and China-linked threat actors. The findings detail how state-sponsored hackers are exploiting everything fro
WormGPT Database Breach Exposes 19,000 Cybercriminal Users and Billing Data
A threat actor has leaked the complete WormGPT database, exposing over 19,000 users of the notorious cybercrime AI platform along with their email addresses, billing data, and subscription information.
Chinese APT UNC3886 Breaches Singapore’s Four Largest Telcos in Coordinated Espionage Campaign
Singapore’s government has officially confirmed that a sophisticated Chinese cyber-espionage group breached all four of the nation’s largest telecommunications providers in a coordinated campaign that exploited zero-day vulnerabilities and deployed advanced persistence mechanisms
BlueNoroff’s GhostCall and GhostHire Campaigns Use Stolen Victim Videos to Compromise Crypto Executives
North Korean threat actor BlueNoroff (also known as Sapphire Sleet, APT38, Alluring Pisces, Stardust Chollima, and TA444) has launched two sophisticated campaigns—GhostCall and GhostHire—targeting cryptocurrency executives, blockchain developers, and venture capital professionals
APT28 Exploits CVE-2026-21509 in Operation Neusploit: Stealing Emails with MiniDoor Backdoor
Russia’s infamous APT28 (Fancy Bear/Forest Blizzard) threat group has weaponized a recently patched Microsoft Office vulnerability in just three days, launching a sophisticated espionage campaign dubbed Operation Neusploit targeting government and diplomatic entities across Centr
Fake 7-Zip Downloads Convert Home PCs Into Residential Proxy Nodes for Cybercriminals
A sophisticated brand impersonation campaign is weaponizing the popular 7-Zip file archiver to silently transform infected Windows computers into residential proxy nodes—monetizing victims’ IP addresses for fraud, scraping, and anonymity laundering operations. The Lookalike Domai
North Korean Hackers Deploy AI-Generated Deepfakes and Seven Malware Families in Targeted Cryptocurrency Attacks
North Korean threat actor UNC1069 has launched a sophisticated campaign targeting the cryptocurrency and decentralized finance (DeFi) sectors, deploying AI-generated deepfake videos and seven unique malware families to steal credentials and financial data, according to new resear
TGR-STA-1030 Espionage Campaign Compromises 70 Organizations Across 37 Nations Using ShadowGuard Linux Rootkit
A massive, state-aligned cyber espionage campaign has quietly infiltrated government networks across 37 countries, targeting ministries of finance, law enforcement, and critical infrastructure. In a new report, Unit 42 exposes the operations of TGR-STA-1030 (also tracked as UNC66
BridgePay Ransomware Attack Forces Nationwide Cash-Only Payment Disruption
A major ransomware attack on BridgePay Network Solutions has caused a nationwide payment processing outage, forcing merchants across the United States to switch to cash-only operations and disrupting card transactions for municipalities and businesses alike. Ransomware Confirmed
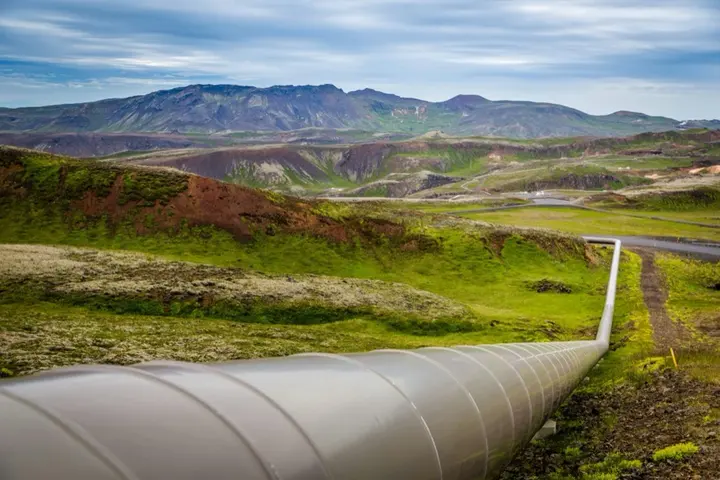
Qilin Ransomware Hits Romania’s National Oil Pipeline Operator Conpet, Claims Nearly 1 TB Data Theft
Romania’s national oil pipeline operator Conpet has confirmed a cyberattack disrupted parts of its technology infrastructure and knocked its website offline earlier this week. The company operates approximately 3,800 kilometers (2,360 miles) of pipelines supplying domestic and im
Flickr Data Breach Exposes User Information Through Third-Party Email Vendor Vulnerability
Photo and video sharing service Flickr has disclosed a data security incident where user personal information was potentially exposed through a vulnerability at a third-party email service provider. The San Francisco-based platform confirmed on February 5, 2026, that the breach m
SafePay Ransomware Attack on Conduent Exposes Data of 25.9 Million Americans
A January 2025 ransomware attack on government technology giant Conduent has exploded into one of the largest data breaches in recent history, with confirmed victims now numbering at least 25.9 million Americans across multiple states. The breach, attributed to the SafePay ransom
APT-Q-27 (GoldenEyeDog) Deploys Fileless Malware in Stealthy Corporate Network Attacks
A new investigation from CyStack’s security team reveals how the threat group APT-Q-27, also known as GoldenEyeDog, is bypassing modern security defenses through an elaborate multi-stage attack chain that operates almost entirely in memory. The Attack Chain: From Support Ticket t
Betterment Data Breach Exposes 1.4 Million Customers Following Sophisticated Social Engineering Attack
Automated investment platform Betterment has disclosed a significant data breach affecting approximately 1.4 million customers, following a sophisticated social engineering campaign that targeted company employees in January 2026. Attack Overview According to Betterment’s officia
Iranian APT Infy Resurfaces with New Tornado Malware After Internet Blackout
The elusive Iranian threat group known as Infy (also tracked as Prince of Persia) has evolved its tactics and deployed new command-and-control infrastructure, resuming operations precisely when Iran’s government-imposed internet blackout ended in late January 2026. Operational Ti
Ransomware Gangs Abuse ISPsystem VMmanager to Hide Malicious Infrastructure at Scale
Ransomware operators are increasingly exploiting legitimate virtual infrastructure management platforms to host and deliver malicious payloads at scale, effectively hiding their command-and-control infrastructure among thousands of innocuous systems. The Discovery Researchers at
Silver Fox APT Unleashes ValleyRAT with Rare PoolParty Process Injection Technique
A sophisticated malware campaign targeting Chinese-speaking users has revealed a significant evolution in the Silver Fox APT group’s capabilities. According to new research from Cybereason Security Services, the threat actors are deploying fake software installers to deliver Vall
SystemBC Botnet Survives Law Enforcement Takedown, Infects Over 10,000 Devices Worldwide
The SystemBC malware loader has demonstrated remarkable resilience, continuing to operate despite targeted efforts during Europol’s Operation Endgame in May 2024. Cybersecurity firm Silent Push has identified more than 10,000 unique infected IP addresses across a massive botnet i