


Intel Feed
Cyber Threat IntelligencePage 21
Reports
Reporting archive — page 21
Showing 481–504 of 584 reports
Strategic Intelligence and the Cognitive Threshold: A Multidimensional Analysis of AI Model Efficacy in 2026
A comprehensive analysis of frontier AI models for strategic intelligence work in 2026, comparing GPT-5.2, Claude Opus 4.5, Gemini 3 Pro, and Grok 4.1 across reasoning benchmarks, research capabilities, geopolitical analysis, and financial intelligence applications.
DKnife: Cisco Talos Exposes China-Nexus Gateway-Monitoring AitM Framework Active Since 2019
Cisco Talos researchers have disclosed a sophisticated adversary-in-the-middle (AitM) framework dubbed “DKnife” that enables China-nexus threat actors to intercept, manipulate, and weaponize network traffic at the gateway level. The framework has been operational since at least 2
CISA Confirms VMware ESXi Flaw CVE-2025-22225 Now Exploited in Active Ransomware Campaigns
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has updated its Known Exploited Vulnerabilities (KEV) catalog to confirm that CVE-2025-22225, a high-severity VMware ESXi sandbox escape vulnerability, is now being actively exploited in ransomware attacks. The Vuln
EnCase Forensic Driver Weaponized: BYOVD Attack Targets 59 EDR Tools Through SonicWall VPN Breach
Security researchers at Huntress have documented a sophisticated intrusion where threat actors leveraged compromised SonicWall SSLVPN credentials to deploy a custom EDR killer that abuses a legitimate forensic driver from Guidance Software’s EnCase to terminate security processes
PDFSider: The Stealthy Backdoor Targeting Fortune 100 Financial Institutions
A newly identified Windows malware strain called PDFSider has emerged as a dangerous tool in the arsenals of multiple ransomware operators, with at least one confirmed attack targeting a Fortune 100 finance company. Security researchers at Resecurity uncovered the malware during
ShinyHunters Claims Massive Ivy League Breach: 2.2 Million Records from Harvard and UPenn
The notorious threat actor group ShinyHunters has claimed responsibility for a significant data breach targeting two of America’s most prestigious academic institutions: Harvard University and the University of Pennsylvania. What’s Being Claimed On February 4, 2026, ShinyHunters
AI-Powered Attack Achieves AWS Admin Access in Under 10 Minutes: A New Era of Automated Intrusions
In a stark demonstration of how artificial intelligence is transforming the cybersecurity threat landscape, the Sysdig Threat Research Team (TRT) has documented a sophisticated cloud intrusion where attackers achieved full administrative control of an AWS environment in less than
ShadowHS: Fileless Linux Post-Exploitation Framework Runs Entirely in Memory
Cyble Research & Intelligence Labs (CRIL) has uncovered a sophisticated Linux intrusion framework dubbed ShadowHS — a stealthy, fileless post-exploitation tool that executes entirely from memory, leaving virtually no traces on disk. This discovery highlights the growing sophistic
Vibe Coding Gone Wrong: Moltbook AI Social Network Exposes 4.75 Million Records in Massive Database Breach
Google-owned Wiz discovers 4.75 million exposed records in AI social network Moltbook, including 1.5M API tokens and plaintext OpenAI keys—all because Row Level Security was never enabled on the “vibe-coded” platform.
Chinese APT Lotus Blossom Hijacks Notepad++ Update Mechanism to Deploy Chrysalis Backdoor
Chinese state-sponsored threat actors hijacked Notepad++ update infrastructure for nearly six months, deploying a sophisticated custom backdoor called Chrysalis to selectively targeted victims.
Russian Legion Hacker Alliance Launches OpDenmark Campaign Against Danish Critical Infrastructure
A newly formed Russian hacktivist alliance called Russian Legion has launched OpDenmark, a coordinated cyberattack campaign against Danish critical infrastructure in retaliation for the country’s 1.5 billion DKK military aid package to Ukraine.
BreachForums Breach Exposes 324,000 Cybercriminal Identities in Unprecedented Dark Web Leak
The tables have turned: BreachForums, one of the largest dark web marketplaces for stolen data, has been breached. A disgruntled insider leaked the real identities of nearly 324,000 cybercriminals, including email addresses, IP addresses, and connections to notorious groups like
SonicWall Cloud Breach Enables Ransomware Attack on 74 US Banks and Credit Unions
State-sponsored hackers exploited SonicWall’s MySonicWall cloud breach to launch a ransomware attack affecting 74 US banks and credit unions, compromising data of over 400,000 individuals. The attack demonstrates how third-party security breaches can cascade into devastating down
Nike Investigates 1.4 TB Data Leak After World Leaks Ransomware Gang Posts Stolen Files
Nike confirms it is investigating a potential breach after the World Leaks ransomware gang claimed to have stolen 1.4 TB of corporate data. The group, a rebrand of Hunters International, has targeted major organizations including the U.S. Marshals Service and Tata Technologies.
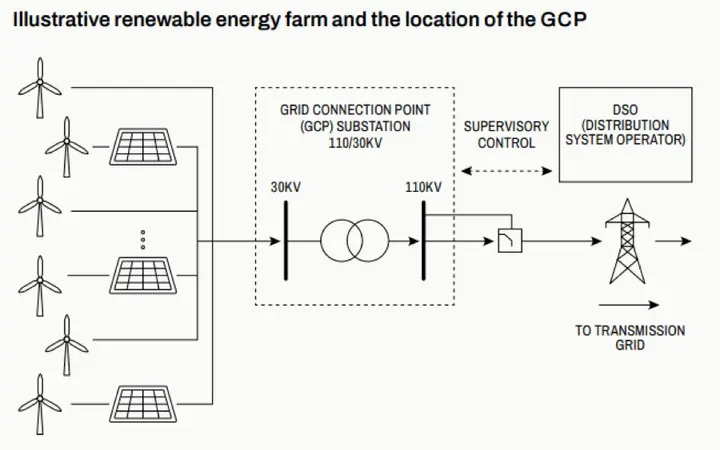
Russian Hackers Launch Coordinated Cyberattacks on Poland’s Renewable Energy Infrastructure
Russian state-sponsored threat actors launched coordinated cyberattacks against Poland’s energy sector on December 29, 2025, targeting over 30 wind and solar farms, a manufacturing company, and a major combined heat and power (CHP) plant that serves nearly 500,000 people, accordi
Iconics Suite SCADA Vulnerability Enables Denial-of-Service Through Privileged File Operations
CVE-2025-0921 in Iconics Suite SCADA allows attackers to exploit privileged file operations to corrupt critical system binaries and crash Windows systems through symbolic link attacks.
Global Energy Systems Exposed: Widespread Cybersecurity Gaps Found in Power Grid OT Networks
A global study by OMICRON reveals critical cybersecurity weaknesses in power grid OT networks, including unpatched devices, weak segmentation, and asset blind spots that leave critical infrastructure vulnerable to attack.
WinRAR CVE-2025-8088: Russia, China, and Cybercriminals Unite to Exploit Path Traversal Flaw
Google Threat Intelligence reveals widespread exploitation of CVE-2025-8088 by Russian APT groups, Chinese actors, and cybercriminals. The WinRAR path traversal flaw enables payload delivery via the Windows Startup folder, with active campaigns targeting Ukraine, LATAM, and finan
North Korean Konni APT Deploys AI-Generated Malware to Target Blockchain Developers
The North Korean threat group Konni has launched a new campaign using AI-generated PowerShell malware to target blockchain developers across the APAC region, marking a significant shift toward technical targets and cryptocurrency infrastructure.
Microsoft to Disable 30-Year-Old NTLM Authentication Protocol by Default
Microsoft announces NTLM will be disabled by default in upcoming Windows releases, marking the end of the 30-year-old authentication protocol that has been a persistent security vulnerability.
CVE-2026-24061: 11-Year-Old GNU Telnetd Vulnerability Grants Instant Root Access
CVE-2026-24061 is a critical 11-year-old vulnerability in GNU InetUtils telnetd that allows unauthenticated attackers to gain instant root shell access. With a CVSS score of 9.8 and active exploitation confirmed, this flaw affects over 200,000 devices running Telnet servers globa
Ivanti Patches Two Critical EPMM Zero-Day Vulnerabilities Under Active Exploitation
Two critical CVSS 9.8 vulnerabilities in Ivanti Endpoint Manager Mobile (CVE-2026-1281, CVE-2026-1340) are under active exploitation, allowing unauthenticated remote code execution. CISA has added them to the KEV catalog with a February 1 federal deadline.
Ivanti EPMM Zero-Days Actively Exploited: Pre-Auth RCE via Bash Arithmetic Expansion
Two actively exploited pre-auth RCE vulnerabilities (CVE-2026-1281 and CVE-2026-1340) in Ivanti Endpoint Manager Mobile allow attackers to execute arbitrary commands via Bash arithmetic expansion. CISA has added these to the KEV catalog.
Android Malware Campaign Abuses Hugging Face AI Platform to Distribute RAT
Threat actors are abusing the Hugging Face AI platform to host Android malware, using server-side polymorphism to generate thousands of RAT variants every 15 minutes.