


Intel Feed
Cyber Threat IntelligencePage 24
Reports
Reporting archive — page 24
Showing 553–576 of 611 reports
The Updated APT Playbook: Tales from the Kimsuky threat actor group
READ ARTICLE Last updated at Thu, 21 Mar 2024 13:20:04 GMT Co-authors are Christiaan Beek and Raj Samani Within Rapid7 Labs we continually track and monitor threat groups. This is one of our key areas of focus as we work to ensure that our ability to protect customers remains con
Curious Serpens’ FalseFont Backdoor: Technical Analysis, Detection and Prevention
By Tom Fakterman, Daniel Frank and Jerome Tujague READ ARTICLE Executive Summary This article reviews the recently discovered FalseFont backdoor, which was used by a suspected Iranian-affiliated threat actor that Unit 42 tracks as Curious Serpens. Curious Serpens (aka Peach Sands
China-Linked Group Breaches Networks via Connectwise, F5 Software Flaws
READ ARTICLE A China-linked threat cluster leveraged security flaws in Connectwise ScreenConnect and F5 BIG-IP software to deliver custom malware capable of delivering additional backdoors on compromised Linux hosts as part of an “aggressive” campaign. Google-owned Mandiant is tr
“Pig butchering” is an evolution of a social engineering tactic we’ve seen for years
By Jonathan Munshaw READ ARTICLE Whether you want to call them “catfishing,” “pig butchering” or just good ‘old-fashioned “social engineering,” romance scams have been around forever. I was first introduced to them through the MTV show “Catfish,” but recently they seem to be maki
New AcidPour Wiper Targeting Linux Devices Spotted in Ukraine
READ ARTICLE By: Kevin Poireault Reporter, Infosecurity Magazine A new variant of the wiper malware AcidRain, known as AcidPour, has been discovered by SentinelOne’s threat intelligence team, SentinelLabs. AcidRain is destructive wiper malware attributed to Russian military intel
Fancy Bear: Espionage group expands global phishing campaign
Source Russia-linked threat actor Fancy Bear is conducting a wave of phishing campaigns impersonating entities across Europe, Americas, and Asia, focusing on Ukraine-related targets. IBM X-Force has identified an ongoing phishing campaign conducted by ITG05, a Russia state-sponso
TBHM Live Training with Jhaddix
Attending The Bug Hunters Methodology Live training by Jason Haddix was a great experience. I think my goal with writing this post is really to paint a picture of my overall personal experience being new to Bug Bounty Hunting, coming from the Blue Teaming side of things, and to j
Detecting and Responding to Security Incidents and Why its Difficult.
Quick Picture of Attacker Vs Defender With the relentless advancement of technology and continuous improvements in security measures, there remains a significant challenge in detecting and responding to security incidents. This difficulty arises partly due to the diverse tactics
Tool of First Resort: Israel-Hamas War in Cyber
Feb 14, 2024 | 4 min read | Sandra Joyce | Shane Huntley READ ARTICLE Cybersecurity plays a critical role in geopolitics — particularly during times of conflict. While offensive cyber operations have become nearly universal, the tactics, timing and objectives of threat actors can
Endpoints vs Routes: What every API hacker needs to know
READ ARTICLE DANA EPP’S BLOG API Hacking Fundamentals February 13, 2024 I recently had an interesting conversation on Twitter/X that got me thinking about API endpoints vs routes. It all started with this tweet: The conversation progressed into whether this was one vulnerability
Bypassing EDRs With EDR-Preloading
READ ARTICLE Marcus Hutchins Previously, I wrote an article detailing how system calls can be utilized to bypass user mode EDR hooks. Now, I want to introduce an alternative technique, “EDR-Preloading”, which involves running malicious code before the EDR’s DLL is loaded into the
Detecting API endpoints and source code with JS Miner
Read Article DANA EPP’S BLOG Security (de)engineering for fun and profit Let’s be honest. Most APIs are naked without some sort of web app frontend calling it. These days, those apps are usually written in some sort of framework based on Javascript. With a bit of work, we can do
Book.HackTricks
To the Book! Disclaimer This book, ‘HackTricks,’ is intended for educational and informational purposes only. The content within this book is provided on an ‘as is’ basis, and the authors and publishers make no representations or warranties of any kind, express or implied, about
Virtual Host Enumeration for Uncovering Hidden Subdomains
Read Article Nairuz Abulhul – Nov 28, 2023 | Published in R3d Buck3T | 8 min read When performing external penetration testing or bug bounty hunting, we explore the targeted system from various angles to collect as much information as possible to identify potential attack vectors
Demystifying Generative AI 🤖 A Security Researcher’s Notes
Roberto Rodriguez – Nov 4, 2023 • 22 min read Read Article As a security researcher, stepping into the world of Generative Artificial Intelligence (GenAI) was like entering unfamiliar territory. While I was excited by the potential it held for revolutionizing security, I soon rea
Threat Modeling LLM Applications
Posted by Gavin Klondike on 06 June 2023 Read Article Before we get started: Hi! My name is GTKlondike, and these are my opinions as a cybersecurity consultant. While experts from the AI Village provided input, I will always welcome open discussion so that we can come to a better
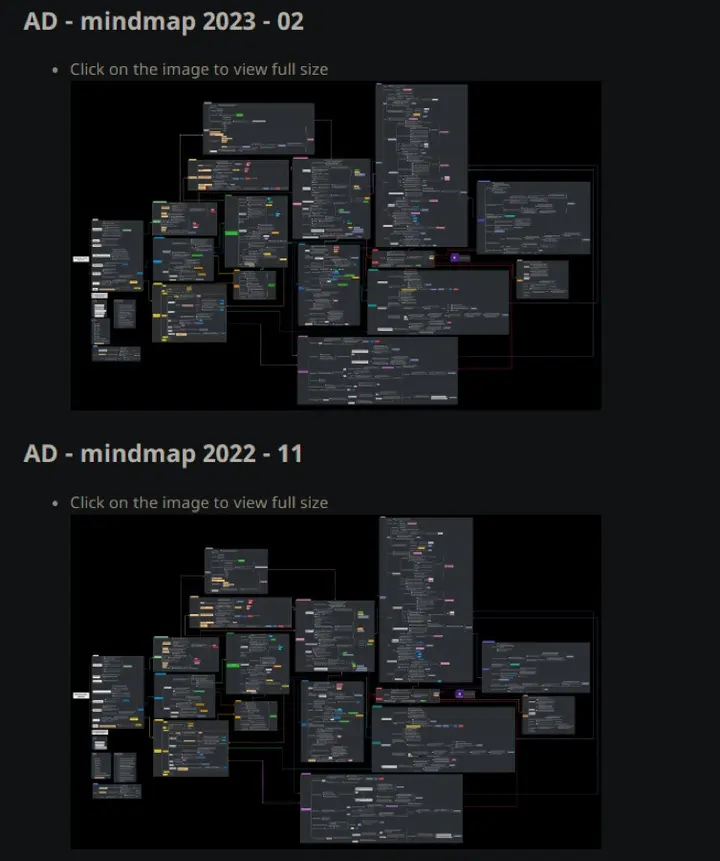
Active Directory Penetration Testing Orange Cyber-defense mind maps
Get Mind Map!
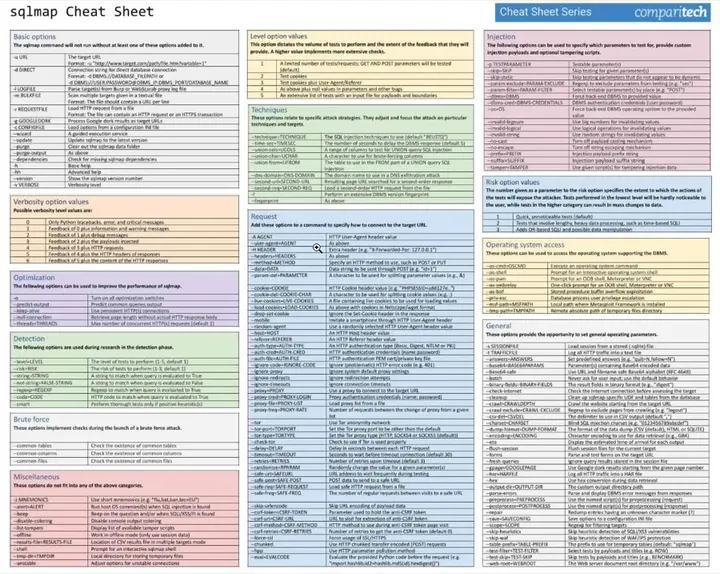
SQLmap Cheat Sheet
Link to Sheet
Announcing cvemap from ProjectDiscovery
Read Article Project Discovery Tool ManagerGitHub pdtm is a simple and easy-to-use golang based tool for managing open source projects from ProjectDiscovery. Security professionals are constantly on guard against cyber threats, especially given the rising number and sophisticatio
How to protect Evilginx using Cloudflare and HTML Obfuscation
Read Article Using a combination of Cloudflare and HTML Obfuscation, it is possible to protect your Evilginx server from being flagged as deceptive and so increase your chances of success on Red Team and Social Engineering engagements. Anyone who has tried to run a Social Enginee
How to Leverage Internal Proxies for Lateral Movement, Firewall Evasion, and Trust Exploitation
THE BUG HUNTERS METHODOLOGY LIVE
https://tbhmlive.com/ Jason Haddix TBHM Live – Course Info I am thrilled to introduce you to The Bug Hunter’s Methodology LIVE, my masterclass designed for aspiring and seasoned offensive security professionals, including web application security testers, red teamers, and bug bou

PWNAGOTCHI: DEEP REINFORCEMENT LEARNING FOR WIFI PWNING!
Project Site Pwnagotchi is an A2C-based “AI” powered by bettercap and running on a Raspberry Pi Zero W that learns from its surrounding WiFi environment in order to maximize the crackable WPA key material it captures (either through passive sniffing or by performing deauthenticat
Automating C2 Infrastructure with Terraform, Nebula, Caddy and Cobalt Strike
Read Article The ability to quickly build out a C2 infrastructure within a few minutes, including all the set up and tear down logic included would be a great asset for any offensive security group or operator. In this post, I will show exactly how to build a fully automated func