


Intel Feed
Cyber Threat IntelligencePage 25
Reports
Reporting archive — page 25
Showing 577–600 of 611 reports
FAKING BLUETOOTH LE WITH AN NRF24L01+ MODULE
SCADA systems: How secure are the systems running our infrastructure?⎥Malav Vyas (Security Researcher at Palo Alto Networks)
Review: Engineering-grade OT security: A manager’s guide
DreamBus Unleashes Metabase Mayhem With New Exploit Module
Read Article Key Takeaways
Detection 101: Top Detections for Email Phishing and BEC
Read Article Phishing Detections: Starting the DIR Process Email phishing and BEC attacks both rely on email communication, so an email security tool is integral to protecting your environment. However, while an email security tool plays a central role in detecting phishing attem
Hundreds of Thousands of Dollars Worth of Solana Cryptocurrency Assets Stolen in Recent CLINKSINK Drainer Campaigns
Read Article On January 3, 2024, Mandiant’s X social media account was taken over and subsequently used to distribute links to a cryptocurrency drainer phishing page. Working with X, we were able to regain control of the account and, based on our investigation over the following
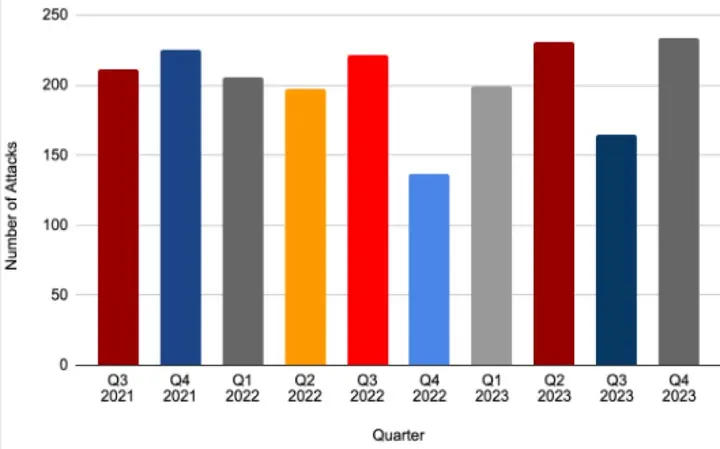
Flash Report: LockBit Ends 2023 with Record Number of Attacks
Read Article Key Findings
Backdoor.Win32 Carbanak (Anunak) / Named Pipe Null DACL
Read Article Discovery / credits: Malvuln (John Page aka hyp3rlinx) (c) 2024 Original source: https://malvuln.com/advisory/b8e1e5b832e5947f41fd6ae6ef6d09a1.txt Contact: malvuln13@gmail.com Media: twitter.com/malvuln Threat: Backdoor.Win32 Carbanak (Anunak) Vulnerability: Named Pi
Which type of malware resides only in RAM? Explaining fileless malware
Read Article Explaining malware which resides only in RAM Unlike traditional malware, which typically involves downloading and running an executable file, fileless malware operates in the system’s memory (RAM) and often exploits legitimate tools (like PowerShell, WMI, or Windows
Hacked in China
Read Article foreign government’s response to a U.S. strategy document rarely earns front page coverage, but in the case of the Chinese Communist Party’s (CCP) recent reaction to the U.S. government’s new cyber strategy, we should all be paying attention. Tensions continue to esc
Financially motivated threat actors misusing App Installer
Read Article Since mid-November 2023, Microsoft Threat Intelligence has observed threat actors, including financially motivated actors like Storm-0569, Storm-1113, Sangria Tempest, and Storm-1674, utilizing the ms-appinstaller URI scheme (App Installer) to distribute malware. In
Opening a Can of Whoop Ads: Detecting and Disrupting a Malvertising Campaign Distributing Backdoors
Read Article Earlier this year, Mandiant’s Managed Defense threat hunting team identified an UNC2975 malicious advertising (“malvertising”) campaign presented to users in sponsored search engine results and social media posts, consistent with activity reported in From DarkGate to
Turkish Hackers Exploiting Poorly Secured MS SQL Servers Across the GlobeTurkish Hackers Exploiting Poorly Secured MS SQL Servers Across the Globe
Read Article Poorly secured Microsoft SQL (MS SQL) servers are being targeted in the U.S., European Union, and Latin American (LATAM) regions as part of an ongoing financially motivated campaign to gain initial access. “The analyzed threat campaign appears to end in one of two wa
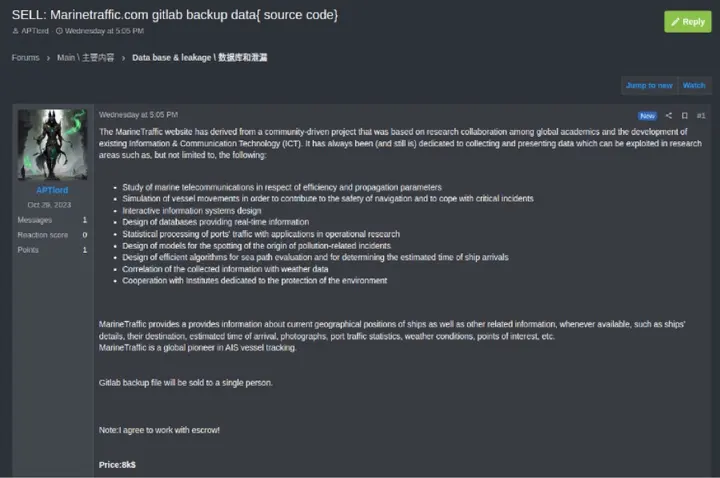
The Underground Economist: Volume 4, Issue 1
https://www.zerofox.com/blog/the-underground-economist-volume-4-issue-1/ On December 27, 2023, threat actor “APTlord” announced on the dark web forum RAMP that they were selling source code and other information owned by marinetraffic[.]com, which was allegedly obtained by the th
Custom GPTs: A Case of Malware Analysis and IoC Analyzing
Read Article On November 6, 2023, CustomGPTs, a new feature that OpenAI stated on its blog, became available. We can already say that the emergence of Custom Generative Pre-trained Transformers (GPTs) could mark a significant shift in the dynamics of both digital defense and offe
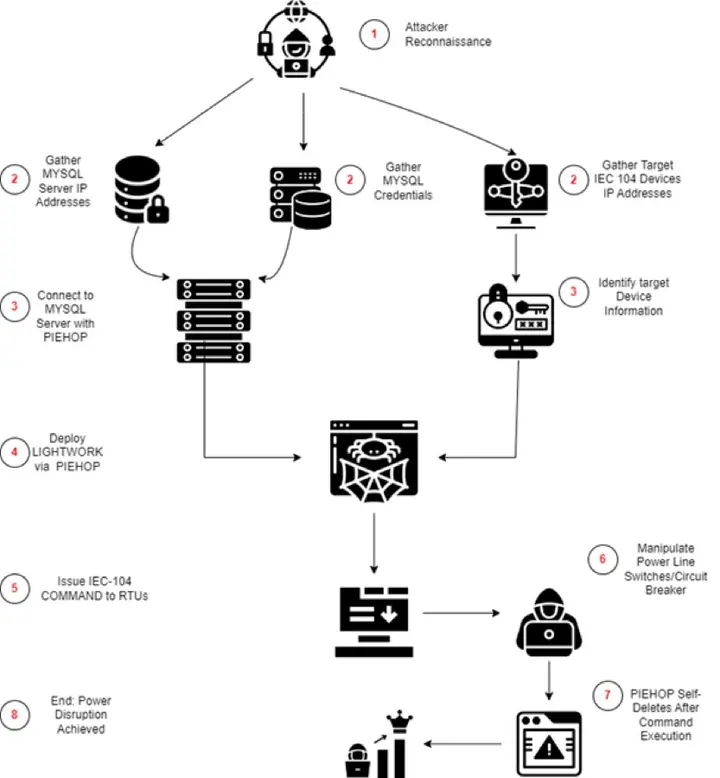
Analysis of OT cyberattacks and malwares
Hardware Implants as an Initial Access Vector
Read Article On every red team engagement, one of the first steps is to gain access to the target environment. Generally, red teams will leverage social engineering techniques to get their customer to run a payload sent through email or other digital means. Unfortunately for us,
Red Pandas Unleashed: How Webhooks, Bad USB, and WiFi Collide in Cyberspace
Read Article The Power of Automation for Pentesting Automation has become a game-changer in the world of penetration testing. With the ever-increasing complexity of networks and systems, manually tracking and responding to security events is no longer viable. This is where webhoo
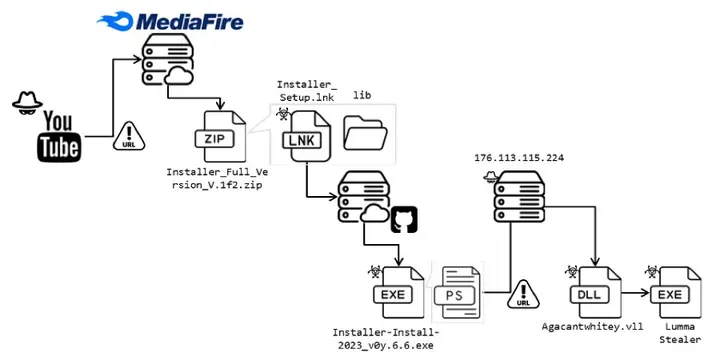
Deceptive Cracked Software Spreads Lumma Variant on YouTube
Read Article Initial Infection Vector The hacker initially breaches a YouTuber’s account and uploads videos masquerading as sharing cracked software. Figure 3 shows the video descriptions in which a malicious URL is embedded, enticing users to download a ZIP file that harbors mal
NoName on Rampage! Claims DDoS Attacks on Ukrainian Government Sites
Read Article NoName ransomware group has allegedly targeted multiple Ukrainian government websites. The latest victims of the alleged NoName ransomware attack on Ukraine include Accordbank, Zaporizhzhya Titanium-Magnesium Plant, State Tax Service, Central Interregional Tax Admini
Alert: Carbanak Malware Strikes Again With Updated Tactics
From Akamai to F5 to NTLM… with love.
Read Article Discovery Note: This paper will be covering 1 smuggle gadget out of about 10 that I use in my testing, however this paper will show how this gadget, originally found by @albinowax, can be modified to pin one provider against another in a brutal fashion as you will re
AsyncRAT loader: Obfuscation, DGAs, decoys and Govno
Read Article Executive summary AT&T Alien Labs has identified a campaign to deliver AsyncRAT onto unsuspecting victim systems. During at least 11 months, this threat actor has been working on delivering the RAT through an initial JavaScript file, embedded in a phishing page. Afte
Chapter 84: In-depth analysis and technical analysis of LockBit, the top encryption ransomware organization (Part 1)
Read Article Excerpt LockBit operators and affiliates will find ways to obtain the victim’s initial access rights and use them to deliver encrypted ransomware. The attack methods can be roughly divided into the following methods: 1. Extensive vulnerability scanning . Using Nday v