


Intel Feed
Cyber Threat IntelligencePage 13
Reports
Reporting archive — page 13
Showing 289–312 of 611 reports
FortiClient EMS Exploitation Turns Endpoint Management Into an Infostealer Delivery System
Attackers are abusing CVE-2026-35616 in FortiClient EMS to push a credential stealer through trusted endpoint management workflows. Here is what defenders should check first.
Meta AI Support Bot Abuse Shows Account Recovery Is Part of the Identity Perimeter
Attackers reportedly abused Meta’s AI support assistant during Instagram account recovery. The lesson for SMBs and contractors: recovery workflows are identity infrastructure and need MFA, monitoring, and guardrails.
SolyxImmortal Shows Why Python Infostealers Are a Business Risk, Not Just Malware Noise
SolyxImmortal combines persistence, browser credential theft, document collection, screenshots, keylogging, and webhook exfiltration. Here is what SMB and government-contractor defenders should do about it.
Showboat and JFMBackdoor Show Telecom Intrusions Are Built for Pivoting
Lumen and PwC reporting on Showboat, Red Lamassu, and JFMBackdoor shows how China-linked telecom intrusions combine Linux footholds, proxying, and Windows backdoors. Here is what SMBs and government contractors should harden now.
WP Maps Pro Exploitation Shows Why Plugin Support Features Need Security Review
Attackers are exploiting CVE-2026-8732 in WP Maps Pro to create rogue WordPress administrator accounts. Here is what SMBs and contractors should patch, audit, and verify.
SideCopy’s XenoRAT Campaign Shows Why Localized Lures Beat Generic Phishing Defenses
SideCopy/APT36 targeted Afghanistan finance officials with Pashto-language lures and XenoRAT. Here is what SMBs and government contractors should take from the campaign.
Dependency Confusion Campaign Shows Reconnaissance Is the First Supply-Chain Payload
Microsoft found 33 malicious npm packages abusing dependency confusion to profile developer and build environments. The defender lesson: treat package installation as code execution and lock down internal namespace hygiene before attackers do reconnaissance at scale.
MediaInfoLib Parser Bugs Show File Metadata Is an Execution Boundary
Cisco Talos disclosed four patched MediaInfoLib heap-based buffer overflow vulnerabilities. The bigger lesson: automated media metadata parsing belongs inside a sandboxed, monitored execution boundary.
Poisoned Search and AI Recommendations Turn Utility Downloads Into RMM Access
Microsoft reported a cryptojacking campaign that uses poisoned search results, AI-surfaced software recommendations, fake utility downloads, and abused ScreenConnect access. Here is what SMBs and government contractors should defend first.
LiteSpeed cPanel KEV Shows Shared Hosting Is Privilege Escalation Terrain
CISA added CVE-2026-48172 to KEV after active exploitation of a LiteSpeed cPanel user-end plugin flaw that can let compromised hosting accounts execute scripts as root.
Megalodon GitHub Actions Backdoor Shows CI/CD Is Now a Credential Battlefield
The Megalodon GitHub campaign shows why CI/CD pipelines must be treated like production infrastructure: malicious workflow commits can harvest cloud credentials, OIDC tokens, SSH keys, and package secrets at scale.
Chinese-Language PhaaS Shows MFA Bypass Is Becoming Real-Time Fraud
Google’s reporting on Chinese-language phishing-as-a-service shows why MFA bypass, real-time OTP interception, and digital wallet fraud require phishing-resistant authentication and session monitoring.
KnowledgeDeliver RCE Shows Shared Machine Keys Are Shared Blast Radius
Mandiant’s KnowledgeDeliver CVE-2026-5426 report shows how shared ASP.NET machine keys can turn ViewState into unauthenticated RCE and user-facing malware delivery.
Laravel-Lang Compromise Shows Dependency Tags Can Be Weaponized
A Laravel-Lang package compromise shows why trusted dependency tags, Composer autoload behavior, and runtime secrets need security monitoring—not just engineering review.
Cl0p’s South Staffs Water Case Shows SOC Coverage Must Be Proven
The South Staffordshire Water breach shows why outsourced SOC coverage, legacy server risk, and vulnerability management must be proven—not assumed—for SMBs, utilities, and government contractors.
ROADtools Abuse Shows Cloud Identity Is the New Attack Surface
Unit 42’s ROADtools research shows why Microsoft Entra ID token abuse, rogue device registration, and Graph API enumeration need to be treated as core incident-response signals for SMBs and government contractors.
Drupal CVE-2026-9082 Shows Web Asset Inventory Is Emergency Response
Drupal CVE-2026-9082 is already being scanned and exploited in the wild. The lesson for SMBs and government contractors: know where your Drupal sites are, verify PostgreSQL exposure, patch fast, and review logs before probing turns into compromise.
Void Dokkaebi’s InvisibleFerret Shift Shows Developer Endpoints Are Production Risk
Trend Micro reports North Korea-aligned Void Dokkaebi has moved InvisibleFerret into Cython-compiled Python extension modules. For SMBs and government contractors, the real risk is developer endpoint access to CI/CD, cloud, and production secrets.
Nimbus Manticore Shows Iranian APTs Are Moving Faster With AI-Assisted Tooling
Check Point Research reports that IRGC-affiliated Nimbus Manticore resurfaced with fake Zoom and SQL Developer lures, SEO poisoning, AppDomain hijacking, and a new MiniFast backdoor. Here is what SMBs and government contractors should tighten first.
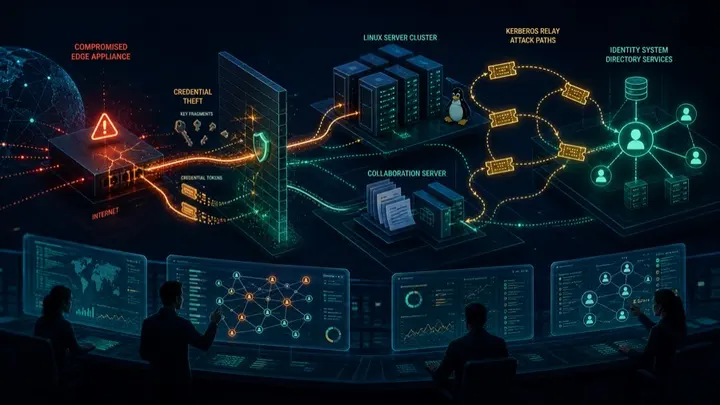
F5-to-Confluence Intrusion Shows Edge Devices Are Identity Attack Paths
Microsoft analyzed an intrusion where an F5 BIG-IP edge appliance led to Linux access, Confluence compromise, credential theft, and identity relay attempts. Here is what SMBs and government contractors should tighten first.
Screening Serpens Shows Recruiting Is Now an Espionage Attack Surface
Iran-nexus Screening Serpens used recruitment and meeting lures, new RAT variants, and .NET AppDomainManager hijacking. Here is what SMBs and government contractors should tighten now.
Kimwolf Arrest Shows DDoS Risk Starts on Forgotten IoT
The alleged Kimwolf botmaster arrest is a useful reminder for SMBs and government contractors: DDoS resilience starts with asset visibility, upstream protection, and hardening forgotten IoT and edge devices.
TamperedChef Shows Signed Productivity Apps Cannot Be Trusted by Default
TamperedChef-style malware hides inside convincing signed productivity apps. Here is what SMBs and government contractors should do about it.
Patriot Bait Shows AI-Enabled Fraud Can Turn Trust Into Attack Surface
Trend Micro’s Patriot Bait research shows how one operator used AI assistance, social trust, WordPress credential attacks, and crypto fraud infrastructure to scale a low-cost cybercrime operation.