


Intel Feed
Cyber Threat IntelligencePage 12
Reports
Reporting archive — page 12
Showing 265–288 of 611 reports
Velvet Ant Shows Authentication Infrastructure Is Critical Infrastructure
Velvet Ant’s Operation Highland shows why PAM, OpenSSH, jump hosts, and proxy paths deserve the same defensive priority as identity providers and domain controllers.
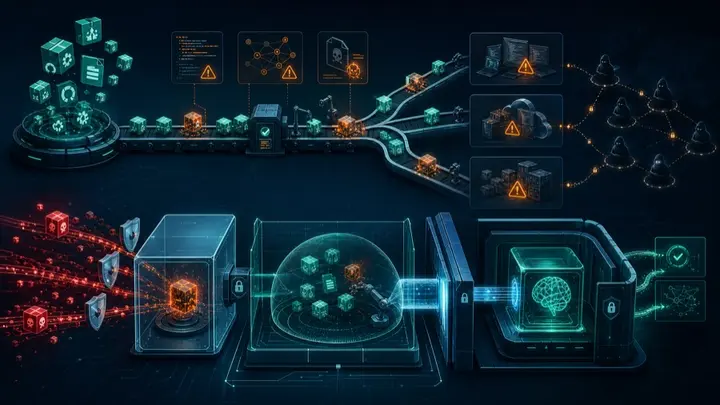
Shai-Hulud Shows AI Package Scanners Need Prompt-Injection Boundaries
Zscaler ThreatLabz says the Shai-Hulud campaign has expanded across package ecosystems and introduced prompt-injection tactics aimed at automated AI security triage. The defense lesson is simple: treat package content as hostile input, even when an LLM is doing the review.
Maine Breach Portal Hoax Shows Disclosure Systems Need Verification Controls
Maine took its public breach notification database offline after fake disclosures were published. The lesson for SMBs and government contractors: public trust workflows need verification, moderation, and correction controls.
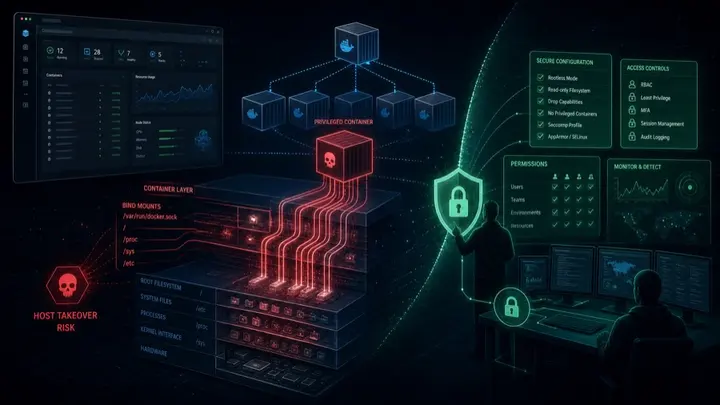
Portainer CVE-2026-33590 Shows Container Admin Tools Need Least Privilege Defaults
intWave disclosed CVE-2026-33590 in Portainer, where insecure default Docker security settings could let regular users escalate toward host takeover. Here is what SMBs and government contractors should lock down.
MaXSS and Spyder Show AI Browser Extensions Are an Endpoint Risk
Rebora disclosed MaXSS and Spyder, two critical flaws in AI browser-extension side panels. The lesson for SMBs and government contractors: browser extensions are endpoint software with identity-session reach and need governance.
ShinyHunters PeopleSoft Exploitation Shows ERP Admin Endpoints Are Breach Surface
GTIG and Mandiant report active ShinyHunters exploitation of Oracle PeopleSoft CVE-2026-35273. Here is what defenders should lock down, hunt, and segment now.
LangGraph Checkpointer Bugs Show AI Agent Memory Is Backend Attack Surface
Check Point Research disclosed LangGraph checkpointer flaws that could turn user-controlled state-history filters into SQL injection, unsafe deserialization, and remote code execution. The lesson for SMBs and government contractors: AI agent memory is application infrastructure,
IMA Diligence Breach Shows Legacy Servers Are Still Third-Party Risk
A reported IMA Diligence breach affecting more than 525,000 people shows why legacy third-party servers need ownership, monitoring, decommissioning, and data-risk review.
C0XMO Shows IoT Botnets Are Still an Edge Exposure Problem
Fortinet researchers detailed C0XMO, a Gafgyt variant spreading through DD-WRT and other exposed devices. Here is what SMBs and government contractors should lock down before compromised routers become DDoS infrastructure.
SolarWinds Serv-U Exploitation Shows File Transfer Availability Is Security
CISA added actively exploited SolarWinds Serv-U CVE-2026-28318 to KEV. Here is what SMBs and government contractors should do about file-transfer availability risk.
Pink Extortion Shows Microsoft 365 Defense Starts With Vishing Controls
Unit 42 is tracking Pink / CL-CRI-1147, a Com-affiliated extortion brand using vishing, credential theft, and Microsoft 365 data exfiltration. Here is what SMBs and government contractors should lock down now.
ChatGPT Lockdown Mode Shows Prompt Injection Defense Is About Egress Control
OpenAI’s ChatGPT Lockdown Mode is a useful reminder that prompt-injection defense is not just about model behavior. It is about limiting outbound paths, connector permissions, and tool access around sensitive work.
PAN-OS GlobalProtect Exploitation Shows VPN Access Needs Log Review, Not Just Patching
Unit 42 reports active exploitation attempts against PAN-OS GlobalProtect CVE-2026-0257. Defenders should patch, but also review VPN sessions, authentication override cookie behavior, and edge-device telemetry for signs of unauthorized access.
UNC3753 Brings Vishing, RMM Abuse, and Physical Intrusions to U.S. Law Firms
Mandiant reports that UNC3753, also known as Luna Moth / Silent Ransom Group, is targeting U.S. law firms and professional services with vishing, RMM abuse, rapid data theft, and suspected physical office intrusions. Here is what SMBs and government contractors should lock down n
Cisco SD-WAN Zero-Day Shows Edge Controllers Need Compromise Review
Cisco says CVE-2026-20245 has been exploited against Catalyst SD-WAN Manager. Defenders should preserve evidence, review controller logs, validate edge-device configuration, and restrict management-plane access.
Agentic AI Failure Modes Show Why AI Tools Need Supply-Chain Controls
Microsoft’s updated agentic AI failure-mode taxonomy turns AI agents into a practical security architecture problem: plugins, prompts, memory, browser use, and human approvals all need controls.
Error 524 Smishing Shows Why Fraud Infrastructure Needs CTI
Group-IB documented a global smishing operation using fake error pages, geofencing, and encrypted WebSocket exfiltration. Here is what SMBs and government contractors should take from it.
Fuel Tank Gauge Attacks Show Why Small OT Still Needs Internet Exposure Control
Federal agencies warn that attackers are compromising internet-exposed automatic tank gauge systems. The lesson for SMBs, fuel operators, farms, logistics firms, and gov contractors is simple: small OT is still operational infrastructure.
Stock Exchange Mailbox Espionage Shows Executive Email Is Strategic Infrastructure
A five-month espionage campaign against a stock exchange executive mailbox shows why senior email accounts need privileged-asset controls, cloud exfiltration monitoring, and scheduled-task hunting.
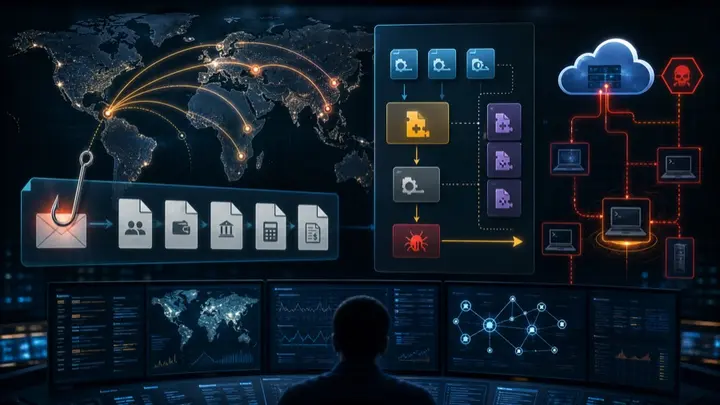
TA4922’s Global Expansion Shows HR and Tax Lures Are Initial Access Infrastructure
Proofpoint’s TA4922 reporting shows how localized HR, payroll, tax, and invoice lures can become full initial-access infrastructure through DLL sideloading, loaders, RATs, RMM tools, and browser credential theft.
Red Hat’s Miasma npm Compromise Shows Trusted Publishing Is Not a Control Boundary
A Red Hat Cloud Services npm compromise shows why signed releases and trusted publishing must be paired with install-time controls, CI/CD isolation, and fast credential rotation.
AI-Assisted Ransomware Tooling Shows EDR Evasion Is Now an Iteration Problem
Sophos observed ransomware-linked operators using AI-assisted development workflows to accelerate EDR evasion testing and Active Directory discovery. The defensive lesson: validate controls, harden identity, and monitor behavior before attackers iterate around your tooling.
FlutterBridge Shows Why macOS Malvertising Is Backdoor Delivery, Not Just Adware
Unit 42’s FlutterBridge research shows macOS malvertising evolving from adware into FlutterShell backdoor delivery. Here is what SMBs and government contractors should tighten first.
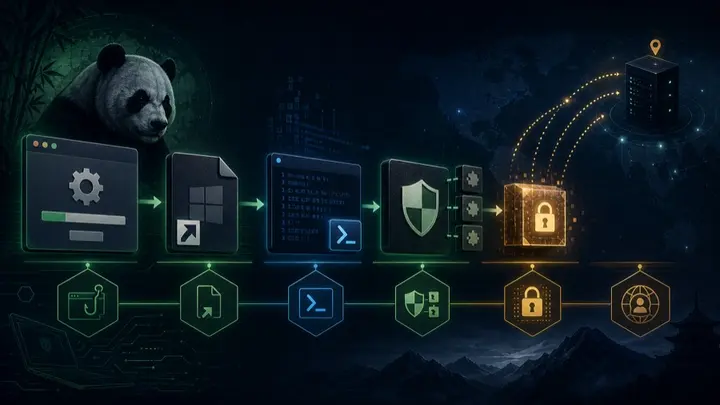
Mustang Panda’s Fake Browser Updater Shows Why LNK Files Still Matter
Mustang Panda’s fake browser updater chain shows why defenders still need to hunt LNK-to-PowerShell execution, DLL sideloading, user-context persistence, and suspicious HTTPS beaconing.