


Intel Feed
Cyber Threat IntelligencePage 10
Reports
Reporting archive — page 10
Showing 217–240 of 584 reports
Clean Repos Can Still Burn Developer Machines When AI Agents Trust Runtime Setup
A clean-looking repository can still become dangerous when an AI coding agent follows setup instructions and executes runtime-fetched configuration. Here is how teams should defend developer workflows.
Splunk Enterprise RCE Shows SIEM Servers Are Tier-Zero Infrastructure
CVE-2026-20253 shows why Splunk and other SIEM platforms need tier-zero hardening: patch quickly, restrict management access, review service accounts, and hunt for suspicious file writes.
NAIC Breach Shows Why PeopleSoft Internet Exposure Needs Immediate Review
NAIC’s PeopleSoft-linked breach is a practical warning for SMBs and government contractors: patch CVE-2026-35273, restrict administrative endpoints, and hunt for attacker staging before extortion begins.
Hospitality Photo-ZIP Campaign Shows Front Desk Workflows Are Initial Access Paths
Microsoft’s hospitality photo-ZIP campaign shows why front desk, booking, and customer intake workflows need executable-content controls, redirect-chain inspection, and endpoint hunting for unusual Node.js persistence.
CL-STA-1062 Shows Critical Infrastructure Intrusions Still Start With Web Shells
Unit 42’s CL-STA-1062 report shows why defenders should focus on exposed web apps, web shells, tunneling tools, scheduled-task persistence, and egress visibility — not just the TinyRCT malware name.
Turla’s STOCKSTAY Backdoor Shows Why Espionage Defense Needs Egress Visibility
GTIG’s STOCKSTAY research shows how Turla blends modular .NET malware, WebSocket C2, and diplomatic targeting. Here are the defensive lessons for SMBs and government contractors.
StrikeShark Shows Loader Malware Is an Edge-Exposure Problem
Kaspersky’s StrikeShark research shows how opportunistic exploitation of exposed servers can become a multi-stage SharkLoader and Cobalt Strike intrusion. Here is what SMBs and government contractors should review now.
MuddyWater’s Chaos Masquerade Shows Ransomware Response Needs Attribution Discipline
Iran-linked MuddyWater activity shows why ransomware response needs to examine identity compromise, remote access, and adversary objectives instead of trusting the ransom note at face value.
SocGholish Takedown Shows Website Trust Is Malware Infrastructure
Operation Endgame disrupted SocGholish infrastructure, but the defensive lesson is bigger: compromised trusted websites are malware delivery infrastructure.
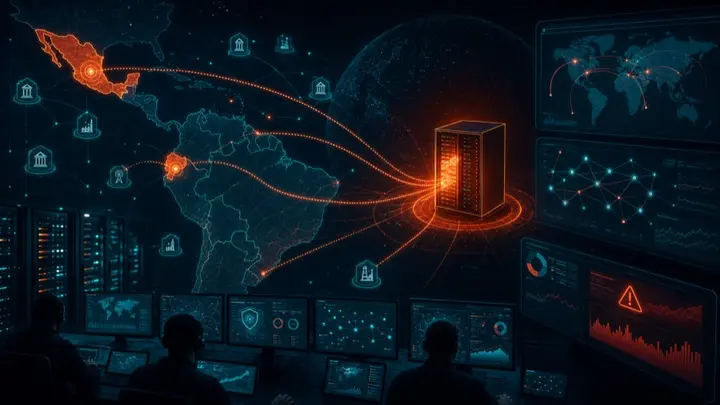
Operation Escaneo Shows Latin America’s Edge Devices Are Prime Intrusion Targets
Operation Escaneo shows how financially motivated actors are turning exposed edge devices, tunnels, and privileged service accounts into full intrusion chains across Latin American government and critical infrastructure targets.
Mastra npm Compromise Shows AI Frameworks Are Supply-Chain Targets
Microsoft linked the Mastra AI npm package compromise to North Korean actor Sapphire Sleet. Here is what SMBs and government contractors should do about AI framework supply-chain risk.
Showboat Malware Shows Telecom Linux Servers Need Rootkit-Level Monitoring
Showboat is a China-linked Linux post-exploitation framework aimed at telecom providers. The lesson for defenders: treat Linux server persistence, dynamic linker abuse, and low-noise C2 as first-class monitoring priorities.
AutoJack Shows AI Browsing Agents Need Localhost Boundaries
Microsoft’s AutoJack research shows how a malicious webpage can abuse an AI browsing agent’s access to localhost services. The defensive lesson: treat agent control planes, MCP servers, and local tool runners like privileged admin surfaces.
Apache APISIX Auth Bypass Cluster Shows API Gateways Need Plugin-Level Review
Apache disclosed a cluster of APISIX authentication and identity plugin CVEs. The defensive priority is patching, plugin inventory, and validating what backend services trust from the gateway.
FortiBleed Shows Firewall Patching Is Not Compromise Recovery
FortiBleed is a reminder that edge firewall patching is necessary, but it does not prove a previously exposed appliance is clean. Defenders need compromise review, credential rotation, and rebuild plans for perimeter devices.
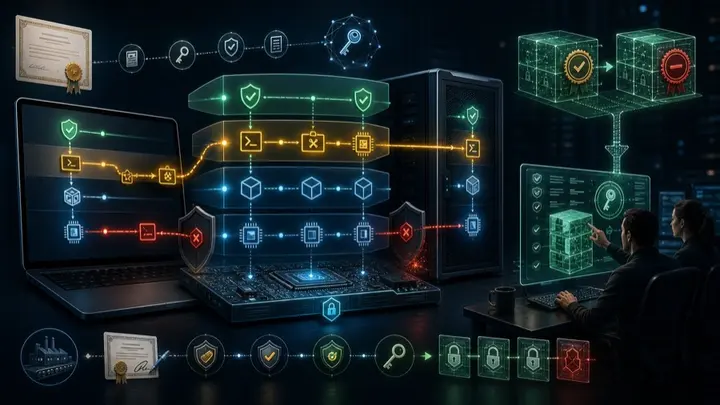
Vendor-Signed UEFI Apps Show Secure Boot Still Depends on Revocation Hygiene
CERT/CC warns that multiple vendor-signed UEFI applications can be abused to bypass Secure Boot before the operating system and EDR controls ever load. For SMBs and government contractors, the fix is not just firmware patching; it is verifying DBX revocation coverage across manag
SmartApeSG Okendo Compromise Shows Third-Party Widgets Are Supply-Chain Risk
Zscaler ThreatLabz reported that SmartApeSG injected malicious JavaScript into the Okendo Reviews widget, creating downstream exposure across e-commerce sites. Here is what SMBs and government contractors should do about third-party browser code risk.
Tor-Based Crypto Clipper Shows Clipboard Theft Is Now Backdoor Activity
Microsoft research on a Tor-routed crypto clipper shows why defenders should connect USB shortcut execution, script interpreters, localhost proxy activity, and clipboard theft into one investigation path.
Outsider Enterprise Shows AI-Powered Phishing Is Now Industrial Infrastructure
The Outsider Enterprise takedown shows AI-powered phishing is now industrial infrastructure. SMBs and government contractors should prioritize phishing-resistant MFA, identity recovery controls, and rapid session revocation.
Handala’s Cal Water Claim Shows OT Defense Starts With Segmentation
Handala’s California Water Service claim is a reminder that critical-infrastructure defense starts with proving separation between billing systems, telemetry platforms, and operational technology.
FortiPortal CVE-2026-49938 Shows Network Configuration Data Is a High-Value Target
Fortinet CVE-2026-49938 is a medium-severity FortiPortal API access-control issue, but sensitive network configuration exposure can still give attackers a valuable map of the environment.
Velvet Ant Shows Authentication Infrastructure Is Critical Infrastructure
Velvet Ant’s Operation Highland shows why PAM, OpenSSH, jump hosts, and proxy paths deserve the same defensive priority as identity providers and domain controllers.
Shai-Hulud Shows AI Package Scanners Need Prompt-Injection Boundaries
Zscaler ThreatLabz says the Shai-Hulud campaign has expanded across package ecosystems and introduced prompt-injection tactics aimed at automated AI security triage. The defense lesson is simple: treat package content as hostile input, even when an LLM is doing the review.
Maine Breach Portal Hoax Shows Disclosure Systems Need Verification Controls
Maine took its public breach notification database offline after fake disclosures were published. The lesson for SMBs and government contractors: public trust workflows need verification, moderation, and correction controls.