


Showing 289–305 of 305 reports
PawsRunner Steganography Shows Infostealers Are Hiding in Plain Sight
FortiGuard Labs reports PureLogs is being delivered through PawsRunner steganography. Here is what SMBs and government contractors should watch for defensively.
BlackFile Vishing Campaign Shows Why MFA Alone Is Not Enough
GTIG reports UNC6671 / BlackFile is using vishing, AiTM phishing, and SaaS data theft to extort organizations. Here is what SMBs and government contractors should harden now.
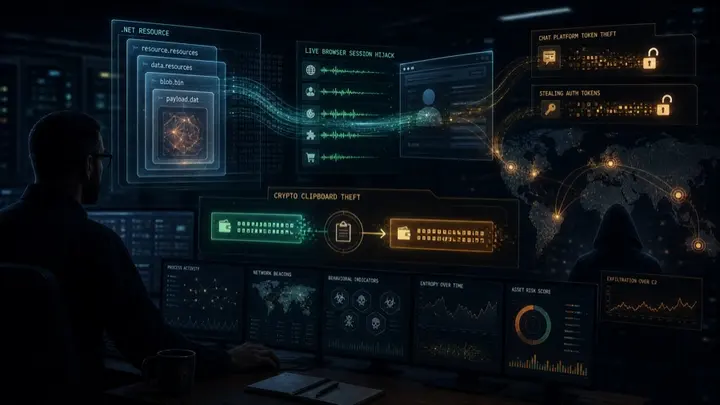
Gremlin Stealer Shows Why Browser Sessions Are Now High-Value Targets
Unit 42 reports Gremlin Stealer has evolved with resource-file obfuscation, session hijacking, Discord token theft, and crypto clipboard fraud. Here is what SMBs and government contractors should do defensively.
Cisco SD-WAN Exploitation Shows Edge Controllers Need Emergency Review
Cisco Talos reports active exploitation of Catalyst SD-WAN authentication bypass and related vulnerabilities. Here is what SMBs and government contractors should prioritize now.
Kazuar Shows Russian Espionage Malware Is Engineering for Resilience
Microsoft reports that Kazuar, attributed to Russian state actor Secret Blizzard, has evolved into a modular P2P botnet. Here is what SMBs and government contractors should take from it defensively.
Exposed AI Apps Turn Misconfiguration Into RCE Risk
Microsoft warns that publicly exposed AI apps, MCP servers, and Kubernetes-hosted agent tooling can turn weak defaults into practical paths for RCE, credential theft, and data exposure.
May 2026 Patch Tuesday: How SMBs Should Prioritize 132 Microsoft CVEs
Microsoft’s May 2026 Patch Tuesday shipped 132 CVEs. Here is how SMBs and government contractors should prioritize identity, server, and Office risks first.
The Gentlemen RaaS Leak Shows Ransomware Is Still an Edge-Device Problem
Check Point’s look inside The Gentlemen ransomware operation is a useful reminder for SMBs and government contractors: exposed edge appliances, weak identity controls, and unmanaged remote access paths still drive real ransomware risk.
JDownloader Site Compromise Shows Why Trusted Downloads Still Need Verification
Attackers swapped selected JDownloader website download links with malicious installers. Here is what SMB and government-contractor defenders should do about trusted-download risk.
Fake OpenAI Hugging Face Repo Shows AI Supply Chain Risk Is Already Here
A fake OpenAI Privacy Filter repository on Hugging Face delivered Windows infostealer malware. Here is what SMB and gov-contractor defenders should take from it.
MCP Server Command Injection Shows Why AI Tools Need Real Isolation
A critical GitHub advisory for @profullstack/mcp-server shows how unsafe AI tool endpoints can turn domain lookup functionality into unauthenticated remote code execution.
Dirty Frag Turns Linux Footholds Into Root: What Defenders Should Do Now
Microsoft is tracking active Dirty Frag Linux privilege escalation activity. Here is what SMB and gov-contractor defenders should prioritize now.
Prompt Injection Just Became an RCE Problem for AI Agents
Microsoft disclosed Semantic Kernel vulnerabilities showing how prompt injection can cross into code execution when AI agents are connected to unsafe tools. Here is what defenders should review now.
PAN-OS Captive Portal Zero-Day Shows Why Internet-Facing Edge Devices Need Immediate Review
Unit 42 reports limited exploitation of CVE-2026-0300, a PAN-OS Captive Portal zero-day. Here is what SMB and government-contractor defenders should check now.
PCPJack Shows Cloud Malware Is Moving From Cryptomining to Credential Theft
SentinelLabs reported PCPJack, a cloud-focused worm that evicts TeamPCP artifacts, steals credentials from exposed infrastructure, and spreads across cloud systems.
TBHM Live Training with Jhaddix
Attending The Bug Hunters Methodology Live training by Jason Haddix was a great experience. I think my goal with writing this post is really to paint a picture of my overall personal experience being new to Bug Bounty Hunting, coming from the Blue Teaming side of things, and to j
Detecting and Responding to Security Incidents and Why its Difficult.
Quick Picture of Attacker Vs Defender With the relentless advancement of technology and continuous improvements in security measures, there remains a significant challenge in detecting and responding to security incidents. This difficulty arises partly due to the diverse tactics