


Showing 241–264 of 305 reports
Agentic AI Failure Modes Show Why AI Tools Need Supply-Chain Controls
Microsoft’s updated agentic AI failure-mode taxonomy turns AI agents into a practical security architecture problem: plugins, prompts, memory, browser use, and human approvals all need controls.
Error 524 Smishing Shows Why Fraud Infrastructure Needs CTI
Group-IB documented a global smishing operation using fake error pages, geofencing, and encrypted WebSocket exfiltration. Here is what SMBs and government contractors should take from it.
Fuel Tank Gauge Attacks Show Why Small OT Still Needs Internet Exposure Control
Federal agencies warn that attackers are compromising internet-exposed automatic tank gauge systems. The lesson for SMBs, fuel operators, farms, logistics firms, and gov contractors is simple: small OT is still operational infrastructure.
Stock Exchange Mailbox Espionage Shows Executive Email Is Strategic Infrastructure
A five-month espionage campaign against a stock exchange executive mailbox shows why senior email accounts need privileged-asset controls, cloud exfiltration monitoring, and scheduled-task hunting.
TA4922’s Global Expansion Shows HR and Tax Lures Are Initial Access Infrastructure
Proofpoint’s TA4922 reporting shows how localized HR, payroll, tax, and invoice lures can become full initial-access infrastructure through DLL sideloading, loaders, RATs, RMM tools, and browser credential theft.
Red Hat’s Miasma npm Compromise Shows Trusted Publishing Is Not a Control Boundary
A Red Hat Cloud Services npm compromise shows why signed releases and trusted publishing must be paired with install-time controls, CI/CD isolation, and fast credential rotation.
AI-Assisted Ransomware Tooling Shows EDR Evasion Is Now an Iteration Problem
Sophos observed ransomware-linked operators using AI-assisted development workflows to accelerate EDR evasion testing and Active Directory discovery. The defensive lesson: validate controls, harden identity, and monitor behavior before attackers iterate around your tooling.
FlutterBridge Shows Why macOS Malvertising Is Backdoor Delivery, Not Just Adware
Unit 42’s FlutterBridge research shows macOS malvertising evolving from adware into FlutterShell backdoor delivery. Here is what SMBs and government contractors should tighten first.
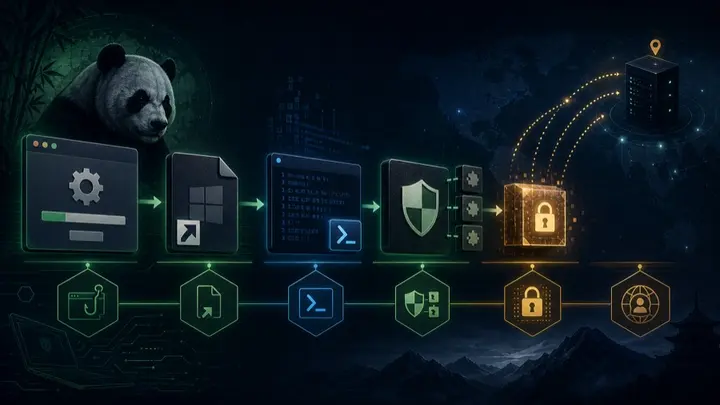
Mustang Panda’s Fake Browser Updater Shows Why LNK Files Still Matter
Mustang Panda’s fake browser updater chain shows why defenders still need to hunt LNK-to-PowerShell execution, DLL sideloading, user-context persistence, and suspicious HTTPS beaconing.
FortiClient EMS Exploitation Turns Endpoint Management Into an Infostealer Delivery System
Attackers are abusing CVE-2026-35616 in FortiClient EMS to push a credential stealer through trusted endpoint management workflows. Here is what defenders should check first.
Meta AI Support Bot Abuse Shows Account Recovery Is Part of the Identity Perimeter
Attackers reportedly abused Meta’s AI support assistant during Instagram account recovery. The lesson for SMBs and contractors: recovery workflows are identity infrastructure and need MFA, monitoring, and guardrails.
SolyxImmortal Shows Why Python Infostealers Are a Business Risk, Not Just Malware Noise
SolyxImmortal combines persistence, browser credential theft, document collection, screenshots, keylogging, and webhook exfiltration. Here is what SMB and government-contractor defenders should do about it.
Showboat and JFMBackdoor Show Telecom Intrusions Are Built for Pivoting
Lumen and PwC reporting on Showboat, Red Lamassu, and JFMBackdoor shows how China-linked telecom intrusions combine Linux footholds, proxying, and Windows backdoors. Here is what SMBs and government contractors should harden now.
WP Maps Pro Exploitation Shows Why Plugin Support Features Need Security Review
Attackers are exploiting CVE-2026-8732 in WP Maps Pro to create rogue WordPress administrator accounts. Here is what SMBs and contractors should patch, audit, and verify.
SideCopy’s XenoRAT Campaign Shows Why Localized Lures Beat Generic Phishing Defenses
SideCopy/APT36 targeted Afghanistan finance officials with Pashto-language lures and XenoRAT. Here is what SMBs and government contractors should take from the campaign.
Dependency Confusion Campaign Shows Reconnaissance Is the First Supply-Chain Payload
Microsoft found 33 malicious npm packages abusing dependency confusion to profile developer and build environments. The defender lesson: treat package installation as code execution and lock down internal namespace hygiene before attackers do reconnaissance at scale.
MediaInfoLib Parser Bugs Show File Metadata Is an Execution Boundary
Cisco Talos disclosed four patched MediaInfoLib heap-based buffer overflow vulnerabilities. The bigger lesson: automated media metadata parsing belongs inside a sandboxed, monitored execution boundary.
Poisoned Search and AI Recommendations Turn Utility Downloads Into RMM Access
Microsoft reported a cryptojacking campaign that uses poisoned search results, AI-surfaced software recommendations, fake utility downloads, and abused ScreenConnect access. Here is what SMBs and government contractors should defend first.
LiteSpeed cPanel KEV Shows Shared Hosting Is Privilege Escalation Terrain
CISA added CVE-2026-48172 to KEV after active exploitation of a LiteSpeed cPanel user-end plugin flaw that can let compromised hosting accounts execute scripts as root.
Megalodon GitHub Actions Backdoor Shows CI/CD Is Now a Credential Battlefield
The Megalodon GitHub campaign shows why CI/CD pipelines must be treated like production infrastructure: malicious workflow commits can harvest cloud credentials, OIDC tokens, SSH keys, and package secrets at scale.
Chinese-Language PhaaS Shows MFA Bypass Is Becoming Real-Time Fraud
Google’s reporting on Chinese-language phishing-as-a-service shows why MFA bypass, real-time OTP interception, and digital wallet fraud require phishing-resistant authentication and session monitoring.
KnowledgeDeliver RCE Shows Shared Machine Keys Are Shared Blast Radius
Mandiant’s KnowledgeDeliver CVE-2026-5426 report shows how shared ASP.NET machine keys can turn ViewState into unauthenticated RCE and user-facing malware delivery.
Laravel-Lang Compromise Shows Dependency Tags Can Be Weaponized
A Laravel-Lang package compromise shows why trusted dependency tags, Composer autoload behavior, and runtime secrets need security monitoring—not just engineering review.
Cl0p’s South Staffs Water Case Shows SOC Coverage Must Be Proven
The South Staffordshire Water breach shows why outsourced SOC coverage, legacy server risk, and vulnerability management must be proven—not assumed—for SMBs, utilities, and government contractors.