


Showing 265–288 of 305 reports
ROADtools Abuse Shows Cloud Identity Is the New Attack Surface
Unit 42’s ROADtools research shows why Microsoft Entra ID token abuse, rogue device registration, and Graph API enumeration need to be treated as core incident-response signals for SMBs and government contractors.
Drupal CVE-2026-9082 Shows Web Asset Inventory Is Emergency Response
Drupal CVE-2026-9082 is already being scanned and exploited in the wild. The lesson for SMBs and government contractors: know where your Drupal sites are, verify PostgreSQL exposure, patch fast, and review logs before probing turns into compromise.
Void Dokkaebi’s InvisibleFerret Shift Shows Developer Endpoints Are Production Risk
Trend Micro reports North Korea-aligned Void Dokkaebi has moved InvisibleFerret into Cython-compiled Python extension modules. For SMBs and government contractors, the real risk is developer endpoint access to CI/CD, cloud, and production secrets.
Nimbus Manticore Shows Iranian APTs Are Moving Faster With AI-Assisted Tooling
Check Point Research reports that IRGC-affiliated Nimbus Manticore resurfaced with fake Zoom and SQL Developer lures, SEO poisoning, AppDomain hijacking, and a new MiniFast backdoor. Here is what SMBs and government contractors should tighten first.
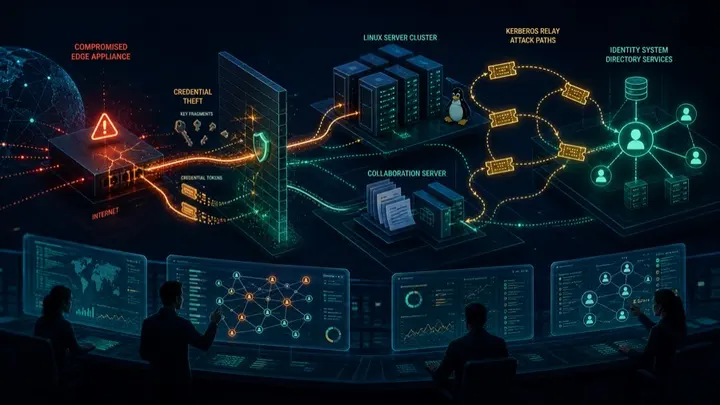
F5-to-Confluence Intrusion Shows Edge Devices Are Identity Attack Paths
Microsoft analyzed an intrusion where an F5 BIG-IP edge appliance led to Linux access, Confluence compromise, credential theft, and identity relay attempts. Here is what SMBs and government contractors should tighten first.
Screening Serpens Shows Recruiting Is Now an Espionage Attack Surface
Iran-nexus Screening Serpens used recruitment and meeting lures, new RAT variants, and .NET AppDomainManager hijacking. Here is what SMBs and government contractors should tighten now.
Kimwolf Arrest Shows DDoS Risk Starts on Forgotten IoT
The alleged Kimwolf botmaster arrest is a useful reminder for SMBs and government contractors: DDoS resilience starts with asset visibility, upstream protection, and hardening forgotten IoT and edge devices.
TamperedChef Shows Signed Productivity Apps Cannot Be Trusted by Default
TamperedChef-style malware hides inside convincing signed productivity apps. Here is what SMBs and government contractors should do about it.
Patriot Bait Shows AI-Enabled Fraud Can Turn Trust Into Attack Surface
Trend Micro’s Patriot Bait research shows how one operator used AI assistance, social trust, WordPress credential attacks, and crypto fraud infrastructure to scale a low-cost cybercrime operation.
Mini Shai-Hulud Shows CI/CD Secrets Are the Real npm Supply-Chain Prize
Mini Shai-Hulud’s @antv npm compromise shows why dependency malware should be treated as a CI/CD credential-theft threat, not just a package hygiene problem.
ExifTool CVE-2026-3102 Shows Image Metadata Belongs in the Threat Model
CVE-2026-3102 in ExifTool shows why image metadata processing should be patched, isolated, and monitored like any other untrusted file-ingest path.
P2Pinfect Shows Exposed Redis in Kubernetes Can Become Dormant Botnet Infrastructure
Fortinet observed P2Pinfect infections inside GKE clusters where exposed Redis instances became long-lived botnet footholds. For SMBs and government contractors, the lesson is clear: cloud misconfiguration, runtime visibility, and egress monitoring matter as much as patching.
Verizon DBIR 2026 Shows Vulnerability Exploitation Is Now the Breach Priority
Verizon’s 2026 DBIR shows vulnerability exploitation overtaking credential abuse as the top breach access vector. Here is what SMBs and government contractors should fix first.
Fox Tempest Shows Code Signing Trust Can Be Weaponized
Microsoft disrupted Fox Tempest, a malware-signing-as-a-service operation that helped ransomware crews make malicious binaries look trusted. Here is what SMBs and government contractors should review now.
CISA GovCloud Leak Shows Secret Scanning Cannot Be Optional
A reported CISA contractor GitHub leak shows why secret scanning, token rotation, and CI/CD hardening need to be enforced controls, not optional developer hygiene.
Storm-2949 Shows Cloud Breaches Start With Identity, Not Malware
Microsoft’s Storm-2949 case study is a clean warning for SMBs and government contractors: once cloud identity and control-plane access are compromised, attackers can steal data without deploying traditional malware.
AI Agent Governance Is Becoming a Security Control, Not a Nice-to-Have
AI agents now operate with real credentials inside business systems. Here is how SMBs and government contractors should govern identity, authority, action, and evidence before agentic workflows become unmanaged risk.
SGLang RCE Flaws Show AI Inference Servers Need Real Network Isolation
CERT/CC disclosed three SGLang vulnerabilities affecting AI inference deployments, including remote code execution and path traversal risks. Here is what SMBs and government contractors should do now.
Grafana GitHub Token Breach Shows Why Source Code Access Needs Guardrails
Grafana disclosed unauthorized GitHub access tied to a leaked token and codebase download. Here is what SMBs and government contractors should tighten around source-code access, CI/CD tokens, and extortion readiness.
AI Literacy Needs Fundamentals: Teaching Technology in the Real World
Albert LaScola reflects on teaching database systems, governance, risk management, and AI literacy through a fundamentals-first approach shaped by Navy operations, security work, Bulwark Black, and Rural Tech and Support.
node-ipc Backdoor Shows Why CI Secrets Need Supply Chain Controls
Malicious node-ipc npm releases turned a package update into a credential-exposure event. Here is what SMBs and government contractors should check first.
Exchange OWA Zero-Day Shows Why Email Servers Need Emergency Mitigation
CISA added Microsoft Exchange Server CVE-2026-42897 to KEV after evidence of active exploitation. For SMBs and government contractors, the lesson is simple: internet-facing email infrastructure needs emergency mitigation playbooks before the patch lands.
Device Code Phishing Turns Legitimate Login Flows Into Token Theft
Device code phishing is scaling because it abuses legitimate OAuth flows instead of simply stealing passwords. Here is what SMBs and government contractors should review now.
Recent Linux Kernel Exploits Make Attack Surface Reduction a Practical Priority
Recent Linux kernel exploit discussions show why SMBs and government contractors should reduce unused modules and services, not just wait for patches.