Category Archive
Red Teaming
10 reports·All intelligence
Offensive operations and adversary simulation — tradecraft, tooling, and the techniques red teams use in the field.
Showing 1–10 of 10 reports
I Got In Without A Badge Easy!? Social Engineering Strategies.
People assume social engineering is all charm and quick thinking. But real operators know the truth:Preparation is the payload.Execution is just the final click. This is how I walked into a secured corporate building twice without a badge, without clearance, and without triggerin
THIS WEEK IN SECURITY: LOOP DOS, FLIPPER RESPONDS, AND MORE!
by: Jonathan Bennett Here’s a fun thought experiment. UDP packets can be sent with an arbitrary source IP and port, so you can send a packet to one server, and could aim the response at another server. What happens if that response triggers another response? What if you could cra
Bypassing EDRs With EDR-Preloading
READ ARTICLE Marcus Hutchins Previously, I wrote an article detailing how system calls can be utilized to bypass user mode EDR hooks. Now, I want to introduce an alternative technique, “EDR-Preloading”, which involves running malicious code before the EDR’s DLL is loaded into the
Detecting API endpoints and source code with JS Miner
Read Article DANA EPP’S BLOG Security (de)engineering for fun and profit Let’s be honest. Most APIs are naked without some sort of web app frontend calling it. These days, those apps are usually written in some sort of framework based on Javascript. With a bit of work, we can do
Book.HackTricks
To the Book! Disclaimer This book, ‘HackTricks,’ is intended for educational and informational purposes only. The content within this book is provided on an ‘as is’ basis, and the authors and publishers make no representations or warranties of any kind, express or implied, about
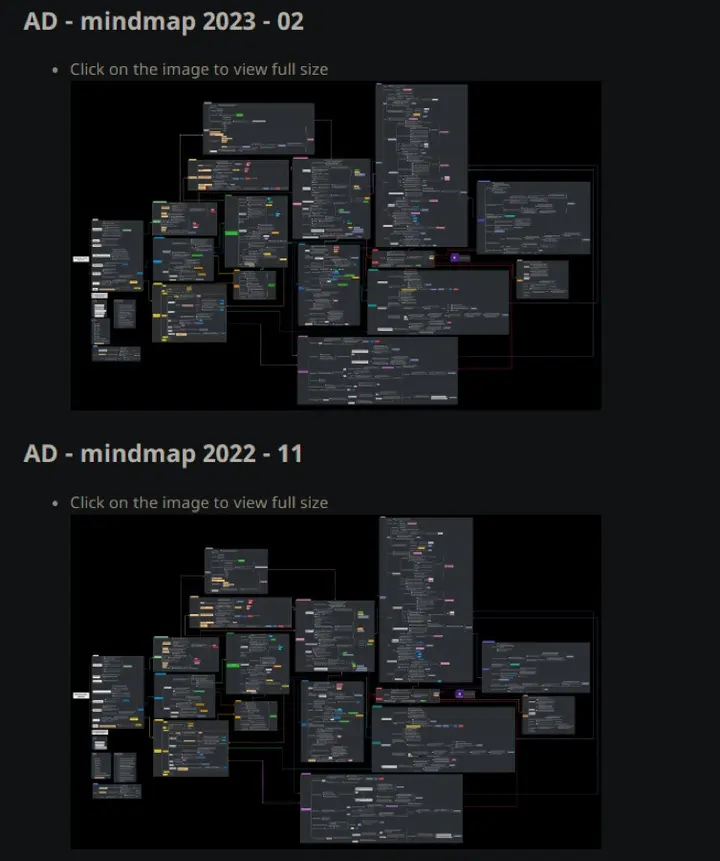
Active Directory Penetration Testing Orange Cyber-defense mind maps
Get Mind Map!
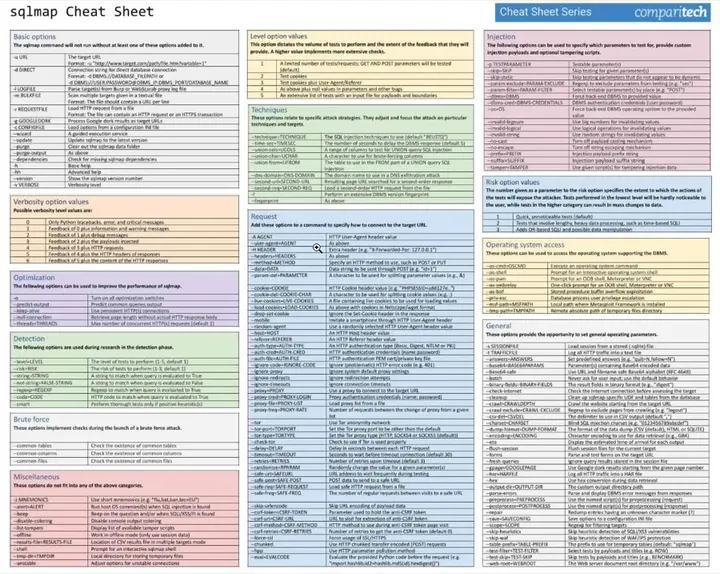
SQLmap Cheat Sheet
Link to Sheet
Announcing cvemap from ProjectDiscovery
Read Article Project Discovery Tool ManagerGitHub pdtm is a simple and easy-to-use golang based tool for managing open source projects from ProjectDiscovery. Security professionals are constantly on guard against cyber threats, especially given the rising number and sophisticatio
How to protect Evilginx using Cloudflare and HTML Obfuscation
Read Article Using a combination of Cloudflare and HTML Obfuscation, it is possible to protect your Evilginx server from being flagged as deceptive and so increase your chances of success on Red Team and Social Engineering engagements. Anyone who has tried to run a Social Enginee