Ransomware defense usually starts with a familiar mental model: catch the loader, block the encryptor, isolate the host, and recover from backups. Kaspersky's latest incident response write-up on PAYLOAD ransomware is a useful reminder that this model is incomplete.
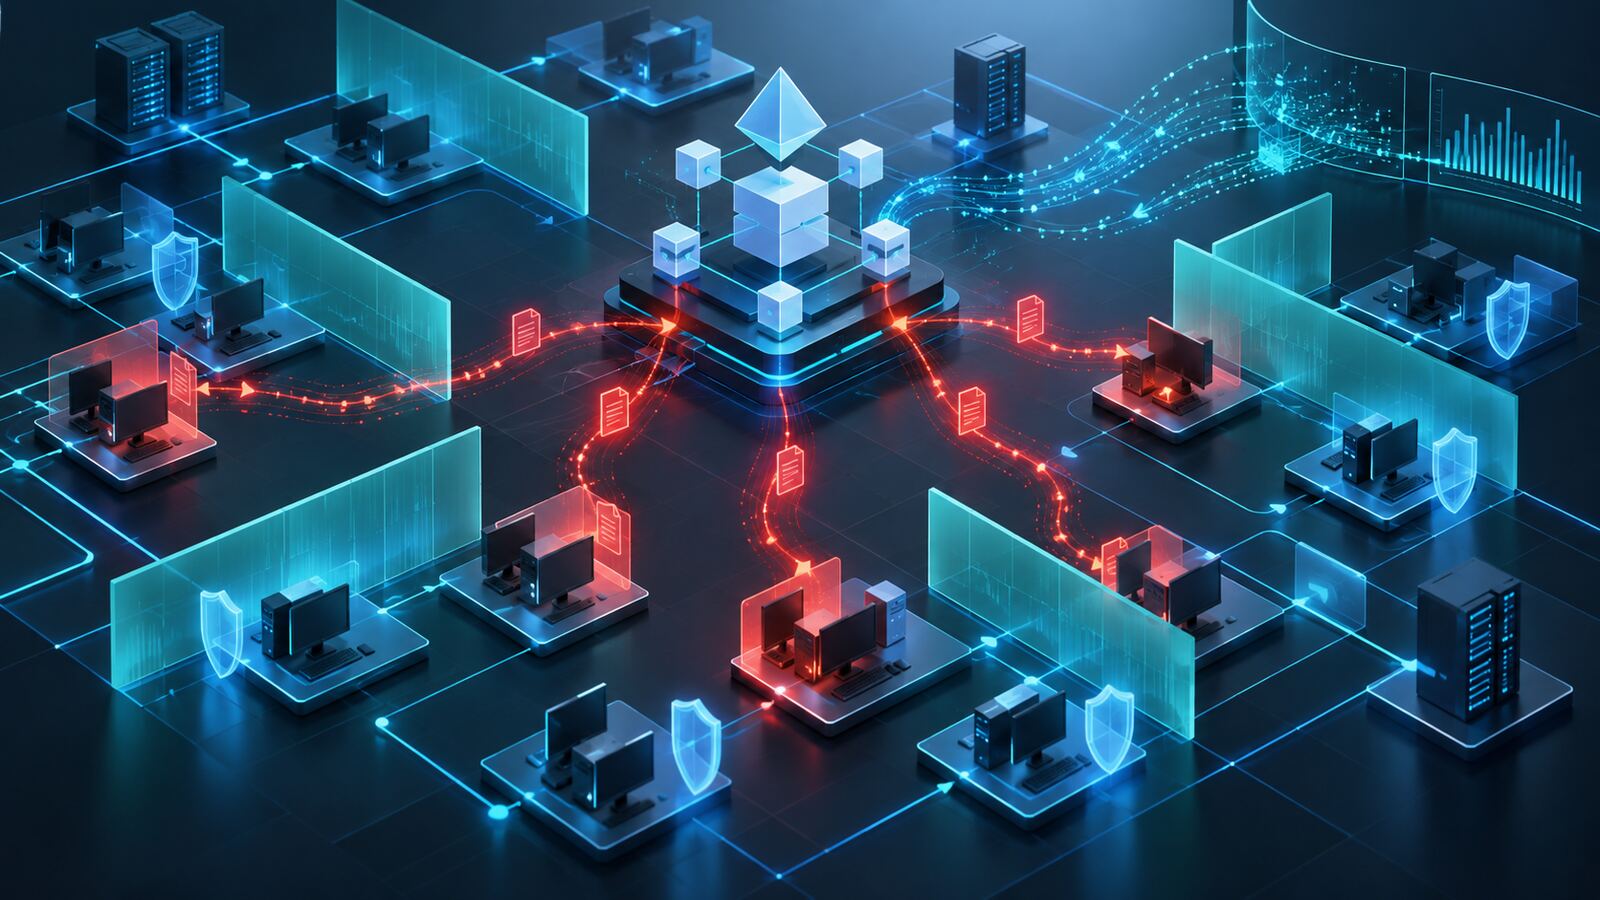
In the incident Kaspersky described, the attacker did not need to drop a Windows ransomware binary across the environment. Instead, after gaining domain-level control, the actor created malicious Active Directory Group Policy Objects and linked them at the domain root. That policy-based impact changed lock screens and wallpapers, displayed ransom messaging, copied ransom notes through SYSVOL, disabled the local administrator account, and separately turned off Windows Firewall profiles across endpoints.
That is the real lesson: Group Policy is not just configuration plumbing. It is a Tier-0 control plane. If an attacker owns it, they can push trusted, high-privilege changes to the fleet using the same mechanism administrators rely on every day.
What Kaspersky reported
Kaspersky's Global Emergency Response Team investigated an April 2026 incident at a manufacturing organization in the Middle East. The attacker authenticated through FortiGate SSL VPN with a valid but compromised domain credential, then reached domain admin-equivalent control in Active Directory.
From there, the actor created a malicious GPO named PAYLOAD and linked it at the domain root. A second GPO, named win Firewall Off, disabled Windows Firewall across domain, private, and public profiles. Kaspersky also observed data exfiltration from file servers and other systems, and later publication of stolen data on the dark web.
The PAYLOAD activity was disruptive, but the Windows endpoint impact was not classic file encryption. Kaspersky reported no Windows files encrypted, no resident Windows malware, no endpoint persistence, and no malicious process running at the time of analysis. The visible impact came from malicious policy configuration living inside Active Directory and SYSVOL.
Why this matters
This is the kind of attack path that can slip past organizations that only hunt for ransomware executables. If a defender is waiting for an unknown binary, mass file rename activity, or an encryption process, a GPO-driven disruption may not trip the expected alarms until machines reboot or refresh policy and the damage becomes visible.
For SMBs and government contractors, this is especially relevant because Active Directory often remains the identity backbone for workstations, file shares, VPN access, endpoint management, and line-of-business systems. A single domain-root-linked GPO can create domain-wide blast radius faster than most security teams can manually inspect endpoints.
There is also a compliance angle. Contractors handling regulated government data are expected to protect identity systems, enforce access control, audit privileged activity, and maintain recovery procedures. Group Policy changes that disable host firewall protections, weaken admin access, or distribute unauthorized content are not just operational problems. They are control failures.
Defensive takeaways
- Treat Group Policy as Tier-0. Domain-root GPO linking, SYSVOL writes, and Group Policy Creator Owners membership should be reviewed with the same seriousness as domain admin changes.
- Monitor GPO creation and linking. Alert on new GPOs, deleted GPOs, domain-root links, changes to high-impact GPOs, and unusual modification outside approved change windows.
- Watch SYSVOL like a deployment channel. Ransom notes, scripts, batch files, executables, policy preference XML changes, and unexpected images or documents in SYSVOL should be investigated quickly.
- Baseline critical policy settings. Track changes to Windows Firewall state, local administrator account status, logon banners, startup scripts, scheduled tasks, Defender exclusions, and lock-screen or wallpaper policies.
- Separate who can create GPOs from who can link them. GPO creation rights are dangerous when combined with link rights at the domain or high-value OU level.
- Require MFA and conditional access for VPN. The incident began with a valid VPN login. Valid credentials remain one of the most reliable paths into AD environments.
- Keep recoverable GPO backups. Backups should include known-good GPOs, SYSVOL content, and documentation for emergency unlink/rollback procedures.
- Exercise AD recovery. Tabletop the scenario where the attacker controls policy, disables controls, and uses normal admin infrastructure as the delivery mechanism.
Hunting ideas
Defenders should look for sudden or suspicious changes in these areas:
- New GPOs linked at the domain root or broad workstation OUs
- GPO display names that look generic, rushed, or operationally suspicious
- Unexpected files staged under SYSVOL and referenced by policy
- Policy changes that disable Windows Firewall or weaken endpoint controls
- Legal notice caption/text changes, forced wallpaper changes, or lock-screen image changes
- Group Policy Preference changes that copy files to user desktops or drive roots
- Event activity around privileged group membership, delegated GPO rights, or domain-root link permissions
The important shift is to hunt the administrative mechanism, not just the malware. In PAYLOAD's case, the attacker used trusted infrastructure to carry the impact.
Bulwark Black assessment
PAYLOAD is not just another ransomware story. It is a control-plane story. The actor used Active Directory to turn normal Windows management into an impact mechanism, while data theft supplied the extortion pressure.
The durable fix is not a single endpoint rule. Organizations need privileged-access hygiene, VPN hardening, GPO change monitoring, SYSVOL visibility, AD backup discipline, and practiced rollback procedures. If Group Policy can touch every workstation, it deserves monitoring and recovery planning equal to its blast radius.
Source: Kaspersky Securelist — PAYLOAD ransomware attacks through Active Directory GPO