

Attackers do not need to break into a vendor to abuse that vendor's trust. Sometimes they only need to rank a convincing fake download page high enough that a hurried user clicks it.
BleepingComputer reported on a malware campaign uncovered by LastPass and Delphos Labs that used SEO-optimized GitHub repositories to impersonate LastPass Authenticator and dozens of other software brands. The fake repositories redirected victims through attacker-controlled infrastructure and ultimately delivered a previously undocumented infostealer that researchers track as Rapuncel.
The campaign is useful to defenders because it combines several trends that keep showing up in real intrusions: search-engine poisoning, brand impersonation, trusted developer platforms, signed driver abuse, DLL sideloading, and credential theft from browsers, wallets, chat apps, and Windows Credential Manager.
What was reported
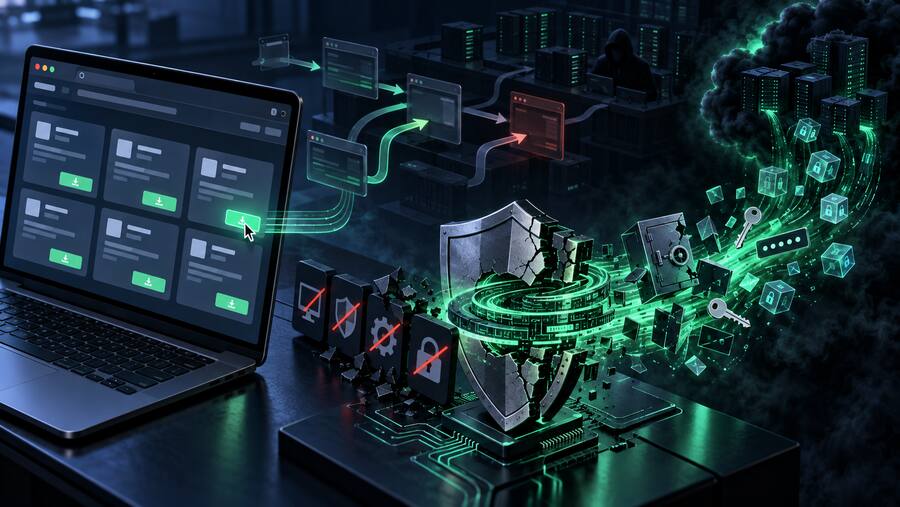
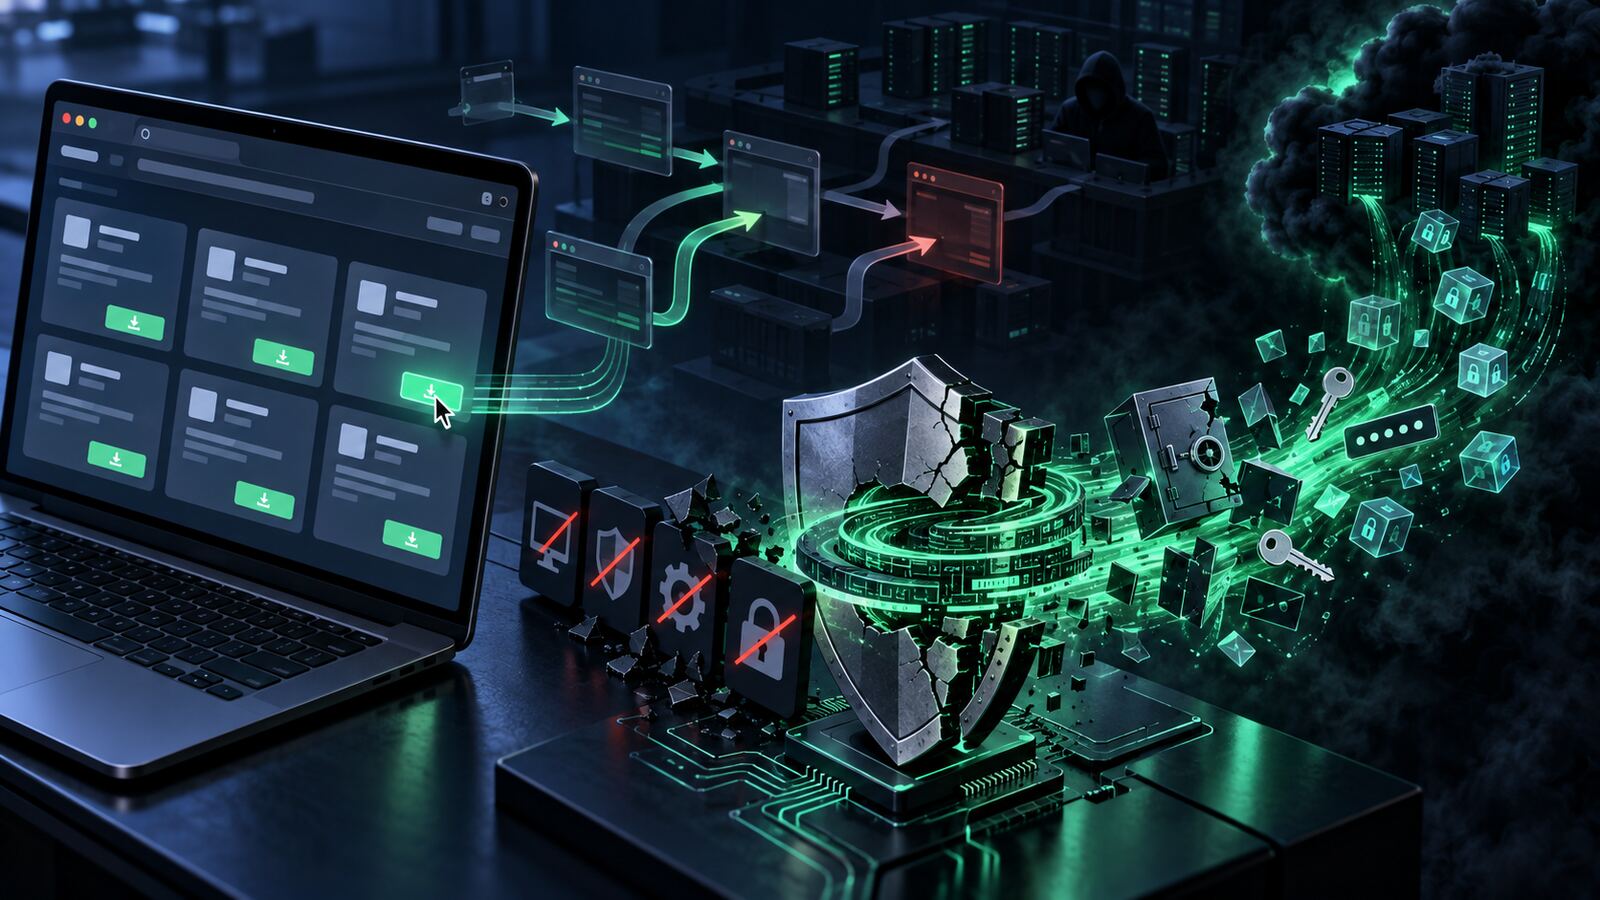
According to the LastPass and Delphos analysis, the attack began with fraudulent GitHub organizations and GitHub Pages sites designed to look like legitimate software download portals. The lure pages used trust signals such as security-themed badges and download animations while silently routing users through redirect infrastructure.
The downloaded archive was intentionally padded to a large size, a common evasion tactic because some scanners and mail/security gateways skip or reduce inspection on oversized files. Inside the archive, the attacker abused a renamed copy of Microsoft's Visual Studio CoreCLR debugger to sideload a malicious DLL.
Once executed, the loader installed a Microsoft-attested kernel driver disguised as an NVIDIA-style component. Researchers said the driver could terminate a hardcoded list of 145 antivirus and EDR processes. With endpoint defenses suppressed, Rapuncel collected browser credentials, cryptocurrency wallet data, Discord, Steam, Telegram session material, Windows Credential Manager contents, sensitive-looking documents, screenshots, and system details.
Why it matters
This is not just another fake installer story. The operational lesson is that software acquisition has become an identity and endpoint security problem. A user searching for a familiar tool, especially under time pressure, can be routed into infrastructure that looks close enough to the real thing to pass a quick visual check.
For SMBs and government contractors, this matters because small teams often allow users and administrators to download utilities directly from search results, GitHub repositories, forums, or vendor-looking pages. That habit creates a gap between strong endpoint tooling and weak software provenance. If the installer is allowed to run with elevated privileges, a signed kernel driver can turn one bad download into a full compromise review.
Defensive takeaways
- Do not treat GitHub as an official download source by default. If a vendor normally distributes through its own domain, app store, package manager, or signed enterprise channel, require that path.
- Block or warn on ad/promoted and newly observed download domains. Search-result abuse is a delivery mechanism. DNS filtering, browser isolation, and secure web gateways should make risky download paths noisy.
- Require publisher and hash validation for administrative tools. Signed does not always mean safe. Validate expected publisher, file path, hash, and source together.
- Use application control for user-writable execution paths. Fake installers often rely on downloads, temp folders, archives, and local staging directories. Those paths should not be trusted execution zones.
- Monitor for security-tool tampering. Sudden termination of EDR/AV processes, new kernel drivers, service creation, or Protected Process Light bypass behavior should trigger immediate containment.
- Hunt for suspicious driver loads. Pay attention to newly installed drivers with odd naming, GPU-themed disguises, unexpected service names, or Microsoft-attested but business-unrelated components.
- Rotate credentials after suspected infostealer execution. Browser passwords, session cookies, chat tokens, wallet material, and Windows Credential Manager secrets should be treated as exposed.
Bulwark Black assessment
Rapuncel is a reminder that endpoint defense cannot stop at malware detection. The stronger control is a trusted software acquisition process: approved sources, managed browsers, least-privilege installs, application control, and driver-load monitoring.
Organizations should also separate “employee convenience downloads” from administrator workflows. If an admin needs an authenticator, VPN client, remote support utility, or cloud tool, the install path should be documented and repeatable. A search engine should never be the control plane for software trust.
The practical move this week is simple: review how your team downloads common tools, block unofficial repositories for branded software, and make EDR/AV tampering a high-severity alert. If a signed driver appears at the same time security tools disappear, assume the machine is already in the hands of the attacker.
Sources: BleepingComputer; LastPass and Delphos Labs technical report.