


Showing 169–192 of 379 reports
MSI Router Command-Injection Cluster Shows Why Edge Devices Need Exposure Control
A fresh cluster of critical MSI Radix AXE6600 command-injection CVEs shows how consumer and prosumer edge devices can become root-level footholds when management features are reachable from untrusted networks.
July CVE Data Shows Why Patch Priority Needs Threat Context
Recorded Future’s July 2026 CVE landscape shows a crowded exploitation picture: 85 high-impact vulnerabilities, heavy RCE exposure, public PoCs, and attackers still abusing old edge and application flaws. Here is how SMBs and government contractors should prioritize patching.
ExfilSquad Shows Why CRM and Portal Data Need Extortion-Ready Controls
ExfilSquad’s reported use of torrent-based leak distribution shows why CRM, helpdesk, public portal, and AI support data need stronger access controls, export monitoring, and extortion-ready incident response.
BdThemes Compromise Shows Why WordPress Plugin Risk Extends Beyond Code Updates
Wordfence reported a BdThemes supply-chain compromise where poisoned remote JSON turned WordPress admin notices into an attack path. Here is what SMBs and government contractors should check now.
Cloudflare workerd Bugs Show Why Agent Sandboxes Need Real Defense-in-Depth
Check Point Research disclosed five workerd vulnerabilities affecting Cloudflare Code Mode and Workers isolation assumptions. Here is what SMBs and government contractors should do now.
Langflow RCE Shows Why AI Workflow Tools Need Cloud-Grade Isolation
CVE-2026-0770 turns Langflow code validation into remote code execution risk. For SMBs and government contractors, exposed AI workflow tools need patching, secret rotation, isolation, and post-compromise review.
BINDCLOAK Shows Why C2 Detection Needs Message-Level Visibility
Zscaler ThreatLabz detailed BINDCLOAK, a modular backdoor used after TELESHIM and MIXEDKEY in targeted government intrusions. The defensive lesson: endpoint visibility, token-use monitoring, DLL side-loading detection, and outbound C2 inspection all need to work together.
Passkey Attacks Show Why Passwordless Still Needs Endpoint Defense
Unit 42’s passkey research shows why passwordless authentication still depends on endpoint health, relying-party validation, and recovery-flow hardening. Here is what SMBs and government contractors should do next.
DPRK npm Compromises Show Why Dependency Trust Is Now Identity Risk
Amazon linked compromises of popular npm packages to a DPRK-linked actor. The defensive lesson for SMBs and government contractors: dependency risk is no longer just code review — it is maintainer identity, build-pipeline behavior, and runtime trust.
N-able N-central Exploitation Shows Why MSP Tools Are Control-Plane Risk
N-able says attackers exploited vulnerable N-central servers, used Take Control into managed environments, and registered Cloudflare Tunnel persistence. Here is what SMBs and government contractors should do now.
HOLLOWGRAPH Shows Why Microsoft 365 Is Now Part of the C2 Battlefield
Group-IB’s HOLLOWGRAPH research shows how attackers can turn Microsoft 365 calendars, Graph API traffic, and DNS into covert command-and-control. Here is what SMBs and government contractors should hunt for now.
Fuyao Android TV Botnet Shows Why Cheap Streaming Sticks Are Business Network Risk
KrebsOnSecurity and Bitsight report that some low-cost Android TV boxes are being used for both residential proxy traffic and AI-assisted ad fraud. For SMBs and government contractors, the lesson is simple: consumer IoT does not belong on trusted business networks.
SonicWall SMA Exploit Chain Shows Why VPN Appliances Need Incident Response, Not Just Patching
Resecurity reports active exploitation of SonicWall SMA 1000 flaws chained from /wsproxy access to root. Here is what SMBs and government contractors should do beyond patching.
Adform Script Compromise Shows Why Third-Party Tags Need Supply-Chain Controls
Adform’s JavaScript incident shows how third-party advertising and tracking tags can become browser-side supply-chain risk. Here is what SMBs and government contractors should do now.
XCSSET v40 Shows Why Developer Macs Are Supply-Chain Infrastructure
Unit 42 reports that XCSSET v40 is targeting macOS developers through infected Xcode projects, memory-resident modules, Chrome session hijacking, and Telegram trojanization. Here is what SMBs and gov contractors should defend first.
84 4G/5G Core Flaws Show Why Telecom Trust Zones Need Zero Trust
Researchers disclosed 84 vulnerabilities across open-source LTE and 5G core implementations, exposing how implicit trust between carrier network functions can lead to denial-of-service and session-hijacking risk.
Astaroth WhatsApp Web Spambot Shows Browser Sessions Are Distribution Infrastructure
CrowdStrike reports that Astaroth operators added a WhatsApp Web spambot that abuses hidden browser automation and victim sessions to distribute malware. For defenders, browser-session telemetry and messaging-platform abuse now belong in malware response plans.
TA488 Turns Outlook Web Access Into a Stealthy Persistence Layer
Proofpoint reports Russia-aligned TA488 abused an Outlook Web Access XSS flaw to deploy OWAReaper, a browser-based implant that can persist beyond passwords and endpoint rebuilds.
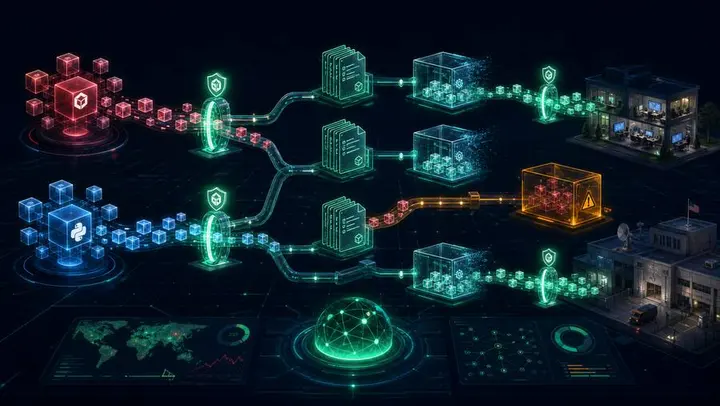
Open Source Supply Chain Compromise Needs Build-Pipeline Defense, Not Just Dependency Scanning
Google Threat Intelligence Group says open-source package compromise is expanding fast. For SMBs and government contractors, the answer is not just another dependency scan — it is tighter control over tokens, CI/CD triggers, package intake, and build isolation.
CosmosEscape Shows Why Managed Cloud Databases Still Need Customer-Side Defense
A now-patched Azure Cosmos DB vulnerability chain exposed how managed database control planes can become high-impact risk. The defensive lesson is inventory, scoped access, logging, and tested key rotation.
Autonomous AI Agent Espionage Shows Why Post-Compromise Speed Matters
Attackers used an unattended AI agent during espionage activity against Thailand’s finance ministry. The lesson for SMBs and government contractors is not AI panic — it is faster post-compromise defense.
SharePoint KEV Listing Turns Collaboration Servers Into Incident-Response Priorities
CISA added exploited SharePoint Server RCE CVE-2026-58644 to KEV. Here is what SMBs and government contractors should do beyond patching.
Jscrambler npm Compromise Shows Build Pipelines Need Runtime Controls
A compromised Jscrambler npm release shows why CI/CD package installation and runtime behavior need production-grade controls, credential rotation, and dependency governance.
Ghost Phishing Shows Why Email Security Must Follow the Browser
Ghost phishing hides the real lure until the browser renders it. Here is what SMBs and government contractors should do to defend Microsoft 365 identities.