


Showing 121–144 of 379 reports
Vault Secrets Operator Flaw Shows Why Kubernetes Controllers Need Egress Control
CVE-2026-8715 in HashiCorp Vault Secrets Operator shows how tenant-controlled custom resources can become a Kubernetes control-plane risk when privileged controllers lack tight input and egress boundaries.
PackClient Shows Why Phishing Defense Needs Execution Controls
Proofpoint reported TA4922 using PackClient in tax-themed phishing campaigns. The defensive lesson for SMBs and government contractors is to control the execution chain after the click.
macOS Screen Sharing Exploitation Shows Why Remote Access Needs Exposure Control
CVE-2026-65400 is being exploited against internet-exposed Macs running Screen Sharing. For SMBs and government contractors, this is a remote-access exposure problem, not just an Apple patch problem.
AI-Assisted Exploits Make OT Reachability the Real Control
AI-assisted exploit development is lowering the skill barrier for attacks against factory controllers. For SMBs and government contractors, the practical defense is shrinking what can reach OT assets.
White-Label Router Backdoors Show Why Edge Provenance Matters
ZBT white-label router backdoors are a reminder that SMBs and government contractors need real edge-device provenance, egress monitoring, and procurement controls.
PaperCut Zero-Day Exploitation Shows Why Print Servers Need Edge-Asset Discipline
PaperCut warned that NG/MF servers are being exploited in zero-day attacks. For SMBs and government contractors, public print-management servers need the same containment, patching, and compromise-assessment discipline as other edge assets.
AI Infrastructure Is Becoming a Control Plane Attack Surface
Microsoft observed attackers targeting AI gateways, RAG platforms, and workflow orchestrators. For SMBs and government contractors, AI infrastructure now needs control-plane security discipline.
QScan and QTRouter Show Why Proxy Infrastructure Is an Espionage Force Multiplier
The FBI/DOJ disruption of QScan and QTRouter shows how China-linked operators turn reconnaissance and proxy routing into reusable espionage infrastructure.
vCenter Exploitation Shows Patching Alone Is Not Incident Response
Active exploitation of CVE-2026-59310 shows why VMware vCenter patching must be paired with compromise assessment, egress controls, and management-plane segmentation.
Edge Infrastructure Convergence Shows Why Perimeter Devices Need Their Own Patch SLAs
SentinelOne and Tenable found that state-backed actors and ransomware crews converge on the same perimeter products. For SMBs and government contractors, edge devices need dedicated patch SLAs, exposure monitoring, and compromise review.
Signed ClickOnce Lures Show Why Hiring Workflows Need Endpoint Guardrails
A fake Web3 interview chain used signed ClickOnce delivery to deploy credential stealers and a Go hVNC RAT. Here is what SMBs and government contractors should tighten now.
ShieldBreak Shows Why Endpoint Protection Needs Compensating Controls
CVE-2026-69414 is a Microsoft Defender privilege-escalation zero-day with public PoC and no patch yet. Here is how defenders should handle the exposure gap.
AI-Enabled Malware Still Behaves Like Malware
Unit 42’s telemetry shows most AI-enabled malware remains experimental, but the real risk is faster iteration and AI-branded delivery. Defenders still win by watching behavior, identity, signing, and execution.
Private APNs Are Becoming OT Attack Paths
CERT Polska’s energy-sector follow-up shows how private APN connectivity can become an OT pivot path. Private LTE and 5G need segmentation, inventory, and monitoring—not blind trust.
vCenter Exploitation Shows Why Control Planes Need Containment
Active exploitation of CVE-2026-59310 shows why vCenter needs more than fast patching: control-plane containment, egress limits, and compromise assessment matter.
Apollo Breach Shows Why Helpdesk Vishing Is a Cloud-Control Problem
Apollo confirmed a cloud breach after helpdesk-style social engineering. The defensive lesson: treat MFA resets, passkey enrollment, and SaaS downloads as control-plane events.
BTR.sys Shows Why Trusted Security Drivers Need Behavioral Monitoring
Check Point Research shows how Microsoft Defender’s boot-time remediation driver can be repurposed for privileged file and registry operations. The defensive lesson is simple: monitor trusted security components by behavior, not signature alone.
WeedHack Shows SEO Poisoning Is Malware Delivery Infrastructure
McAfee says WeedHack is still using fake gaming sites, SEO poisoning, Discord links, MediaFire, and GitHub-style trust signals to deliver malware. The same playbook can hit business users searching for tools and downloads.
AI Agent Incidents Need Task-Scoped Incident Response
AI agents need incident response that maps credential use back to task authorization. Here is how SMBs and government contractors can reduce blast radius with task-scoped access, logging, and containment runbooks.
SDLC Supply-Chain Attacks Show Why Developer Tools Need Runtime Controls
Attackers are targeting developer endpoints, CI/CD pipelines, package managers, and cloud runtime—not just finished applications. Here is how SMBs and government contractors can reduce SDLC supply-chain blast radius.
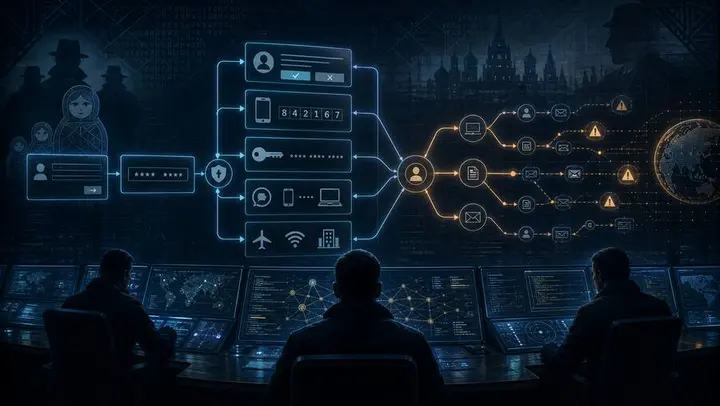
Russian Auth-Flow Phishing Shows MFA Can Be Bypassed Without Exploits
Russian-linked clusters are abusing app passwords, OAuth consent, device-code login, WhatsApp linking, and captive portals. The defense is visibility and governance around authorization flows—not just MFA at login.
Fake AI Tools Show Brand Trust Has Become Malware Delivery
Sophos X-Ops found attackers repeatedly impersonating AI brands with fake installers, malicious extensions, phishing lures, and AI-assisted tooling. The near-term defense is not exotic: approved sources, browser governance, endpoint telemetry, DNS controls, token hygiene, and clear AI software rules.
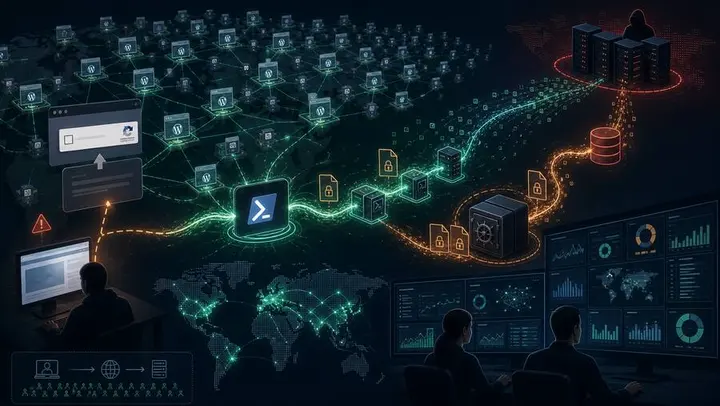
StopAndProtect Shows Why WordPress Sites Are Attack Infrastructure
Check Point Research exposed StopAndProtect, an operation abusing thousands of compromised WordPress sites for ClickFix delivery, malware staging, command routing, victim logging, data theft, and ransomware. The practical lesson: public websites need the same ownership, telemetry, and incident-response discipline as other production infrastructure.
MacSync Stealer Shows Why Behavioral Pivots Beat Rotating Domains
Microsoft Defender Experts expanded MacSync Stealer tracking from a small domain set to 30+ related domains by correlating durable endpoint and network behaviors. For defenders, the lesson is to hunt the attack chain—not just the rotating infrastructure.