


Intel Feed
Cyber Threat IntelligencePage 6
Reports
Reporting archive — page 6
Showing 121–144 of 611 reports
Cyclops Blink on Cisco FMC Shows Why Edge Appliances Need Compromise Review
Sophos CTU and Cisco Talos reporting on Cyclops Blink activity against Cisco Secure FMC shows why edge security appliances need compromise review, not just emergency patching.
Revolut Breach Shows Why Data Requests Need Verification Controls
Revolut confirmed sensitive customer data was disclosed after fraudulent requests appeared to come from a legitimate government agency email domain. Here is what SMBs and government contractors should tighten now.
Check Point VPN Flaws Show Why Remote Access Needs Emergency Patch Discipline
Dutch NCSC warns exploitation is expected soon for two critical Check Point VPN RCE flaws. Here is what SMBs and government contractors should patch, restrict, and review now.
Mirth Connect Flaws Show Why Healthcare Middleware Needs Compromise Review
CISA warned that NextGen Mirth Connect SQL injection and XXE flaws can expose data or disrupt healthcare integration workflows. Here is how SMBs, healthcare vendors, and government contractors should respond.
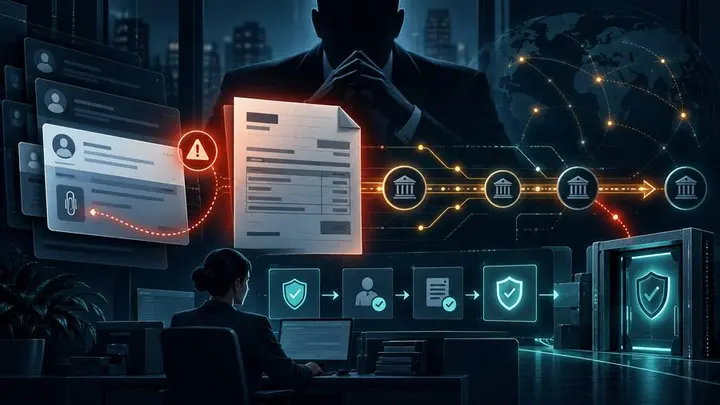
AI Invoice Fraud Shows Why Finance Needs Verification Controls
Microsoft observed a million-email AI-assisted executive impersonation campaign pushing fabricated invoices and ACH payment requests. For SMBs and government contractors, the fix is not just better spam filtering — it is finance workflow verification.
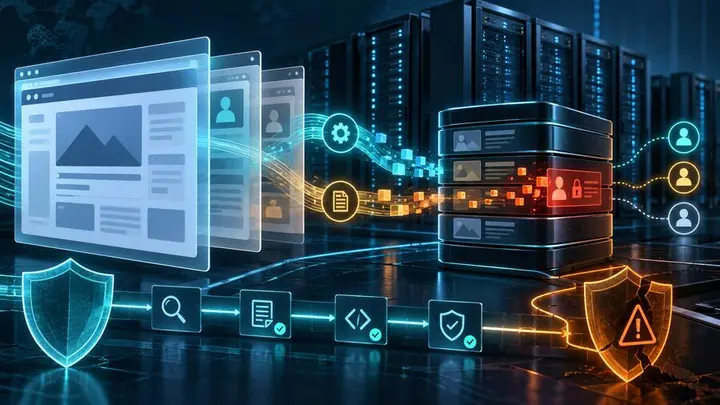
Angular SSR Flaws Show Why Hydration and Edge Caches Need Security Review
New Angular SSR advisories show how hydration, transfer-state caching, URL normalization, and server-side credentials can become application security boundaries.
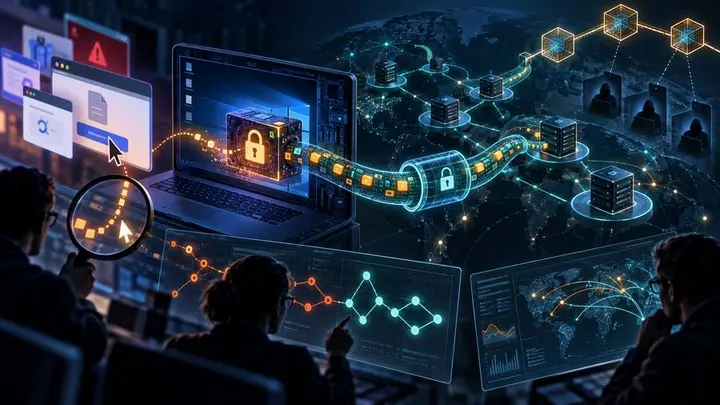
SloppyRAT Shows Why Ransomware Defense Has to Watch the Whole Infection Funnel
Zscaler ThreatLabz analysis of SloppyRAT shows why defenders need to detect the full ransomware precursor funnel, not just the final payload.
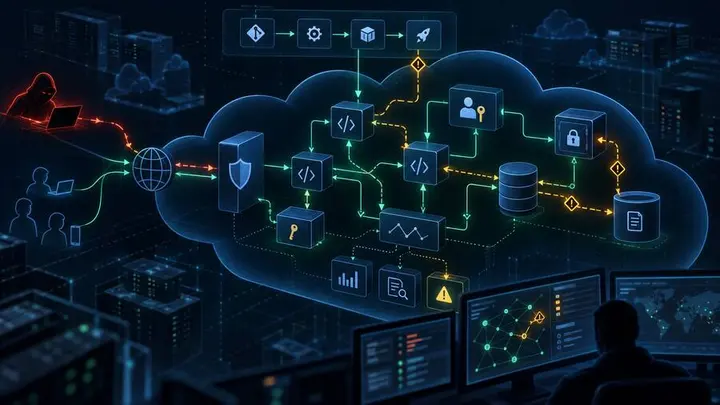
Cloud Web Apps Need Attack-Path Defense, Not Just App Scans
Microsoft’s cloud web applications threat matrix is a useful reminder: modern web app risk spans code, CI/CD, managed identities, serverless triggers, storage, and logs.
THost9 Shows Why Exposed Android Debug Interfaces Need Compromise Review
Dark Atlas research on THost9 shows how exposed ADB and Redroid debug services can become a malware propagation path. Here is what SMB and government-contractor defenders should review now.
OfferLoader Shows Why Commodity Malware Needs Funnel-Aware Defense
Unit 42 exposed a pay-per-install operation using YouTube gaming lures and SEO poisoning. The lesson: suspicious installers need full compromise review, not quick cleanup.
Apache Impala Flaws Show Why Data Platforms Need Zero-Trust Controls
Apache Impala 4.5.2 fixes a critical SAML authentication bypass plus SSRF and RCE paths. The lesson: analytics platforms need identity, egress, and privilege controls.
ChatGPT Sandbox Leak Shows Why AI Agents Need Tenant Isolation
Check Point Research disclosed a now-remediated ChatGPT sandbox isolation issue. The lesson for SMBs and government contractors: AI agents need tenant isolation, least privilege, and visible approval controls.
JetBrains IDE Flaws Show Why Developer Workstations Need Trust Boundaries
JetBrains IntelliJ IDEA 2026.2.2 fixes high-severity Remote Development and Dev Container flaws that show why developer workstations need patching, isolation, and credential discipline.
Fileless PHP Rootkit Shows Why BIG-IP Incidents Need Process-Level Hunting
SophosLabs analysis of a BIG-IP APM-linked PHP web server rootkit shows why defenders need post-patch compromise review, process-level hunting, and edge appliance rebuild discipline.
OWAReaper Shows Why Exchange Mailboxes Need Post-Patch Compromise Review
Resecurity’s OWAReaper report shows why on-prem Exchange response cannot stop at patching: defenders need mailbox-permission audits, token revocation, OWA exposure control, and post-patch compromise review.
Apache Ant Path Traversal Shows Why Build Pipelines Need Sandboxes
Apache Ant CVE-2026-78254 is moderate on paper, but CI/CD context makes arbitrary file overwrite worth treating as build-pipeline integrity risk.
Teams Helpdesk Impersonation Shows Why Remote Support Needs Guardrails
Microsoft’s Teams helpdesk impersonation case shows why remote support sessions need verification, tool control, user-writable execution limits, and WinRM monitoring.
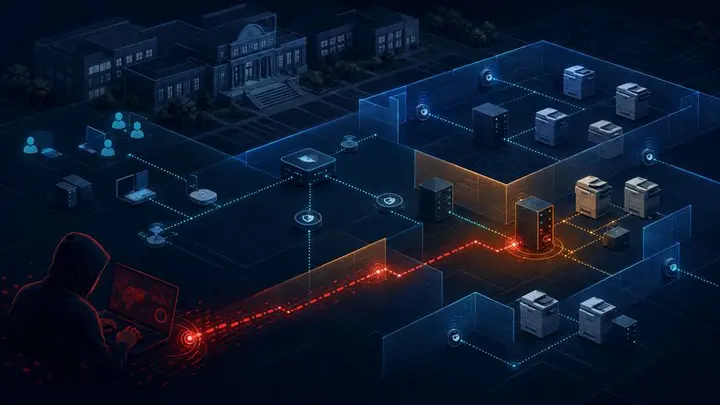
PaperCut RCE Shows Why Print Servers Need Compromise Review
Active exploitation of PaperCut NG/MF vulnerabilities shows why print-management servers need patching, exposure control, log review, and credential-access hunting.
Edge AI Moves the Trust Boundary Into Customer-Owned Environments
Microsoft’s edge AI guidance is a reminder that local AI systems need attestation, artifact provenance, least-privilege credentials, and deterministic policy gates before they touch sensitive data or take action.
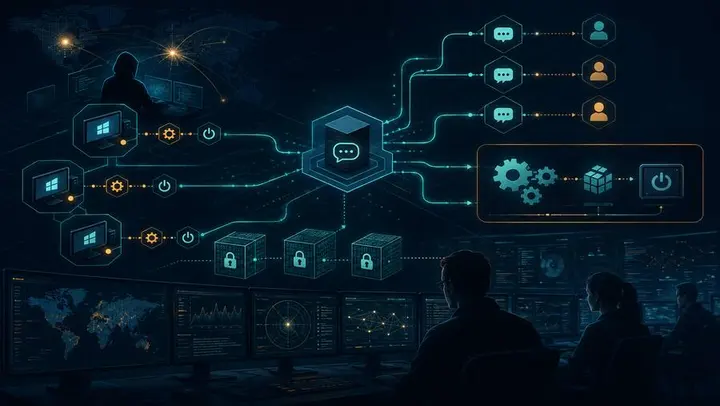
Toy Ghouls Shows Why Custom C2 Needs Protocol-Aware Monitoring
Kaspersky reports that Toy Ghouls has added custom Windows backdoors using HiveMQ MQTT and Matrix/Element-style command channels. For SMBs and government contractors, the lesson is not just malware blocking — it is protocol-aware egress control, service persistence review, and post-compromise valida
Ted Backdoor Shows Why Edge Load Balancers Need Compromise Review
Rapid7’s DPRK-attributed ted backdoor and curlRAT research shows why HAProxy, SSH, cron, and other Linux edge services need integrity checks, centralized logs, and post-compromise review.
Nisos DPRK Investigation Shows Why Remote Hiring Is a Security Control
Nisos’ DPRK employment-fraud investigation shows why remote hiring, contractor onboarding, identity verification, and access control now belong in the same security conversation.
Fake Claude Opus 5 App Shows Why AI Tooling Needs Software Control
A fake Claude Opus 5 GitHub desktop app delivering RevStealer shows why AI experimentation needs approved software paths, endpoint controls, and credential-theft triage.
NodeRabbit and PollCat Show Why Developer Workstations Need Recruiting-Lure Controls
Mirage Kitten’s NodeRabbit and PollCat malware campaigns show why fake recruiter coding tests are a practical workstation, credential, and supply-chain risk for SMBs and government contractors.