


Intel Feed
Cyber Threat IntelligencePage 4
Reports
Reporting archive — page 4
Showing 73–96 of 611 reports
Browser Detection and Response Shows Why the Browser Is Now a Security Blind Spot
Zscaler argues that browser-based attacks increasingly evade traditional endpoint and network controls because key behavior happens inside the browser. Defenders should treat browser telemetry, extension control, clipboard/file movement, identity flows, and isolation policy as part of the detection-
Apache Struts REST Plugin Flaws Show Why Legacy Java Apps Need Exposure Review
Apache disclosed four Struts vulnerabilities on October 5, including an important REST plugin issue that can exhaust Java heap memory and an OGNL injection path in the legacy RESTful action mapper. Defenders should inventory exposed Struts apps, patch to 6.12.0 or 7.4.0, and verify mapper/plugin usa
ClingSTUN Shows Why IoT Edge Devices Need Real Egress Monitoring
Fortinet’s ClingSTUN research shows how compromised IoT and edge devices can abuse public STUN infrastructure to become proxy backdoors. SMBs and government contractors should treat exposed firmware, unexpected UDP/STUN traffic, and unmanaged edge devices as a real incident-response priority.
Apache Thrift 61-CVE Patch Shows Why RPC Frameworks Need Inventory
Apache Thrift 0.25.0 fixes 61 vulnerabilities across multiple language bindings. Defenders should treat this as an RPC exposure and software-inventory problem, not just another library bump.
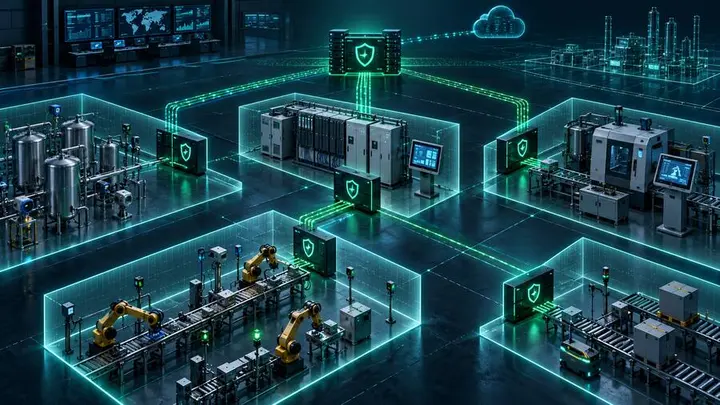
NIST OT Zero Trust Guidance Shows Segmentation Must Reach Below Level 3
NIST SP 800-82r4 brings zero trust into OT guidance, but defenders need local segmentation and access controls below Purdue Level 3 where controllers, HMIs, and engineering authority live.
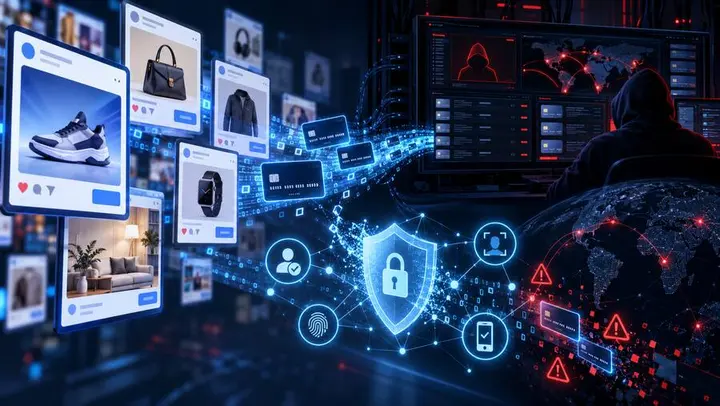
Milk Dragon Shows Social Commerce Phishing Needs Identity and Payment Controls
Group-IB’s Milk Dragon research shows how shopping-discount lures on social media can become adversary-in-the-middle phishing and payment-card theft. SMBs and government contractors should treat social commerce fraud as an identity, brand, and payment-risk problem — not just user awareness.
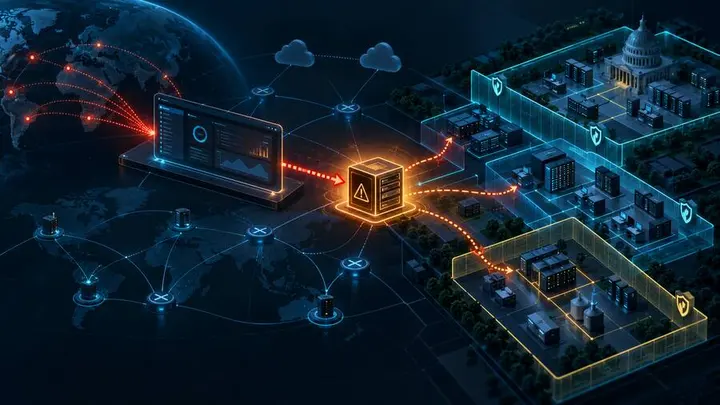
Cisco SD-WAN Auth Bypass Shows Edge Control Planes Need Emergency Review
Cisco says CVE-2026-76504 is being actively exploited against Catalyst SD-WAN Manager, giving unauthenticated attackers admin-level API access. Edge management systems need emergency patching, exposure reduction, and compromise review.
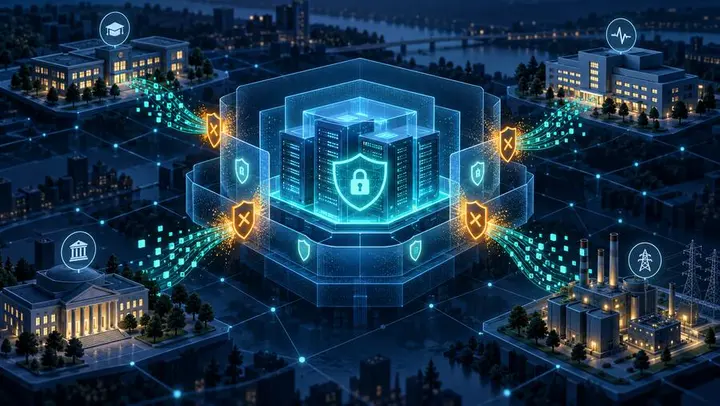
Ransomware Data Theft Surge Shows Why Exfiltration Defense Comes First
Zscaler ThreatLabz reports ransomware data theft surged 275.8% year over year, with government, healthcare, education, and utilities facing larger exfiltration events. Defenders need controls that stop data movement before encryption begins.
Live Exposed Credentials Show Why Secret Scanning Must End in Revocation
Truffle Security found more than half a million live credentials in public GitHub repositories. For SMBs and government contractors, the lesson is clear: secret scanning is not remediation until access is revoked and verified.
Antino Backdoor Shows Why Microsoft 365 C2 Needs Cloud-Aware Detection
Cisco Talos reports China-nexus UAT-11587 used the Antino backdoor with Outlook and OneDrive as command-and-control channels. Here is what SMB and government-contractor defenders should monitor.
Session Cookie Bypass Shows Why SSO Is Not the Whole Trust Boundary
Resecurity found an application where predictable session-cookie signing bypassed Entra ID SSO and MFA. Here is what SMB and government-contractor defenders should check.
Warlock Ransomware Shows SharePoint Is Still Critical Infrastructure Risk
Recorded Future News and Symantec report China-nexus Warlock ransomware attacks against water, telecom, government, and university targets. Here is what SMB and government-contractor defenders should do about exposed SharePoint risk.
FortiMail Zero-Day Shows Email Security Appliances Need Incident Response
Fortinet says CVE-2026-104286 is being exploited against FortiMail. Here is how SMB and government-contractor defenders should respond beyond patching.
DragonForce TURN and MQTT Backdoors Show Why Ransomware Defense Needs Egress Visibility
Lab52 reports DragonForce-linked backdoors abusing TURN relays and MQTT for resilient command-and-control. Here is what SMBs and government contractors should monitor now.
TA419 Shows AI Policy Is Now an Espionage Phishing Target
Proofpoint reports China-aligned TA419 is targeting U.S. AI policy experts with identity impersonation and adversary-in-the-middle phishing. Here is what SMBs, law firms, universities, and government contractors should take from it.
AI Is Turning Vulnerability Triage Into a Threat-Intel Problem
Google Threat Intelligence Group says AI is increasing vulnerability discovery and n-day weaponization pressure. For SMBs and government contractors, the answer is not panic-patching everything—it is exposure-aware, intelligence-led triage.
2CLoader Shows Why Malware Loader Alerts Need Identity Response
Zscaler ThreatLabz detailed 2CLoader delivering Vidar, Remus, and XWorm. Here is why SMB and government-contractor defenders should treat loader detections as credential and identity incidents.
Zimbra CVE-2026-73570 Shows Mail Servers Need Full Incident Review
Microsoft tracked exploitation of an unauthenticated Zimbra command injection flaw. For defenders, this is a patch-and-investigate mail-server incident, not just a routine update.
RMM Phishing Turns Trusted Admin Tools Into Persistent Access
Microsoft observed phishing campaigns abusing legitimate MSP360 RMM and ScreenConnect to create redundant remote access. Here is what SMB and government-contractor defenders should monitor.
Apache MINA SSHD Auth Bypasses Show Why Embedded SSH Needs Inventory
Apache disclosed critical MINA SSHD authentication-bypass flaws affecting certain Java SSH server implementations. Here is what SMB and government-contractor defenders should check first.
Custom GPT ClickFix Shows Why AI Trust Needs Browser-to-Shell Controls
Attackers abused ChatGPT Custom GPT pages and fake verification prompts to push victims into a ClickFix-to-RAT chain. Here is what SMB and government-contractor defenders should monitor.
NetScaler Zero-Days Show Why Edge Devices Need Incident Response, Not Just Patching
Unit 42 reports active exploitation of Citrix NetScaler zero-days CVE-2026-88771 and CVE-2026-88772. Here is what SMBs and government contractors should do now.
NeedyMantis Shows Why Post-Compromise Malware Needs Full Intrusion Review
Microsoft’s NeedyMantis analysis shows why targeted malware found after initial access should trigger full intrusion review, not a simple cleanup ticket.
Python MaaS Infostealer Builder Shows Why Credential Theft Needs Behavior Controls
K7 Labs’ Python MaaS infostealer-builder research shows why defenders need behavior controls for credential theft, webhook exfiltration, persistence, and session compromise.