


Category Archive
AI (General)
54 reports·All intelligence
Bulwark Black cyber threat intelligence filed under AI (General).
Showing 1–24 of 54 reports
LiteLLM Gateway Flaws Show AI Infrastructure Needs Real Access Control
Check Point Research found LiteLLM gateway vulnerabilities that could let lower-privileged users alter runtime configuration, read files, take over admin access, or reach RCE paths. Here is what defenders should do now.
LiteLLM Gateway Flaws Show AI Proxies Need Control-Plane Security
Check Point found LiteLLM gateway vulnerabilities that could let low-privileged users tamper with configuration, read files, take over admin access, execute code, and leak provider keys. The defense is treating AI gateways like privileged infrastructure.
UAT-11985 Shows AI-Assisted Phishing Is Now Real-Time Account Takeover
Cisco Talos reported an APT campaign using AI-assisted event lures, malicious QR codes, and real-time Google AitM phishing. The defensive answer is phishing-resistant MFA, invitation verification, and identity telemetry that connects clicks to sessions.
Malicious AI Agent Skills Turn Prompt Instructions Into Supply-Chain Risk
VirusTotal found thousands of malicious AI agent skills, many carrying the attack in plain-language instructions rather than code. The defensive move is to review skills like software, sandbox agents, and monitor outbound behavior.
ARTEX AI Bank Attacks Show Agentic Tools Are Now an Incident-Response Problem
CrowdStrike found ARTEX configuration files and Claude Code histories tied to attacks on South Korean financial organizations. The lesson for defenders is not AI panic—it is faster triage, stronger application logging, and tighter controls around data-access workflows.
AI-Analysis Evasion Shows Why Malware Triage Needs Prompt Boundaries
Cisco Talos found malware families embedding natural-language instructions meant to steer AI-assisted analysis. The lesson for defenders: treat sample text as evidence, not instruction.
AI Agent Swarms Turn Security Basics Into Cost Controls
Cisco Talos warns that agentic attacks can compress reconnaissance, probing, social engineering, and exploitation. The practical defense is to make every attacker step more expensive through identity hardening, telemetry, throttling, and rehearsed response.
TA419 Shows AI Policy Is Now an Espionage Phishing Target
Proofpoint reports China-aligned TA419 is targeting U.S. AI policy experts with identity impersonation and adversary-in-the-middle phishing. Here is what SMBs, law firms, universities, and government contractors should take from it.
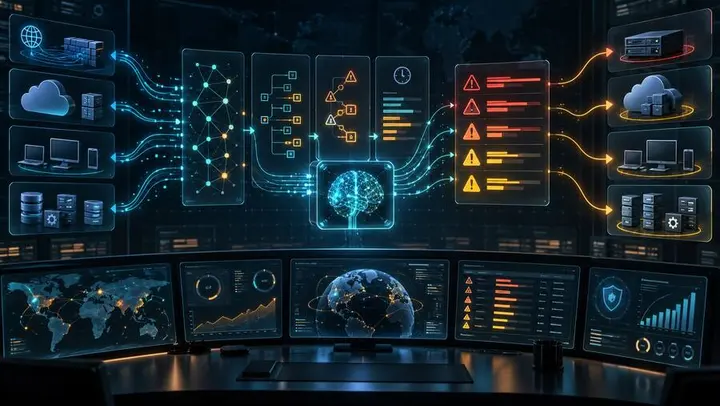
AI Is Turning Vulnerability Triage Into a Threat-Intel Problem
Google Threat Intelligence Group says AI is increasing vulnerability discovery and n-day weaponization pressure. For SMBs and government contractors, the answer is not panic-patching everything—it is exposure-aware, intelligence-led triage.
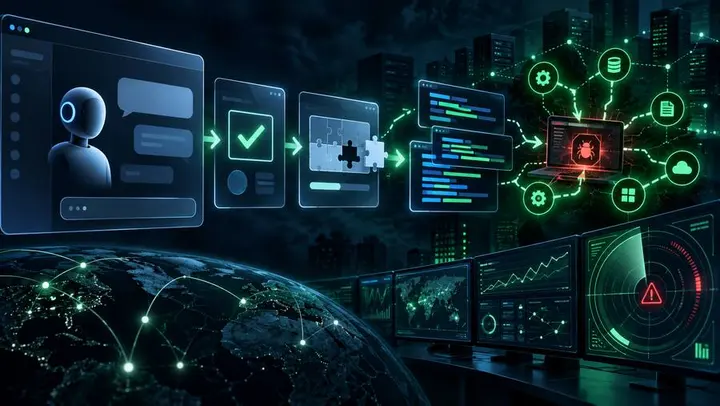
Custom GPT ClickFix Shows Why AI Trust Needs Browser-to-Shell Controls
Attackers abused ChatGPT Custom GPT pages and fake verification prompts to push victims into a ClickFix-to-RAT chain. Here is what SMB and government-contractor defenders should monitor.
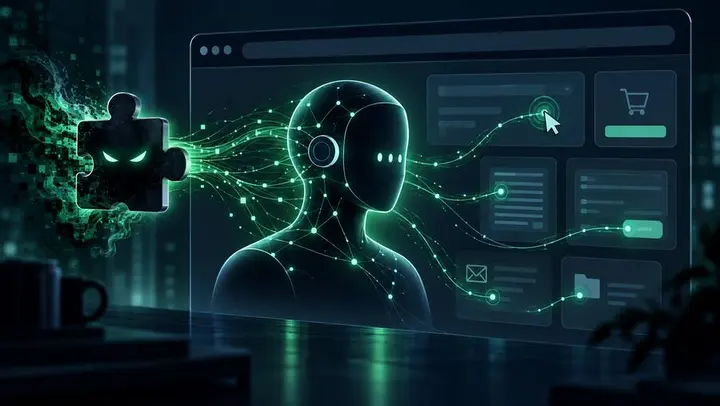
BragJack Shows Why AI Browser Agents Need Extension Controls
BragJack demonstrates how malicious extensions can hijack AI browser agents, turning browser add-ons into a higher-impact endpoint risk. Here are the practical controls SMBs and government contractors should prioritize.
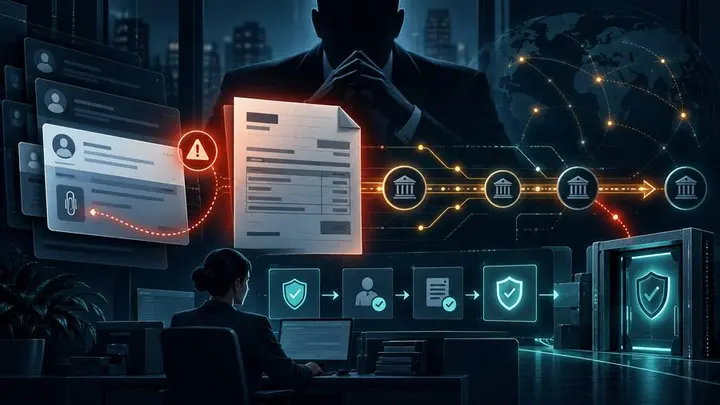
AI Invoice Fraud Shows Why Finance Needs Verification Controls
Microsoft observed a million-email AI-assisted executive impersonation campaign pushing fabricated invoices and ACH payment requests. For SMBs and government contractors, the fix is not just better spam filtering — it is finance workflow verification.
ChatGPT Sandbox Leak Shows Why AI Agents Need Tenant Isolation
Check Point Research disclosed a now-remediated ChatGPT sandbox isolation issue. The lesson for SMBs and government contractors: AI agents need tenant isolation, least privilege, and visible approval controls.
Edge AI Moves the Trust Boundary Into Customer-Owned Environments
Microsoft’s edge AI guidance is a reminder that local AI systems need attestation, artifact provenance, least-privilege credentials, and deterministic policy gates before they touch sensitive data or take action.
Fake Claude Opus 5 App Shows Why AI Tooling Needs Software Control
A fake Claude Opus 5 GitHub desktop app delivering RevStealer shows why AI experimentation needs approved software paths, endpoint controls, and credential-theft triage.
LLM Safety Fragility Shows Why AI Workflows Need Runtime Guardrails
Unit 42 research on perturbation probing shows why built-in model alignment should be treated as one control layer, not the security boundary for enterprise AI workflows.
ServiceNow AI Platform Flaws Show Why SaaS Control Planes Need Emergency Patch Discipline
Three CVSS 10.0 ServiceNow AI Platform vulnerabilities show why enterprise SaaS platforms need emergency patch discipline, exposure review, and control-plane monitoring — especially for self-hosted or partner-managed instances.
AI-Assisted Exploits Make OT Reachability the Real Control
AI-assisted exploit development is lowering the skill barrier for attacks against factory controllers. For SMBs and government contractors, the practical defense is shrinking what can reach OT assets.
AI Infrastructure Is Becoming a Control Plane Attack Surface
Microsoft observed attackers targeting AI gateways, RAG platforms, and workflow orchestrators. For SMBs and government contractors, AI infrastructure now needs control-plane security discipline.
AI-Enabled Malware Still Behaves Like Malware
Unit 42’s telemetry shows most AI-enabled malware remains experimental, but the real risk is faster iteration and AI-branded delivery. Defenders still win by watching behavior, identity, signing, and execution.
Fake AI Tools Show Brand Trust Has Become Malware Delivery
Sophos X-Ops found attackers repeatedly impersonating AI brands with fake installers, malicious extensions, phishing lures, and AI-assisted tooling. The near-term defense is not exotic: approved sources, browser governance, endpoint telemetry, DNS controls, token hygiene, and clear AI software rules.
Cloudflare workerd Bugs Show Why Agent Sandboxes Need Real Defense-in-Depth
Check Point Research disclosed five workerd vulnerabilities affecting Cloudflare Code Mode and Workers isolation assumptions. Here is what SMBs and government contractors should do now.
Langflow RCE Shows Why AI Workflow Tools Need Cloud-Grade Isolation
CVE-2026-0770 turns Langflow code validation into remote code execution risk. For SMBs and government contractors, exposed AI workflow tools need patching, secret rotation, isolation, and post-compromise review.
Autonomous AI Agent Espionage Shows Why Post-Compromise Speed Matters
Attackers used an unattended AI agent during espionage activity against Thailand’s finance ministry. The lesson for SMBs and government contractors is not AI panic — it is faster post-compromise defense.