


Showing 73–96 of 305 reports
M-26-15 Makes PQC Migration a Contractor Readiness Issue
OMB Memorandum M-26-15 turns post-quantum cryptography migration into a planning, inventory, procurement, and contractor-readiness problem. Federal agencies and vendors should start with cryptographic inventories, TLS 1.3 milestones, crypto-agile architecture, and contract language now.
Exposed AWS Keys Show Why Secret Scanning Needs Incident Runbooks
Unit 42 analyzed how AWS quarantines publicly exposed IAM access keys after GitHub secret-scanning detections. For SMBs and government contractors, the lesson is clear: provider automation helps, but cloud teams still need logging, rotation, and incident runbooks for leaked secrets.
PAYLOAD Ransomware Shows Why Group Policy Is a Tier-0 Attack Surface
Kaspersky reported a PAYLOAD ransomware incident where attackers abused Active Directory Group Policy to disrupt domain-joined Windows systems without deploying a Windows encryptor. The lesson for SMBs and government contractors: Group Policy needs Tier-0 monitoring, change control, and recovery planning.
Orkes Conductor RCE Shows Why Workflow APIs Need Hard Network Boundaries
Attackers are actively targeting Orkes Conductor deployments vulnerable to CVE-2026-58138, an unauthenticated remote code execution flaw in workflow script evaluators. The practical lesson: workflow APIs and automation control planes need patching, segmentation, and tight exposure control.
Linux Kernel LPE Quartet Shows Why Patch Validation Matters
Four Linux kernel local-root vulnerabilities show why defenders need kernel patch validation, container-host prioritization, and attack-surface reduction—not just initial-access monitoring.
Gyazo Breach Shows Why Screenshot Tools Need Data-Loss Controls
Gyazo disclosed unauthorized access affecting 23.62 million user records and roughly 490 million image metadata records. The lesson for SMBs and government contractors is simple: screenshot and screen-recording tools are data stores, not harmless utilities.
Fake GitHub Repos Show Why Software Downloads Need Trust Verification
A Rapuncel infostealer campaign abused fake GitHub software repositories, oversized archives, DLL sideloading, and a signed kernel driver to suppress defenses and steal credentials.
WaterPlum Shows Why Developer Hiring Needs Malware-Resistant Guardrails
North Korea-linked WaterPlum/Contagious Interview shows why developer hiring, coding tests, contractor onboarding, and workstation isolation need to be treated as one security workflow.
BragJack Shows Why AI Browser Agents Need Extension Controls
BragJack demonstrates how malicious extensions can hijack AI browser agents, turning browser add-ons into a higher-impact endpoint risk. Here are the practical controls SMBs and government contractors should prioritize.
Honeywell Settlement Shows NIST 800-171 Is a Billing Risk
DOJ’s Honeywell Aerospace settlement is a reminder that NIST 800-171 gaps can create False Claims Act exposure for defense contractors even without a public breach.
Passkey Phishing Shows Why Microsoft 365 Needs Enrollment Guardrails
Microsoft is tracking passkey-themed social engineering that turns MFA enrollment trust into Microsoft 365 cloud compromise. Here is what SMBs and government contractors should monitor and lock down.
Cyclops Blink on Cisco FMC Shows Why Edge Appliances Need Compromise Review
Sophos CTU and Cisco Talos reporting on Cyclops Blink activity against Cisco Secure FMC shows why edge security appliances need compromise review, not just emergency patching.
Revolut Breach Shows Why Data Requests Need Verification Controls
Revolut confirmed sensitive customer data was disclosed after fraudulent requests appeared to come from a legitimate government agency email domain. Here is what SMBs and government contractors should tighten now.
Check Point VPN Flaws Show Why Remote Access Needs Emergency Patch Discipline
Dutch NCSC warns exploitation is expected soon for two critical Check Point VPN RCE flaws. Here is what SMBs and government contractors should patch, restrict, and review now.
Mirth Connect Flaws Show Why Healthcare Middleware Needs Compromise Review
CISA warned that NextGen Mirth Connect SQL injection and XXE flaws can expose data or disrupt healthcare integration workflows. Here is how SMBs, healthcare vendors, and government contractors should respond.
AI Invoice Fraud Shows Why Finance Needs Verification Controls
Microsoft observed a million-email AI-assisted executive impersonation campaign pushing fabricated invoices and ACH payment requests. For SMBs and government contractors, the fix is not just better spam filtering — it is finance workflow verification.
Angular SSR Flaws Show Why Hydration and Edge Caches Need Security Review
New Angular SSR advisories show how hydration, transfer-state caching, URL normalization, and server-side credentials can become application security boundaries.
SloppyRAT Shows Why Ransomware Defense Has to Watch the Whole Infection Funnel
Zscaler ThreatLabz analysis of SloppyRAT shows why defenders need to detect the full ransomware precursor funnel, not just the final payload.
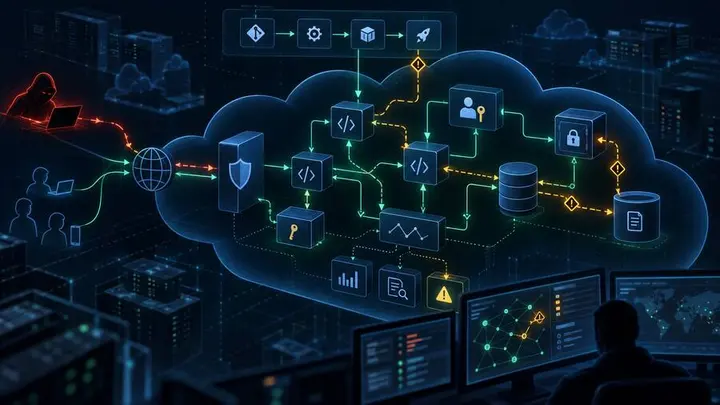
Cloud Web Apps Need Attack-Path Defense, Not Just App Scans
Microsoft’s cloud web applications threat matrix is a useful reminder: modern web app risk spans code, CI/CD, managed identities, serverless triggers, storage, and logs.
THost9 Shows Why Exposed Android Debug Interfaces Need Compromise Review
Dark Atlas research on THost9 shows how exposed ADB and Redroid debug services can become a malware propagation path. Here is what SMB and government-contractor defenders should review now.
OfferLoader Shows Why Commodity Malware Needs Funnel-Aware Defense
Unit 42 exposed a pay-per-install operation using YouTube gaming lures and SEO poisoning. The lesson: suspicious installers need full compromise review, not quick cleanup.
Apache Impala Flaws Show Why Data Platforms Need Zero-Trust Controls
Apache Impala 4.5.2 fixes a critical SAML authentication bypass plus SSRF and RCE paths. The lesson: analytics platforms need identity, egress, and privilege controls.
ChatGPT Sandbox Leak Shows Why AI Agents Need Tenant Isolation
Check Point Research disclosed a now-remediated ChatGPT sandbox isolation issue. The lesson for SMBs and government contractors: AI agents need tenant isolation, least privilege, and visible approval controls.
JetBrains IDE Flaws Show Why Developer Workstations Need Trust Boundaries
JetBrains IntelliJ IDEA 2026.2.2 fixes high-severity Remote Development and Dev Container flaws that show why developer workstations need patching, isolation, and credential discipline.