


Showing 145–168 of 305 reports
Azure Directory Dumps Show Why Identity Data Is Attack Infrastructure
A reported Azure and Entra directory exfiltration campaign shows why cloud identity data, service accounts, and org charts need defensive monitoring before attackers weaponize them.
Signed ClickOnce Shows Fake Interviews Are Now a Credential-Theft Delivery System
A fake Web3 interview chain used a signed ClickOnce app to deliver stealers and a RAT. Here is what SMBs and government contractors should change in endpoint, identity, and hiring-workflow defenses.
Dropcatch Domains Show Why Reputation Is Not Trust
Threat actors are buying expired domains with inherited reputation, backlinks, and traffic, then using them for redirects, scams, malware, and command-and-control. Here is what SMBs and government contractors should harden first.
CaptiveCrunch Shows Why Travel Wi-Fi Is an Identity Attack Surface
Zscaler reports that Midnight Blizzard operators are abusing hotel and conference Wi-Fi captive portals for Microsoft 365 credential theft, device-code phishing, and malware delivery. Here is what SMBs and government contractors should harden first.
HoneyMyte’s CoolClient Rootkit Shows Why Kernel Visibility Matters
HoneyMyte’s CoolClient backdoor now includes signed kernel-mode rootkit capabilities, raising the bar for driver monitoring, Defender exclusion review, and post-compromise endpoint validation.
JWR Phishing Framework Shows Why MFA Codes Are Now Live Targets
Cisco Talos documented JWR, a real-time phishing framework that lets operators steer victims through fake checkout and login flows while harvesting credentials, payment data, OTPs, identity documents, and device fingerprints. For SMBs and government contractors, the lesson is direct: MFA codes are n
Evooo1Bot Shows Why Exposed Linux and Edge Devices Are Still High-Value Targets
FortiGuard Labs documented Evooo1Bot, a Linux botnet combining Mirai-style DDoS with SSH brute forcing, SOCKS relay, credential sniffing, persistence, and exploit-driven infection of exposed devices.
Malware Crypting Services Show Why Behavioral Detection Matters
Recorded Future’s look at malware crypting services shows why SMBs and government contractors need behavioral detection, endpoint telemetry, and incident response—not just clean file scans.
Private Wireless Utility Networks Are Becoming OT Attack Paths
A CERT Polska follow-up on an energy-sector incident shows why private APNs, private LTE/5G, and cellular routers must be treated as OT attack paths — not inherently trusted connectivity.
Kong Mesh Vulnerabilities Show Why Service Mesh Security Needs Control-Plane Discipline
Fresh Kong Mesh/Kuma vulnerabilities touch service-mesh trust boundaries: admin token exposure, data-plane configuration disclosure, workload identity confusion, token interception, and control-plane DoS.
Gunra Ransomware Shows Why VPN Compromise Is an Incident, Not a Patch Ticket
Gunra ransomware activity tied to Fortinet VPN exploitation shows why edge-device compromise requires incident response: credential review, session validation, segmentation checks, and backup protection — not just patching.
CI Fortify Shows Why OT Isolation Must Be Engineered Before the Incident
New CI Fortify OT isolation guidance turns prepare-to-disconnect planning into an engineering test: can vital systems be isolated fast while essential services keep running?
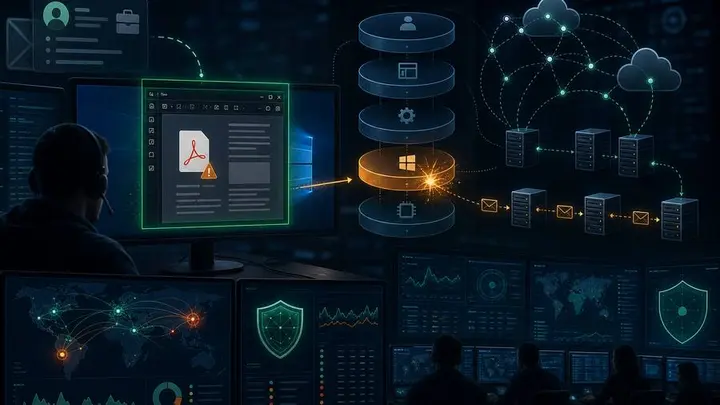
Lazarus Dream Job Campaign Turns Fake Recruiting Into a Windows Zero-Day Intrusion
Check Point Research reports a new Lazarus Operation Dream Job wave using fake recruiting lures, trojanized PDF tooling, Microsoft Graph/OneDrive C2, Roundcube relay infrastructure, and the patched CVE-2026-68820 Windows AFD.sys zero-day.
Deno Runtime Abuse Shows Why Developer Tooling Needs Security Governance
Sophos MDR observed attackers bringing the legitimate Deno runtime into intrusions to execute malicious JavaScript through less-monitored paths. Here is what SMBs and government contractors should monitor.
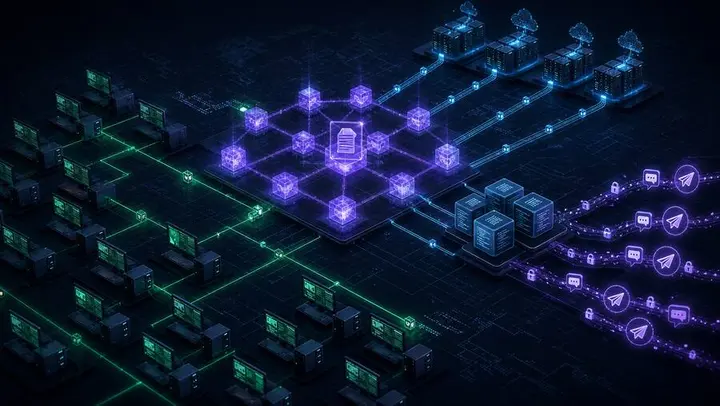
Aeternum Shows Why Blockchain-Based C2 Is a Practical Defense Problem
Aeternum uses Polygon smart contracts, GitHub staging, and Telegram exfiltration to make botnet command-and-control more resilient. Here is what SMBs and government contractors should watch for.
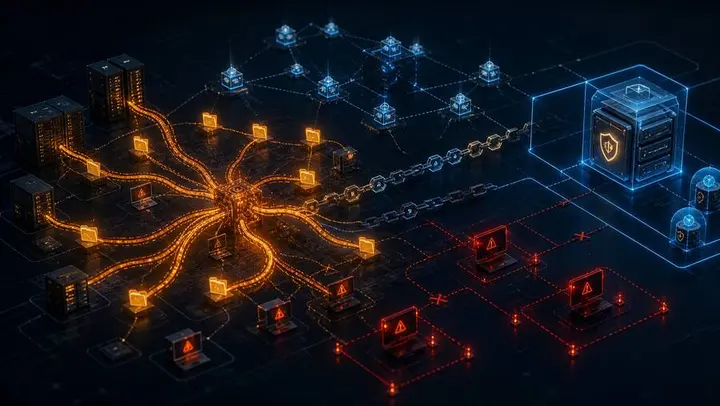
DeadLock Ransomware Shows Why Recovery Infrastructure Is Part of the Attack Surface
Microsoft’s DeadLock ransomware analysis shows why SMBs and government contractors need to protect backups, logs, identity, and recovery workflows before encryption starts.
UNC6671 Shows Why Helpdesk Vishing Is a Cloud Data-Theft Problem
Google Threat Intelligence reports UNC6671 is using helpdesk vishing, AiTM portals, and SaaS exfiltration across multiple extortion brands. Here is what SMBs and government contractors should do now.
VeloCloud Orchestrator RCE Shows Why SD-WAN Controllers Need Incident Response
CVE-2026-16812 is an actively exploited CVSS 10.0 command-injection flaw in on-premises Arista VeloCloud Orchestrator. For defenders, this is not just a patching issue — it is SD-WAN management-plane incident response.
MSI Router Command-Injection Cluster Shows Why Edge Devices Need Exposure Control
A fresh cluster of critical MSI Radix AXE6600 command-injection CVEs shows how consumer and prosumer edge devices can become root-level footholds when management features are reachable from untrusted networks.
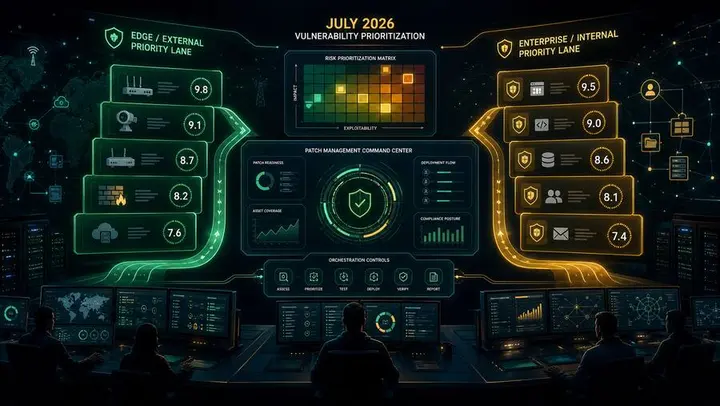
July CVE Data Shows Why Patch Priority Needs Threat Context
Recorded Future’s July 2026 CVE landscape shows a crowded exploitation picture: 85 high-impact vulnerabilities, heavy RCE exposure, public PoCs, and attackers still abusing old edge and application flaws. Here is how SMBs and government contractors should prioritize patching.
ExfilSquad Shows Why CRM and Portal Data Need Extortion-Ready Controls
ExfilSquad’s reported use of torrent-based leak distribution shows why CRM, helpdesk, public portal, and AI support data need stronger access controls, export monitoring, and extortion-ready incident response.
BdThemes Compromise Shows Why WordPress Plugin Risk Extends Beyond Code Updates
Wordfence reported a BdThemes supply-chain compromise where poisoned remote JSON turned WordPress admin notices into an attack path. Here is what SMBs and government contractors should check now.
Cloudflare workerd Bugs Show Why Agent Sandboxes Need Real Defense-in-Depth
Check Point Research disclosed five workerd vulnerabilities affecting Cloudflare Code Mode and Workers isolation assumptions. Here is what SMBs and government contractors should do now.
Langflow RCE Shows Why AI Workflow Tools Need Cloud-Grade Isolation
CVE-2026-0770 turns Langflow code validation into remote code execution risk. For SMBs and government contractors, exposed AI workflow tools need patching, secret rotation, isolation, and post-compromise review.