


Showing 49–72 of 401 reports
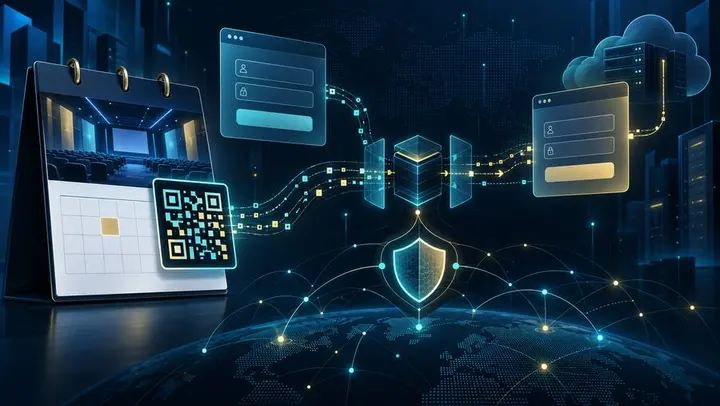
UAT-11985 Shows AI-Assisted Phishing Is Now Real-Time Account Takeover
Cisco Talos reported an APT campaign using AI-assisted event lures, malicious QR codes, and real-time Google AitM phishing. The defensive answer is phishing-resistant MFA, invitation verification, and identity telemetry that connects clicks to sessions.
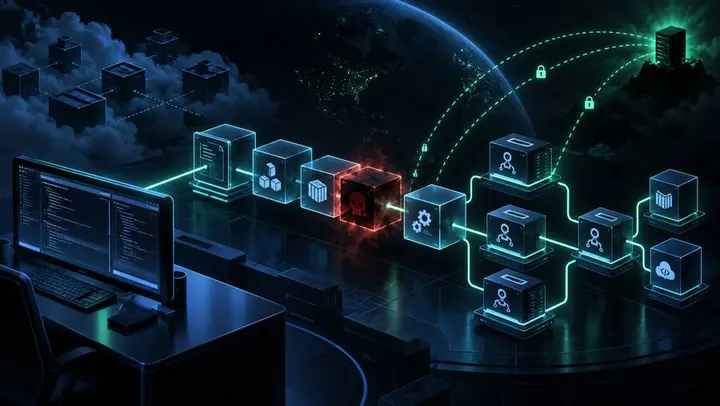
Trojanized Terraform Providers Show IaC Pipelines Are Developer Endpoints
Zscaler ThreatLabz detailed a suspected TraderTraitor campaign using a fake Terraform provider to launch cross-platform malware. The practical lesson: infrastructure-as-code plugins run on developer and CI/CD systems, so they need endpoint controls, provenance checks, and egress monitoring.
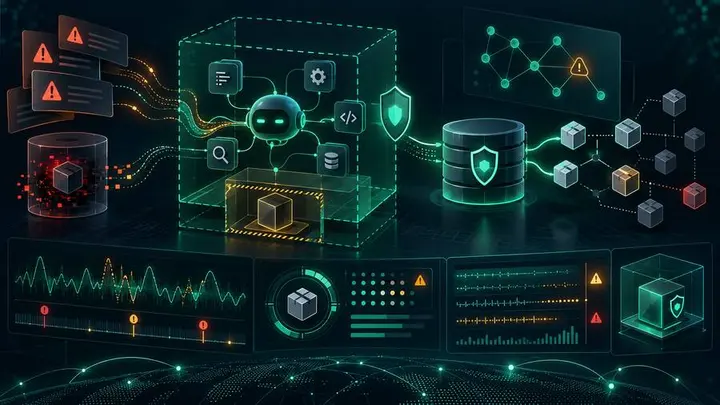
Malicious AI Agent Skills Turn Prompt Instructions Into Supply-Chain Risk
VirusTotal found thousands of malicious AI agent skills, many carrying the attack in plain-language instructions rather than code. The defensive move is to review skills like software, sandbox agents, and monitor outbound behavior.
ARTEX AI Bank Attacks Show Agentic Tools Are Now an Incident-Response Problem
CrowdStrike found ARTEX configuration files and Claude Code histories tied to attacks on South Korean financial organizations. The lesson for defenders is not AI panic—it is faster triage, stronger application logging, and tighter controls around data-access workflows.
Ransomware Negotiation Arrest Shows Why Extortion Response Needs Guardrails
A ShinyHunters-linked arrest report is a reminder that ransomware negotiation is not just a tactical service. SMBs and government contractors need clear authority, evidence handling, vendor vetting, and legal guardrails before extortion starts.
Internet Scanning Turns Open Ports Into Threat-Intel Pivots
VirusTotal added daily public IPv4 scanning data to IP reports, including ports, banners, services, versions, fingerprints, and port history. The practical lesson: open ports are weak signals alone, but service metadata can turn exposure into useful threat-intel pivots.
AnyDesk Linux Exploit Shows Remote Access Tools Need Exposure Controls
A public exploit for a pre-authentication AnyDesk Linux flaw shows why remote access tools need patching, exposure controls, inventory, and monitoring—not just user approval prompts.
Go Security Release Shows Why HTTP/2 and Proxy Paths Need Patch Discipline
Go 1.27.2 and 1.26.9 fix 15 security issues across HTTP/2, reverse proxy behavior, TLS, templates, multipart parsing, and module checksum trust. The operational lesson is simple: language-runtime patches are infrastructure patches.
Midnight Mimosa Shows Why Cheap Android Devices Need Supply-Chain Controls
Bitdefender found firmware-level Android malware preinstalled on low-cost devices. For SMBs and government contractors, the lesson is procurement discipline, segmentation, mobile access policy, and monitoring for proxy-like behavior.
AI-Analysis Evasion Shows Why Malware Triage Needs Prompt Boundaries
Cisco Talos found malware families embedding natural-language instructions meant to steer AI-assisted analysis. The lesson for defenders: treat sample text as evidence, not instruction.
Web3 C2 Shows Why Build Pipelines Need Egress Controls
Unit 42 warns that supply-chain malware is using Web3 infrastructure to hide command-and-control while stealing cloud credentials from developer workstations and CI/CD runners.
AI Agent Swarms Turn Security Basics Into Cost Controls
Cisco Talos warns that agentic attacks can compress reconnaissance, probing, social engineering, and exploitation. The practical defense is to make every attacker step more expensive through identity hardening, telemetry, throttling, and rehearsed response.
Q3 Attack Trends Show Trusted Paths Are Becoming the Real Target
ASEC’s Q3 2026 attack-techniques report shows attackers chaining perimeter devices, supply-chain paths, and identity workflows. Defenders should map and monitor trusted paths, not just patch isolated CVEs.
FortiBleed Shows Why VPN Credential Compromise Needs Full Incident Response
The FBI and Secret Service warn that FortiBleed remains active against Fortinet firewall and VPN environments. The key lesson: exposed edge-device credentials require incident response, not just patching and password resets.
GitHub Enterprise SSRF Shows Why Secret Scanning Needs Network Guardrails
GitHub patched CVE-2026-96890, a high-severity GitHub Enterprise Server SSRF in secret-scanning validity checks that could potentially lead to appliance RCE. Defenders should patch GHES and restrict appliance egress.
Blinder Tunnel Shows How Developer Trust Becomes Critical Infrastructure Risk
Unit 42 reports an Iran-nexus campaign using fake Dubai Airports recruitment lures, weaponized Visual Studio projects, GitHub-based command-and-control, and tunneling tools against Iraqi critical infrastructure. The lesson for SMBs and government contractors: developer workflows need the same identi
Browser Detection and Response Shows Why the Browser Is Now a Security Blind Spot
Zscaler argues that browser-based attacks increasingly evade traditional endpoint and network controls because key behavior happens inside the browser. Defenders should treat browser telemetry, extension control, clipboard/file movement, identity flows, and isolation policy as part of the detection-
Apache Struts REST Plugin Flaws Show Why Legacy Java Apps Need Exposure Review
Apache disclosed four Struts vulnerabilities on October 5, including an important REST plugin issue that can exhaust Java heap memory and an OGNL injection path in the legacy RESTful action mapper. Defenders should inventory exposed Struts apps, patch to 6.12.0 or 7.4.0, and verify mapper/plugin usa
ClingSTUN Shows Why IoT Edge Devices Need Real Egress Monitoring
Fortinet’s ClingSTUN research shows how compromised IoT and edge devices can abuse public STUN infrastructure to become proxy backdoors. SMBs and government contractors should treat exposed firmware, unexpected UDP/STUN traffic, and unmanaged edge devices as a real incident-response priority.
Apache Thrift 61-CVE Patch Shows Why RPC Frameworks Need Inventory
Apache Thrift 0.25.0 fixes 61 vulnerabilities across multiple language bindings. Defenders should treat this as an RPC exposure and software-inventory problem, not just another library bump.
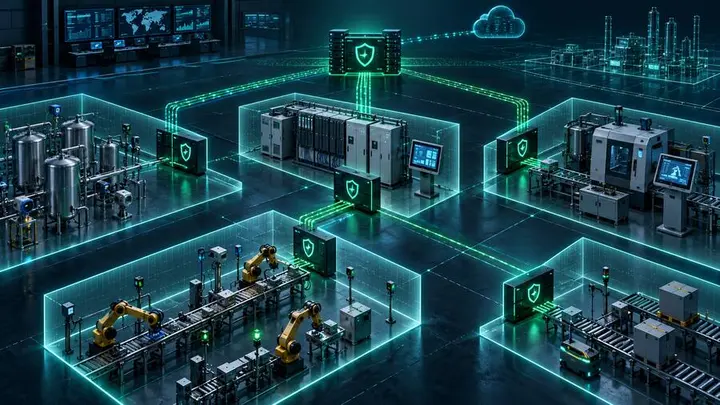
NIST OT Zero Trust Guidance Shows Segmentation Must Reach Below Level 3
NIST SP 800-82r4 brings zero trust into OT guidance, but defenders need local segmentation and access controls below Purdue Level 3 where controllers, HMIs, and engineering authority live.
Milk Dragon Shows Social Commerce Phishing Needs Identity and Payment Controls
Group-IB’s Milk Dragon research shows how shopping-discount lures on social media can become adversary-in-the-middle phishing and payment-card theft. SMBs and government contractors should treat social commerce fraud as an identity, brand, and payment-risk problem — not just user awareness.
Cisco SD-WAN Auth Bypass Shows Edge Control Planes Need Emergency Review
Cisco says CVE-2026-76504 is being actively exploited against Catalyst SD-WAN Manager, giving unauthenticated attackers admin-level API access. Edge management systems need emergency patching, exposure reduction, and compromise review.
Ransomware Data Theft Surge Shows Why Exfiltration Defense Comes First
Zscaler ThreatLabz reports ransomware data theft surged 275.8% year over year, with government, healthcare, education, and utilities facing larger exfiltration events. Defenders need controls that stop data movement before encryption begins.